With immediate effect, netfiles GmbH, a provider of virtual data rooms and highly secure data exchange solutions, is adopting passkey authentication as an additional and convenient option to log in. Thanks to passkeys, users no longer have to remember passwords and can keep their user accounts reliably protected against phishing and cyber-attacks.
It has long been understood that logging in with a password is a not particularly secure way of accessing applications, websites, and online shops. Why? Because there is a serious danger that passwords could be intercepted or become known due to data breaches.
Troublesome chore
Microsoft reported 4,000 password attacks per second last year–up from “only” 115 attacks in 2015
Moreover, this threat is constantly on the rise: Microsoft alone reported 4,000 password attacks per second last year–up from “only” 115 attacks in 2015.
For users, it is also a troublesome chore to think up passwords that are hard for others to guess – and then remember them. This explains why simple passwords are used all too often, and why one and the same password is often used for multiple services.
Security and data protection
“We attach supreme importance to security and data protection, because our customers use netfiles mostly to exchange confidential, mission-critical, and/or personal information,” explains Thomas Krempl, Managing Director of netfiles GmbH.
“This being the case, it is crucial to make the login procedure too as secure as possible. That is why we are now one of the first data room providers to support passkeys as an exceptionally secure but also simple and convenient login alternative.”
How does passkey authentication work?
Secret private key is stored either on the user’s computer or mobile device, under password manager
Passkeys are based on pairs of cryptographic keys. When a user registers with a web service, two keys – the passkeys – are generated. A secret private key is stored either on the user’s computer or mobile device, under their password manager, or on their FIDO2 security key (a hardware token similar to a USB stick). In contrast, the online service only stores the public key.
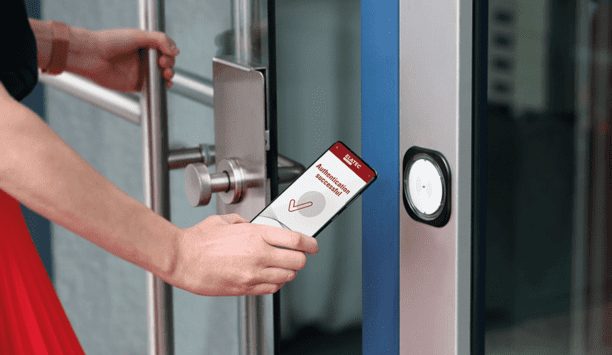
For all future login attempts, the web service issues a “challenge” that can only be solved correctly with the private key. Users then authenticate themselves with a fingerprint, via facial recognition, with their FIDO2 stick or by entering the device PIN. In the background, the correct answer is then forwarded to the web service and the user is granted access to his or her account. The advantage? Since no passwords have to be transmitted via the Internet and users no longer have to remember their passwords, passkeys provide robust protection against data theft and are quite simply easier to use.
netfiles products
With immediate effect, customers can use passkey authentication to log in to all netfiles products:
- netfiles Deal Room – a virtual data room for due diligence audits and company/real estate transactions
- netfiles Board Room – for meeting management and board-level communication
- All netfiles data exchange solutions.