Security service

Gunnebo Safe Storage is expanding its reach through a new collaboration with Carriquiry Sécurité, with the two companies set to showcase their collaboration at Expoprotection 2026. Product showcase at Expoprotection 2026 The exhibition will see Carriquiry Sécurité present the Chubbsafes Vega and DuoGuard safes alongside the Gunnebo Encry™ lock on stand C094, Hall 1. The display marks the first opportunity for visitors to discover the products through the new c...

Detection Technology, a global pioneer in X-ray detector solutions, announced AVA Zero, a new dual-energy line detector for entry-level urban security systems. AVA Zero is designed to help security scanner manufacturers lower system costs while maintaining the high image quality needed to ensure the safety of people. Design, features and functions Targeted at transmissive X-ray security scanners for applications such as metros, train stations and critical structures, AVA Zero combines a strea...
Arctic Wolf®, the cybersecurity and AI company, today at the 2026 Security Operations Summit announced SwarmView™, a new capability that brings the power of the Swarm of Experts™ directly to customers, providing unprecedented visibility into how the Aurora Agentic SOC® investigates, validates, and responds to modern threats at machine speed. By providing a direct view into how AI agents and human experts work together throughout every investigation, SwarmView gives organizati...

Gunnebo Entrance Control is at SKYDD 2026 to showcase its latest pedestrian entrance security technologies and explore how different approaches to entrance control can support the needs of smart buildings. Visitors to stand A18:33 at Nordic’s leading trade fair for security will be able to see the SpeedStile FLs UC, SpeedStile FP Glide and NexGate, with each offering a different approach to managing pedestrian movement and controlling access. Tailored to specific requirements “Cho...

Colt Technology Services (Colt), the digital infrastructure company, announces it is the first European-based provider to integrate its last-mile connectivity services with the Equinix Fabric Marketplace. Fabric Marketplace simplifies access to services across the world’s largest digital business ecosystem. It gives enterprises a single destination to quickly discover, learn about and connect with service providers that can enhance their distributed networking deployments for multicloud a...

Verisure, the provider of professionally monitored security services by customers served, has been recognized as one of the Fortune 100 Best Companies to Work For™ in Europe for 2026. This marks Verisure's inaugural inclusion in the prestigious list. With more than 30,000 colleagues across 18 countries, Verisure has built a high-performance, people-focused culture centred on trust, inclusion and growth. Monitored security services This commitment has earned widespread recognition, inclu...
News

HID, a pioneer in trusted identity solutions, has joined the FIDO Alliance Board of Directors to help accelerate the shift to passwordless authentication across the enterprise. Sean Dyon, Vice President of the Authentication Business Unit, will serve as the company’s Primary Board Delegate. HID joins the Board with decades of leadership across physical and digital identity, bringing a real-world perspective to the Alliance’s work advancing interoperability, lifecycle management and deployment at scale. “HID has been a longtime and valuable contributor to the FIDO Alliance, and we're pleased to welcome them and Sean Dyon to our Board,” said Andrew Shikiar, Executive Director and CEO of the FIDO Alliance. “As enterprises scale passkey deployments, HID's perspective on converged physical and digital identity will help us bring the security and usability benefits of passkeys to a wider range of environments.” Digital identity work together The FIDO Alliance enables identity technologies that put trust and simplicity at the center of interactions among people, services and devices, including the open standards behind passkeys and passwordless sign-in. Passkeys built on FIDO standards are phishing-resistant because they never transmit reusable passwords and bind authentication to a specific device and origin. The Alliance's board shapes its strategy, standards and certification priorities, and HID will contribute to that work through board governance and strategy discussions, collaborating with other industry leaders to advance more secure, interoperable authentication. HID’s appointment comes as passkey implementation moves from limited pilots to wider deployments, a shift that has brought attention and scrutiny to interoperability, lifecycle management and how physical and digital identity work together at scale. FIDO-certified authenticators A FIDO Alliance member since 2015, HID has contributed to working groups spanning FIDO2, digital credentials and consumer deployment, and has partnered with the Alliance on research into identity security and convergence. HID also builds FIDO-certified authenticators and authentication platforms trusted by enterprise and government users worldwide. This expertise will be valuable as the Board guides a broader shift already underway in the market: 93% of organizations are now at some stage of passkey adoption and 65% report high or expert technology familiarity, according to the FIDO Alliance and HID report. On the Board, HID will draw on that dual vantage point to represent enterprise priorities around converged identity, lifecycle management and multi-vendor interoperability as passwordless adoption accelerates from pilot programs to full-scale deployment. Lifecycle management and interoperability "As enterprises scale passkeys and passwordless authentication, the standards behind them must address the real-world challenges of deployment, lifecycle management and interoperability," said Sean Dyon, Vice President of the Authentication Business Unit at HID. “The FIDO Alliance has been instrumental in advancing open standards for secure, passwordless authentication, and we are proud to contribute to that work. Because our business spans both physical and digital identity, we understand these challenges across the full range of how people authenticate. That is the perspective we intend to bring to the table.”

Absolute Security, a pioneer in Autonomous Cyber Resilience, has acquired Phoenix Technologies’ FirmGuard, a UEFI BIOS firmware security, management, and networking service. FirmGuard extends Absolute Persistence®, the patented firmware-embedded technology behind the Autonomous Cyber Resilience Platform. This acquisition adds deeper visibility, integrity verification, posture management, continuous patching, and compliance enforcement for endpoints, AI workstations, and autonomous agents. Together, they will provide the firmware foundation AI-driven enterprises need to defend against threats, reduce risk, prevent agents from going rogue, and minimize disruption. AI-driven enterprises “AI-driven threats and fragility are disrupting enterprises from the cloud to the endpoint. Full resilience requires visibility, control, security, and recovery capabilities in the device hardware — a unique and exclusive location only Absolute occupies,” said Christy Wyatt, President & CEO, Absolute Security. “For more than 30 years, we have led the market in helping customers withstand cyberattacks and IT failures and recover from operational breakdowns. Our strengthened platform will help security and risk leaders confidently accelerate and protect AI initiatives against threats, complexity, and downtime.” Advanced AI workstations Research shows that firmware and hardware attacks are rising, and 80 percent of IT and security decision makers say AI will accelerate exploitation2. Yet 60 percent delay firmware updates, and more than half report firmware FOMU (Fear of Making Updates)3. Because firmware boots before the OS, it is essential for management and recovery, and a prime target for attackers, who can use it to evade security tools and persist undetected. Firmware security is now a strategic imperative for Chief Information Security Officers (CISOs). Enterprise CISOs can quickly activate Absolute across endpoint fleets and advanced AI workstations. Through exclusive partnerships with top OEMs Dell, HP, and Lenovo, Absolute is embedded in the firmware of 600 million endpoint devices. This gives customers an unbreakable connection to the firmware to manage and secure devices and applications and restore them to an operational state at boot, even when the OS is corrupted or crashing. Absolute’s AI focus has also led to trusted collaborations with NVIDIA and HP, extending these capabilities to advanced AI workstations and autonomous agents. Data-wipe options Absolute will integrate its deep firmware and UEFI capabilities to deliver a consolidated, best-in-class solution for integrity, security, resilience, and full device control, from the moment devices power on. In the first phase, customers can expect: broader below-the-OS management, continuous firmware integrity and patching, expanded data-wipe options, one firmware-to-cloud console. “We built FirmGuard to make firmware protection simple and secure. Absolute has proven its firmware-embedded platform can do this at enterprise scale,” said Gerard Moore, President & CEO, FirmGuard. “With FirmGuard integrated into Absolute, customers can remain confident their AI devices will stay secure, compliant, and running, so when something goes wrong, downtime will not become a business loss.” Boston Meridian Partners acted as exclusive financial advisor to FirmGuard through the completion of the acquisition.

Starburst, the enterprise intelligence platform for governed data and AI, announces the appointment of Kerman Lau as Chief Financial Officer (CFO). In this role, Kerman will lead Starburst’s finance organization and partner with the leadership team on growth strategy, operating performance, capital allocation and long-term value creation. Lau joins Starburst with more than 25 years of experience spanning high-growth software companies and large global enterprises. Most recently, he served as CFO of Moveworks, where he helped scale the company through a period of rapid growth, the emergence of generative and agentic AI, and its acquisition by ServiceNow. Measurable business outcomes Throughout his career, Lau has focused on building high-performing finance organizations, using technology and data to improve decision-making, and helping companies translate strategy into measurable business outcomes. A consistent thread across his career has been people: his roles have grown out of trusted relationships and he credits talented, passionate teams as the common factor behind the companies he has helped scale. “AI is reshaping how companies operate, and it’s also changing what it takes to build and scale a great technology company,” said Justin Borgman, co-founder and CEO of Starburst. “Kerman has been through that journey before. He knows how to invest aggressively in the opportunities that matter while building the financial discipline needed to scale, and he understands the enormous opportunity in front of us as data becomes the foundation for enterprise AI. I’m excited to have him as a partner for Starburst’s next chapter.” Accelerating AI adoption As enterprises accelerate AI adoption, agentic workloads are multiplying alongside human ones, and access to trusted, governed data and business context is becoming increasingly critical. Starburst gives organizations secure, governed access to data wherever it lives, helping AI platforms, applications and agents move from pilots to production without requiring enterprises to first consolidate all of their data into a single platform. “People are the most important factor in my decision to join Starburst. Every company I’ve been part of has started with a people connection and that connection is what makes you want to take a bet on a new opportunity. From my first conversations with Justin and the leadership team, I felt we could build a great partnership and accomplish something meaningful together,” said Lau. Highest-growth opportunities “Starburst is also in the sweet spot of one of the biggest shifts happening in enterprise technology. Starburst already gives people high-performance, governed access to their data. Agentic workloads need the same things, plus business context a human naturally brings to every query. That’s exactly what we’re building and I believe Starburst is incredibly well positioned to be the gateway for any workload, human or agentic, to reach the data it needs.” As CFO, Lau will work closely with Starburst’s leadership team to align investment with the company’s highest-growth opportunities, strengthen operating performance and help guide the company through its next stage of scale. His experience navigating competitive technology markets and periods of rapid change will help Starburst balance investment and growth as the enterprise AI market continues to evolve.
HackerOne, a pioneer in Continuous Threat Exposure Management (CTEM), today released its 10th annual HackerOne Security Research Report, revealing that on the H1 Platform, the backlog of validated, unresolved vulnerabilities grew 131% in two years, even as average resolution time improved 54%. This year's report, Exposure Debt: The Next Challenge in Cybersecurity, introduces the urgent challenge security teams are grappling with in the race to stay ahead of attackers. AI has changed what security researchers can find. In skilled hands, advanced models are surfacing authorization flaws and multi-step attack chains that traditional scanners often miss. Organizations are responding: the average resolution time improved 54% this year, but discovery is outpacing remediation, and the gap between them continues to widen. Every vulnerability an organization knows about and hasn't fixed is a risk it already owns and hasn't paid down. That's Exposure Debt, and it grew 131% in just two years. Sensitive information disclosure Key findings from the report include: Exposure Debt is compounding: Despite the fastest remediation speeds recorded on the H1 Platform, the backlog of known, unresolved findings has still grown 131% over the past two years. Security leaders are feeling the pressure: 75% of surveyed security leaders said their organizations formally track exposure debt, and nearly 70% confirmed that validated findings are entering their systems faster than their teams can fix them. AI vulnerabilities are shifting as systems become more connected: System Prompt Leakage reports increased 557% year over year, Misinformation rose 455%, and Improper Output Handling increased 264%. Prompt injection and sensitive information disclosure continue to account for the largest share of AI vulnerability reports on the platform. Bug bounty programmes “AI is changing both sides of the security equation. It’s helping researchers find vulnerabilities faster and go deeper, while representing entirely new attack surfaces for them to test,” said Kara Sprague, CEO of HackerOne. “At the same time, nearly 70% of security leaders say findings are piling up faster than their teams can address them. Fixing got faster. It still lost ground. The constraint is no longer discovery; it is everything between a report arriving and a risk being resolved.” Additional notable findings from the report include: Researchers have incorporated AI into their workflows: 85% of surveyed researchers are actively upskilling in AI, with nearly three-quarters self-reporting a meaningful increase in valid findings. Complexity is the new frontier: 68% of surveyed researchers have shifted toward higher-complexity, higher-bounty bugs as AI changes how and where researchers spend their time. Remediation is faster than ever: Across HackerOne programmes, organizations have cut average resolution time from 135 days to 62 days, a 54% improvement in just two years. Researchers earned a record $89 million from July 2025 to June 2026: Organizations running bug bounty programmes on the H1 Platform awarded $89 million to security researchers, an 18% increase over the prior year and the highest annual total in the platform’s history. Highest annual total “AI hasn’t replaced how I think as a security researcher. It’s changed how much ground I can cover,” said Douglas Day, a top-earning security researcher on HackerOne. “I’ve automated parts of my research process that used to take hours, which gives me more time to focus on the vulnerabilities that require creativity, context, and an understanding of how systems actually work. The researchers who get the most out of AI won’t be the ones who simply turn it on. They’ll be the ones who know how to guide it, question it, and recognize when it has found something worth pursuing. The most valuable skill in the age of AI will be the ability to be flexible and adapt to new tools and technologies as they become available.”

Resilience, value retention, and insurability are among the key requirements for modern logistics facilities. At BUILDINX, taking place November 17-19, 2026, in Dortmund, WAGNER Group GmbH will demonstrate how preventive fire protection solutions help meet these requirements and minimize risks at the earliest stage. Visitors can find WAGNER at booth 5. B50. Fire protection requirements for logistics facilities are diverse: Automated storage and material flow systems, high-value goods, and new risk scenarios involving battery technologies and hazardous materials call for solutions that go beyond reactive measures. Systems are needed that detect fires at the earliest possible stage, proactively reduce risks, and ensure the long-term availability of critical operations. Fire protection solutions This is precisely where WAGNER comes in. The company develops fire protection solutions for high-availability logistics, production, and infrastructure sites. At the trade show, WAGNER will demonstrate how highly sensitive early fire detection, intelligent extinguishing technologies, and active fire prevention help avoid business interruptions over the long term. WAGNER will present active fire prevention live on site. Visitors to the booth can experience how an oxygen-reduced atmosphere prevents fires from starting. For the first time, BUILDINX will also focus on the highly topical issue of data centers. Against this backdrop, WAGNER will showcase its holistic fire protection solutions for business-critical infrastructure and present the new TITANUS REX® aspirating smoke detector—an innovative solution for highly precise early fire detection in demanding environments of this kind. For early fire detection in 19-inch equipment such as server and control cabinets, WAGNER offers TITANUS RACK·SENS®, a space-saving solution developed specifically for use in open ventilated, open non-ventilated, and closed climate-controlled cabinets. Operating specialized facilities Safely planning, permitting, and operating specialized facilities that handle hazardous materials presents particular challenges for warehouse operators, investors, and project development professionals, including with regard to fire protection. WAGNER will therefore participate in the BUILDINX session “Specialized facilities for hazardous materials: Requirements for construction, permitting, and protection.” Dirk Band, Head of Sales at WAGNER, will discuss the specific challenges and potential solutions for protecting hazardous materials warehouses with industry experts from Rhenus Logistics and Fabrikon on the first day of the trade show at 1:10 p.m. in the BUILDINX FORUM, Hall 5. The panel will focus on permitting, risk management, and appropriate fire protection measures for facilities with a higher risk profile. The expert panel will thus broaden the perspective from individual buildings to the resilience of entire logistics and supply chains—an aspect that is becoming increasingly important, particularly for hazardous materials facilities and security-critical logistics sites. Strengthen site resilience The importance of resilient protection strategies is particularly evident in defense logistics. As Europe’s defense industry expands, demand is growing for manufacturing, storage, and logistics facilities serving the defense sector. At the same time, requirements for the safety and availability of these critical infrastructures are increasing. At sites where sensitive electronics, hazardous materials, lithium-ion batteries, or essential supplies are stored, protecting the building alone is not enough. Fires can have a significant impact on operations and supply chains. Preventive fire protection solutions help identify risks at an early stage, minimize business interruptions, and strengthen site resilience over the long term. “The resilience of critical defense supply chains begins with preventive protection for storage, production, and infrastructure sites. The key is to identify risks early and prevent fires from starting wherever possible. This is precisely where WAGNER’s preventive, holistic fire protection solutions come in,” explains Dirk Band.

Global cybersecurity pioneer DigiCert has been the victim of a recent cyberattack. This is a major concern in the cybersecurity industry, as attackers were able to gain access to the issuance of 60 Extended Validation (EV) Code Signing certificates in a clever social engineering scheme. The attack started on April 2 when a sophisticated threat actor reached out to DigiCert’s support system through a Salesforce-based chat system. The threat actor appeared to be a customer, requested technical assistance, and eventually sent a ZIP file, claiming to be a message from a screenshot of an error. Major containment failure An “.scr (screensaver) file” was found in the archive of the file. On Windows, the system runs or stores .scr as native code. DigiCert’s endpoint defences thwarted the first four attempts, but at the fifth attempt, the attackers were able to get past the security via the support analyst’s workstation, giving them a foothold. DigiCert was able to isolate the first compromised machine (ENDPOINT1) within 24 hours A later investigation found a major containment failure. DigiCert was able to isolate the first compromised machine (ENDPOINT1) within 24 hours, but the attackers had already pivoted to an additional machine (ENDPOINT2). The second compromise was not discovered for 10 days, during which time the hackers were able to move freely about his company’s internal tools, from April 4 to April 14. First compromised machine The hackers took advantage of a “view-as-customer” function as part of the support portal. The developers created this tool for troubleshooting purposes, but it inadvertently provided the codes for the initialization of accepted, but not delivered, EV Code Signing orders. The attackers were able to steal these codes and then: Activate legitimate certificates in their own names. Bypass the rigorous identity verification usually required for EV status. Sign malicious software with “trusted” credentials that bypass Windows SmartScreen and antivirus filters. Stealing sensitive information The stolen certificates have been identified as part of the “Zhong Stealer” malware family by security researchers. This “stealer-RAT” combination is used to steal sensitive information and cryptocurrencies. A single e-crime group tied to the Chinese government appears to be using the stolen certificates known as GoldenEyeDog (APT-Q-27). Since then, DigiCert has canceled all 60 affected certificates, and the team has made emergency security upgrades: Feature Removal: Support staff can no longer view initialization codes. Identity Hardening: MFA teams have tightened the requirements, and the system administrators have disabled Okta FastPass for support portals. IP Blocking: The security team has blacklisted seven attacker-controlled IP addresses. Security professionals are encouraged to immediately update their Certificate Revocation Lists (CRL) and OCSP responders. Users should conduct a security audit of any internal “allow-lists” to make sure that none of the 60 revoked DigiCert certificates are being unwittingly trusted. Digital supply chain This incident is part of a pattern that experts say is becoming more common: Attackers are exploiting the human component of the digital supply chain, which threatens the trust in the internet globally. Upcoming Maintenance DigiCert has a scheduled maintenance window starting Saturday, May 9, 2026: Time: 22:00 – 24:00 MDT (Sunday, May 10, 04:00 – 06:00 UTC). Impact: Signing services (like PrimoSign) and certificate issuance APIs may be temporarily unavailable.

Expert commentary
Physical security isn’t a one-time project or a static system. It’s a dynamic, ongoing process and program that requires constant attention and management to remain effective. While the initial implementation of a security system — what we often call Day 1 — is critical, the ongoing maintenance, service, and adjustments made after systems are operational, or Day 2, are equally essential. Security program long-term Organizations that fail to focus on post-occupancy security operations risk falling victim Organizations that fail to focus on post-occupancy security operations risk falling victim to a phenomenon known as "program drift," where systems and policies gradually deviate from their intended standards over time. To manage your security program long-term, you often need an outside perspective. By engaging a security partner to provide managed services, organizations can achieve a strategic solution for maintaining their security programs' integrity, effectiveness, and efficiency over the long term. Let’s look at the reasons why. Moving beyond Day 1 Day 1 is the milestone moment when a security system is launched — whether it’s a new system, an upgraded access control platform, or a transition to advanced surveillance technology. On this day, all components align with established policies and standards. Yet, Day 1 is only the beginning of a security program's lifecycle. What happens on Day 2 and beyond is often where the real work begins. Without a robust plan for ongoing service and maintenance, security systems can quickly fall out of compliance. Policies become outdated, configurations drift, and vulnerabilities emerge. This gradual degradation — program drift — occurs not due to neglect but as a natural result of decentralized management; competing operational priorities; and the lack of dedicated, knowledgeable resources to oversee the systems. Avoiding program drift Drift is particularly pronounced in physical security because, unlike other building systems Program drift occurs when a security program’s elements — such as access controls, camera placements, or intrusion detection settings — gradually become misaligned from their intended standards. Think of a straight line representing perfect compliance on Day 1. Over time, various factors push individual components off this line. Left unchecked, these deviations accumulate, leading to significant vulnerabilities and deferred remediation costs that would be much easier to manage and predict with a more proactive approach. Drift is particularly pronounced in physical security because, unlike other building systems such as lighting or HVAC, security measures are often viewed as inconveniences. Even when systems function as designed, features like turnstiles, visitor management, or additional access controls may face pushback for being "in the way" of daily operations. This resistance and the Day 2 problems that often result — along with the lack of centralized oversight — exacerbate the risk of misalignment and ongoing inefficiencies. Why centralized post-occupancy management matters Post-occupancy management is critical for maintaining the long-term health of a security program. Facility managers, who are often tasked with overseeing security systems, may lack the technical expertise or bandwidth to handle the complexity of modern security infrastructure. Partnering with dedicated professionals to help meet these responsibilities ensures systems are managed effectively and vulnerabilities are addressed proactively. It also helps improve system availability and uptime, accelerate break/fix response and resolution times, lower ownership costs by reducing unnecessary and repeat service dispatches, and achieve a more consistent end user experience. Moreover, centralized management provides a consistent framework for handling security systems across multiple sites. This consistency is vital in preventing Program Drift, ensuring that local variations or individual decisions do not undermine the organization’s overall security posture. The case for managed services Hiring outside consultants offers a proactive and professional approach to mitigating program drift Hiring outside consultants offers a proactive and professional approach to mitigating program drift. Specialized providers have the expertise, tools, and resources to manage complex security systems effectively and ensure those systems remain aligned with organizational policies and performance expectations. By acting as a dedicated external resource and interfacing regularly with your security team, your consultant can help you build, manage, and optimize a variety of services that help keep your program on track. These services range from system health and availability management (break fix); move, add change management; system configuration administration; and program/project management offices. Key benefits in the following areas Let’s look at how a managed services a partner can yield key benefits in the following areas: Standards compliance. Centralized management ensures that security systems and processes remain in compliance with established policies and standards, reducing vulnerabilities caused by ad hoc changes or decentralized management. Operational efficiency. Managed services streamline maintenance and support workflows, minimize downtime, and ensure quick issue resolution. Enhanced security resilience. Proactive monitoring and maintenance reduce the likelihood of system failures and improve overall system reliability. Standardized processes for move-add-change (MAC) activities ensure that security configurations remain consistent across locations. Cost savings. Outsourced providers help organizations optimize resources, avoid errors, and benefit from economies of scale in service delivery. Strategic focus. Outsourcing also allows internal teams to shift their focus from routine operational tasks to higher-value activities, such as strategic planning, threat analysis, and incident response. Long-term value of security investments While Day 1 success is the foundation of a comprehensive program, what happens on Day 2 determines your ability to realize the long-term value of your security investments. As the complexity of security challenges grows, leaders must prioritize sustained management and professionalized oversight to protect their organizations, making the conversation around post-occupancy security more critical than ever. By adopting innovative strategies, implementing mature toolsets and processes, and leveraging specialized expertise, organizations can ensure their programs remain robust, aligned, and prepared to meet the challenges of tomorrow.

The days of being reactive are over. That’s right, we as an industry, can no longer afford to be reactive. As threats evolve, the need for proactive security is critical. While traditional methods, including physical barriers and security personnel, are still necessary, the future of our approach is built on the backs of emerging technologies. Substantial vulnerabilities As an industry, we’ve operated reactively for decades, it has been common for security teams to address threats only after they occur. The growing risk landscape proves that this approach has significant limitations. Human oversight, delayed responses, and the inability to monitor large areas have exposed substantial vulnerabilities. Emergence of AI AI enables real-time monitoring, advanced data analysis, and more accurate risk detection Times are changing though and it’s largely due to the emergence of AI. AI is revolutionizing the security landscape by making technology smarter. It enables real-time monitoring, advanced data analysis, and more accurate risk detection. This ensures a higher level of security and safety, minimizing potential incidents' impact while enhancing overall safety. Focus on strategic aspects AI's ability to process vast amounts of data quickly and accurately is, quite frankly, a game-changer. It can identify patterns and anomalies that can provide stakeholders with critical insights to respond in a more prepared manner. By automating routine tasks and highlighting potential issues, AI also allows operators to focus on more complex and strategic aspects of security management, rather than responding to false alarms. The future is AI The future of security lies in AI. The Security Industry Association (SIA) has recognized AI as one of the top security megatrends in 2024. However, the challenge is not adopting AI, it is about effectively using it to enhance security. AI can enhance video surveillance by improving object detection and enabling real-time, informed responses AI systems can easily integrate with existing infrastructures, providing a layered defense that combines traditional methods with more modern technology. For example, AI can enhance video surveillance by improving object detection, reducing false alarms, and enabling real-time, informed responses. This ensures that security measures are adaptive, scalable, and capable of addressing the evolving risk landscape. Don’t react, anticipate One of AI's most significant benefits is its ability to provide proactive insights. AI can predict potential breaches by analyzing behavior patterns and detecting anomalies allowing security pioneers to do something before an event happens. This shift, from reactive to anticipatory measures, marks a significant advancement in asset protection and risk management. AI systems can also continuously analyze data and distinguish between everyday events and real-world threats. It’s AI's continuous learning capabilities that mean the systems can adapt and improve over time to become more accurate and efficient in threat detection and response. Save money, scale on demand Contrary to common belief, adopting AI technologies will not put a security department over budget. It may be surprising, but these solutions offer cost-effective and scalable alternatives to traditional security measures. An initial investment in AI technology can result in substantial long-term savings (and ROI) by reducing the need for physical infrastructure and on-site security personnel. Customizable solutions The ability to scale and customize AI solutions makes them an efficient choice for enhancing perimeter defense AI systems are also inherently scalable and can be tailored to meet the specific needs of different environments. This ensures the system can evolve with emerging threats and technological advancements without requiring a complete system overhaul. The ability to scale and customize AI solutions makes them a practical and efficient choice for enhancing perimeter defense. How’s that for staying within budget? Embrace the possibilities Integrating AI into perimeter security is the future of proactive and intelligent security. As these technologies continue to evolve, we can expect even more refined solutions that are predictive, autonomous, and capable of directly addressing new and emerging threats. We’re experiencing an exhilarating transformation as AI becomes more trusted, precise, and advanced on multiple levels. This evolution is bigger than pilots and small, low-profile deployments. AI in perimeter security For instance, France is preparing to deploy AI-powered video surveillance as it gears up to host the 2024 Olympics, part of its efforts to detect sudden crowd movements, abandoned objects, and suspicious activities. Think about the sheer scale of that project. We’re finally moving forward, and staying one step ahead must be our priority. But this shift requires a significant change in mindset. Are you ready to make the change?
In the realm of physical security, the distinction between being perceived as a security vendor and a security partner holds great importance. While both may seem interchangeable at first glance, how an organization is viewed by its clients can have a huge impact on the success of its security programs. At the heart of this differentiation is the concept of relationships and how they shape the dynamics between providers and their clients. Time, care, and diligence For security vendors such as systems integrators, security dealers, monitored services providers or manufacturers that sell directly to the end user elevating from supplier to partner requires a greater investment of time, care, and diligence. However, the eventual payoff can be incalculably advantageous to the organization. Not only does this approach better serve the client but it also cultivates longer-term business and is more likely to generate referrals. Clients will change vendors often but stick with partners for the long haul. Simple installation and/or service Security end-users should look to their security products and service providers to partner with them Security end-users should look to their security products and service providers to partner with them, be vested in their success, and be part of the solution. They should seek out and expect more than a simple installation and/or service in the absence of any real, tangible, and value-added relationship with stakeholders. That means looking deeper than the similar cameras or equipment most vendors provide. Doing so brings benefits from the partnership in solving problems and creating strategies for mitigation. Vendors have short shelf lives A security vendor is typically seen as a transactional company that offers products or services to address specific security needs or challenges. When an organization engages with a vendor, the focus is primarily on the exchange of goods and/or services for a fee. The relationship tends to be more transactional, with limited interaction beyond the scope of the security solution being provided. Tools, technologies, or service offerings The relationship between a security vendor and a client is often short with a one-time purchase Security vendors often play a crucial role in the security industry by offering specialized tools, technologies, or services that can help organizations improve their defenses against threats. Examples would be video surveillance, access control, intrusion detection, or fire/life-safety systems, as well as the monitoring of any of them from a central monitoring station or security operations command center. The thing about it is, however, that the relationship between a security vendor and a client is often short with a one-time purchase and limited ongoing engagement or consultation. Partners prove their value On the other hand, a security partner is viewed as a member of the team that works closely with an organization to address its security challenges. Unlike a vendor, a security partner is invested in the long-term success of their clients and is committed to building a strong relationship based on expertise, trust, and transparency. Creating custom solutions Security partners go beyond offering products or services by engaging with companies and organizations Security partners go beyond offering products or services by engaging with companies and organizations to understand their unique security needs, goals, and challenges. They work concurrently with organizations to develop customized security solutions, provide support and guidance, and adapt to ever-changing threats and risks. When this kind of scenario is developed, the potentially distracting and detracting focus on monetary cost moves to the back burner because the value and return on investment (ROI) are so thoroughly compelling. Relationships bring real benefits The core of the difference between being perceived as a security vendor and a security partner hinges on the crucial role of relationships. While vendors focus on transactions and sales, partners prioritize collaboration and a sense of being in it together. Building strong relationships based on trust, communication, and shared goals is essential for forging a successful security partnership. Personalized approach Security partners navigate complex security challenges, drive innovation, and deliver incredible value over the long term Security partners are not just providers of security solutions; they are trusted advisors who are invested in the success and well-being of their clients. They can be reached easily when needed and emphasize a personalized approach with custom-tailored solutions. By building strong relationships based on respect and understanding, security partners navigate complex security challenges, drive innovation, and deliver incredible value over the long term. Operational opportunities Businesses and facilities often encounter or face very specific security needs that can only truly be solved in concert with a vendor that essentially acts like an extension of the end-user organization. Furthermore, when communicating and collaborating on that level, additional security/safety and sometimes even operational opportunities for improvement come to light. This amplifies the value for both the end customer and their security vendor. Talk about a win-win! Prosper with partner power While vendors offer products or services, partners offer teamwork, expertise, and a shared commitment At the end of the day, the difference between being a security vendor and a security partner is not merely a matter of semantics. It is about the fundamental difference in approach and mindset toward physical (electronic and networked) security. While vendors offer products or services, partners offer teamwork, expertise, and a shared commitment to reducing losses and crime. Quality of relationships Ultimately, it is the quality of relationships that separates providers in the security space and determines the success of security initiatives in the current rapidly changing security landscape. This unification of intent, practice, and purpose enables practitioners and the public alike to harness the full power of pioneering-edge technologies that support the security industry’s core mission of protecting people and property. Security partners are not just providers of security solutions; they are trusted advisors who are invested in the success and well-being of their clients.
Security beat
The shift from standalone systems to fully integrated solutions is one of the biggest shifts the security industry has experienced in recent years. There is a higher demand for integrated solutions that go beyond just security at the device and software level, and manufacturers have been continuously developing improved application programming interfaces (APIs), and hybrid and cloud-connected solutions. Artificial intelligence (AI) Also, artificial intelligence (AI) plays an important role in modern intrusion systems by helping enable automated threat detection, real-time response, and predictive analysis. AI algorithms can analyze vast amounts of data to identify patterns and anomalies that may indicate security breaches. Security solutions are being developed with a focus on AI and machine learning to provide more proactive and resilient defenses against increasingly sophisticated cyber threats. Benefits of AI AI-driven security solutions can continuously learn and adapt to new threats, providing more robust protection “The practical benefits of AI in security systems include enhanced accuracy in detecting threats, reduced response times through automation, and the capability to anticipate and prevent potential vulnerabilities before they are exploited,” says Sergio Castillejos, President, of Commercial Security at Honeywell. Additionally, AI-driven security solutions can continuously learn and adapt to new threats, providing businesses with more robust and dynamic protection. Unified Intelligent Command user interface Honeywell meets the challenge of better-integrated systems with a unified Intelligent Command user interface (UI). Castillejos says Honeywell continually innovates with the latest analytics and encryption to keep up with evolving threats. Honeywell’s products integrate with many offerings for partners to construct a robust and modern system relevant to their security needs. Advanced cloud-based security Advanced cloud-based security technologies have been developed that offer real-time monitoring, automated threat detection Advanced cloud-based security technologies have been developed that offer real-time monitoring, automated threat detection, and remote management, essential for hybrid work environments, says Castillejos. “These solutions enhance scalability, improve data analytics capabilities, and provide seamless updates reducing significant maintenance costs that help companies to respond swiftly to emerging threats and enable robust, adaptive security measures.” Physical and digital security The best security systems are a combination of physical, digital, and national security, says Castillejos. While Honeywell focuses on providing the best in physical and digital security within their solutions, protecting sensitive and/or personal information must also be within the responsibility of the organizational policy. Cybersecurity for connected devices Some of the challenges in the next five years will likely include integrating advanced technologies Security systems can safeguard this information by being highly configurable while also notifying users of unwanted activity. Sometimes, just restricting access to sensitive areas can be enough. However, in the world of data analysis and machine learning, security systems can audit and report on users who have accessed data to ensure that the protections are in place. Some of the challenges in the next five years will likely include integrating advanced technologies such as AI and the Internet of Things (IoT) while securing cybersecurity for connected devices, notes Castillejos. Balancing act “Additionally, there will be a growing need for skilled professionals to manage and maintain these complex, connected systems,” he says. “Balancing cost-effectiveness with the demand for resilient security solutions will also pose a significant challenge, especially for smaller businesses.” Legacy systems that are susceptible to vulnerabilities like cloning or unauthorized access present the largest challenge to overcome. “However, as technology evolves, it becomes more challenging for a customer to manage a unified security system rather than a collection of unique solutions that all operate independently,” says Castillejos. Disruptive technology But investing in the newest analytics, AI and IoT will not improve a company’s physical security systems if they do nothing with the data. “They are not a replacement for the devices that keep people and property safe,” says Castillejos. “They can enhance a user’s experience and speed up the time to respond when they are planned correctly.” The best security systems will look at disruptive technology as another tool in the overall system. However, the focus should remain on the user experience. If the latest technology is not properly integrated or configured, it will turn into more noise that most operators will ignore. {##Poll1720586145 - Which is the most useful benefit of artificial intelligence (AI) in security systems?##}
Fueled by mounting concerns about the cybersecurity vulnerability of U.S. ports, President Joe Biden has signed an Executive Order aimed at shoring up defenses against cyberattacks. Cybersecurity initiative The cybersecurity initiative marks a significant shift in policy, empowering key agencies and outlining concrete actions to bolster defenses. By empowering agencies, establishing clear standards, and fostering collaboration, the initiative aims to strengthen U.S. ports against the evolving threat of cyberattacks, safeguarding the nation's maritime economy and national security. Expanded authority for DHS The proactive approach aims to prevent incidents before they occur The Executive Order grants expanded authority to the Department of Homeland Security (DHS) and the Coast Guard to address maritime cyber threats. DHS gains the power to directly tackle these challenges, while the Coast Guard receives specific tools. The Coast Guard can compel vessels and waterfront facilities to address cyber vulnerabilities that endanger safety. The proactive approach aims to prevent incidents before they occur. Real-time information sharing Reporting any cyber threats or incidents targeting ports and harbors becomes mandatory. This real-time information sharing allows for swifter response and mitigation efforts. The Coast Guard also gains the authority to restrict the movement of vessels suspected of posing cyber threats. Inspections can be conducted on vessels and facilities deemed risky. Mandatory cybersecurity standards The standardization aims to eliminate weak links in the chain and prevent attackers from exploiting Beyond these broad powers, the Executive Order establishes foundational elements for improved cybersecurity. Mandatory cybersecurity standards will be implemented for U.S. ports' networks and systems, ensuring a baseline level of protection across the board. This standardization aims to eliminate weak links in the chain and prevent attackers from exploiting individual vulnerabilities. Importance of collaboration and transparency Furthermore, the initiative emphasizes the importance of collaboration and information sharing. Mandatory reporting of cyber incidents fosters transparency and allows government agencies and private sector partners to work together in mitigating threats. Additionally, the Executive Order encourages increased information sharing among all stakeholders, facilitating a unified response to potential attacks. Maritime Security Directive The Executive Order encourages investment in research and development for innovative cybersecurity solutions To address specific concerns, the Coast Guard will issue a Maritime Security Directive targeting operators of Chinese-manufactured ship-to-shore cranes. This directive outlines risk management strategies to address identified vulnerabilities in these critical pieces of port infrastructure. The long-term success of this initiative hinges on effective implementation. The Executive Order encourages investment in research and development for innovative cybersecurity solutions, recognizing the need for continuous improvement and adaptation to evolving threats. Recognizing the urgency of cyber threats The initiative has been met with widespread support from port authorities, industry stakeholders, and cybersecurity experts who recognize the urgency of addressing cyber threats. However, some concerns exist regarding the potential burden of complying with new regulations for smaller port operators. Effective communication, resource allocation, and collaboration among all stakeholders will be crucial to ensure the successful implementation of this comprehensive plan. Enhancing cybersecurity The more impactful and noteworthy piece is the associated NPRM from the U.S. Coast Guard (USCG) “This Executive Order is a positive move that will give the U.S. Coast Guard (USCG) additional authority to enhance cybersecurity within the marine transportation system and respond to cyber incidents,” comments Josh Kolleda, practice director, transport at NCC Group, a cybersecurity consulting firm. The more impactful and noteworthy piece is the associated Notice of Proposed Rulemaking (NPRM) from the U.S. Coast Guard (USCG) on “Cybersecurity in the Marine Transportation System,” adds Kolleda. Portions of the notice of proposed rulemaking (NPRM) look similar to the Transportation Security Administration (TSA) Security Directive for the rail industry and the Emergency Amendment for the aviation industry. Coordinating with TSA on lessons learned The USCG should be coordinating with TSA on lessons learned and incorporating them into additional guidance to stakeholders and processes to review plans and overall compliance, says Kolleda. “At first glance, the NPRM provides a great roadmap to increase cybersecurity posture across the various stakeholders, but it underestimates the cost to private companies in meeting the requirements, particularly in areas such as penetration testing,” says Kolleda. Cyber espionage and threats The focus is on PRC because nearly 80% of cranes operated at U.S. ports are manufactured there “It is unclear if or how the federal government will provide support for compliance efforts. As this seems to be an unfunded mandate, many private companies will opt for the bare minimum in compliance.” “Cyber espionage and threats have been reported by the Director of National Intelligence from multiple nation-states including China, Russia, and Iran,” adds Paul Kingsbury, principal security consultant & North America Maritime Lead at NCC Group. The focus here is on the People’s Republic of China (PRC) because nearly 80% of cranes operated at U.S. ports are manufactured there, he says. Destructive malware “The state-sponsored cyber actors’ goal is to disrupt critical functions by deploying destructive malware resulting in disruption to the U.S. supply chain,” says Kingsbury. “These threat actors do not only originate in China or other nation-states but also include advanced persistent threats (APTs) operated by criminal syndicates seeking financial gain from such disruptions." "The threat actors don’t care where the crane was manufactured but rather seek targets with limited protections and defenses. The minimum cyber security requirements outlined within the NPRM should be adopted by all crane operators and all cranes, regardless of where they are manufactured.” PRC-manufactured cranes Kingsbury adds, “The pioneering risk outlined in the briefing is that these cranes (PRC manufactured) are controlled, serviced, and programmed from remote locations in China." "While this is a valid concern and should be assessed, there are certainly instances where PRC-manufactured cranes do not have control systems manufactured in PRC. For example, there are situations in maritime transportation system facilities where older cranes have been retrofitted with control systems of European Union or Japanese origin.” Monitoring wireless threats “The Biden Administration’s recent Executive Order is a critical step forward in protecting U.S. ports from cyberattacks and securing America’s supply chains,” says Dr. Brett Walkenhorst, CTO at Bastille, a wireless threat intelligence technology company. “To ensure proper defense against malicious actors accessing port-side networks, attention must also be paid to common wireless vulnerabilities." "Attacks leveraging Wi-Fi, Bluetooth, and IoT protocols may be used to access authorized infrastructure including IT and OT systems. Monitoring such wireless threats is an important element in a comprehensive approach to upgrading the defenses of our nation’s critical infrastructure.”
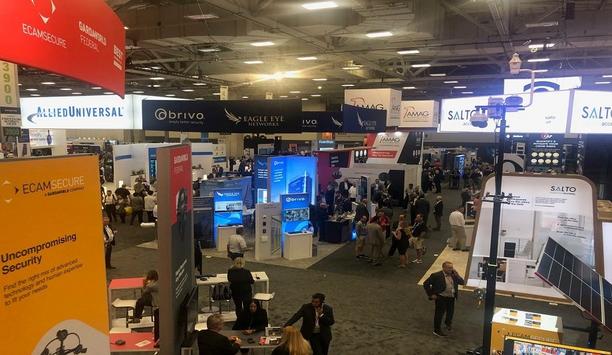
Companies at GSX 2023 emphasized new ways that technologies such as artificial intelligence (AI) and the cloud can address long-standing issues in the security market. Among the exhibitors at the event in Dallas were companies seeking creative ways to apply technology, lower costs, and make the world a safer place. Reflecting on the exhibition, here are some additional takeaways. Expanding AI at the edge i-PRO is a company reflecting the continued expansion of edge AI capability in the security market. Today, more than half of the company’s lineup supports AI at the edge so the customer has a wide choice of form factors when seeking to leverage the feature set. AI processing relay, extended warranty i-PRO is increasing their warranty period from 5 to 7 years, which could be a lifetime warranty in some cases I-PRO also has an “AI processing relay” device that accepts non-AI video streams and applies edge analytics. AI has progressed from a high-end technology to a feature available in a variety of cameras at different price points. i-PRO is also increasing its warranty period from 5 to 7 years, which could be a lifetime warranty in some cases depending on a customer’s refresh schedule and lifecycle management. Active Guard, MonitorCast The company’s video management system (Video Insight) is continuing to build new features including “Active Guard,” an integrated metadata sorter. Their access control platform, MonitorCast, is a Mercury-based solution that is tightly integrated with Video Insight. Their embedded recorders now have PoE built in. “We can move at a faster pace to fill out our product line since leaving Panasonic,” says Adam Lowenstein, Director of Product Management. “We can focus our business on adapting to the market.” Emphasis on retail and other verticals Shoplifting is a timely issue, and retail is a vertical market that got a lot of attention at GSX 2023. “We see a lot of retailers who are primarily interested in protecting employee safety, but also assets,” says Brandon Davito, Verkada’s SVP of Product and Operations. “Shrinkage is a CEO-level priority.” “Retailers are getting more engaged with security posture, instead of letting perpetrators walk,” Davito adds. Intrusion detection Verkada has an intrusion product that will notify a central station if there is an alarm On the alarm side, Verkada has an intrusion product that will notify a central station if there is an alarm, and operators can review videos to confirm the alarm. Other capabilities seeking to discourage trespassers include sirens, strobes, and “talkdown” capabilities. International expansion Verkada continues to expand internationally with 16 offices in all, including Sydney, Tokyo, and London. The core value proposition is to enable customers to manage their onsite infrastructure more simply, including new elements such as PTZ cameras, intercoms, and visitor management. Verkada emphasizes ease of use, including a mobile application to allow access to be managed across the user base. Forging partnerships “We are committed to the channel and industry, and we continue to build relationships and expand our reach,” says Davito. Among the industry relationships is a new partnership with Convergint, which was hinted at during the show and announced later the same day. They are also expanding their partnerships with Schlage, Allegion, and ASSA ABLOY. Working with other verticals They offer new features for K -12 schools, and a new alarm platform is easier to deploy and manage Verkada has also found success across multiple other verticals, notably healthcare, where they integrate with an electronic medical records system. They offer new features for K-12 schools, and a new alarm platform is easier to deploy and manage. They are integrating wireless locks to secure interior doors in schools, looking to secure the perimeter, and installing guest management systems. Transitioning the Mid-Market to the Cloud Salient is squarely focused on the “mid-market,” a large swath of systems somewhere between small businesses and enterprise-level systems. Pure cloud systems are not as attractive to this market, which has a built-out infrastructure of on-premise systems. Adding a camera to an existing system is easier and less expensive than tying it to the cloud. Benefits of cloud It’s a market that may not be ready for pure cloud, but there are benefits to be realized from adding a cloud element to existing systems. “We are continuing to augment our premise-based solutions with added cloud capabilities and flexibility,” says Sanjay Challa, Salient’s Chief Product Officer. The feedback Salient hears from their customers is “I want to own my data.” The hybrid cloud approach offers the right mix of control, flexibility, and unit economics. Cloud add-on capabilities We want to provide the flexibility for customers to go full-cloud as it becomes more economically attractive" Cloud add-on capabilities include bringing more intelligence about system operation to the user via the cloud. Over time, Salient expects to sell more cloud-centric offerings based on feedback from integrators and customers. “We want to provide the flexibility for customers to go full-cloud as it becomes more economically attractive over time,” says Challa. Vaidio AI technology Salient seeks to be a transition pioneer to help customers realize the path to the cloud. Their approach is “crawl, walk, run,” and helping customers make the transition at each stage. Salient has added AI to its product offering, incorporating Vaidio AI technology from IronYun into a powerful suite and broad array of on-premise analytics, which are gaining traction. The seamless approach makes it easy for customers to embrace AI analytics, although Salient remains broadly committed to open systems. Addressing ‘Soft’ Features for Integrators AMAG is in the process of enhancing its product line with the next generation of access control panels. However, “product” is just part of the new developments at AMAG. In addition to “hard” features (such as products), the company is looking to improve its “soft” features, too; that is, how they work with the integrator channel. Integrator channel Rebuilding a process to make your organization more efficient, is relatively easy; it just takes a lot of persistence" “We have the depth of our legacy customer base we can learn from, we just need to close the feedback loop quicker,” says Kyle Gordon, AMAG’s Executive Vice President of Global Sales, Marketing, and commercial Excellence, who acknowledges the value of reinstating face-to-face meetings after COVID. “We are laser-focused on nurturing our integrator channel,” he says. “Developing new features takes time, but rebuilding a process to make your organization more efficient, that’s relatively easy; it just takes a lot of persistence,” says Gordon. More cohesive internal communication is another useful tool, he says. Disrupting the cloud based on price Wasabi is working to make cloud applications less expensive by offering a “disruptive” price on cloud storage, $6.99 per terabyte per month (80% less than hyperscalers). Contending “hyperscalers” like AWS are charging too much for cloud storage, Wasabi is using its own intellectual property and server equipment co-located in data centers around the world. Wasabi sells “hot cloud storage,” which refers to the fact that they only have one tier of storage and data is always accessible. In contrast, a company such as AWS might charge an “egress fee” for access to data stored in a “colder” tier. Cloud storage “We saw that several video surveillance companies had not yet adopted cloud storage, and we saw an opportunity to make it easy to use,” said Drew Schlussel, Wasabi’s Senior Director of Product Marketing. “We just install a little bit of software that allows them to store data in the cloud and bring it back from the cloud.” Performance, protection (cybersecurity), and price Wasabi works with integrators, resellers, and distributors and also integrates with VMS companies Wasabi works with integrators, resellers, and distributors and also integrates with VMS companies such as Genetec and Milestone. Emphasizing performance, protection (cybersecurity), and price, their data centers are certified to SOC 2 and ISO 27001 standards. Faster throughput for weapons detection Xtract One is a young company focusing on weapons detection in a time of accelerated concern about gun issues post-COVID. Founded in Canada and based on technology developed at McMaster University, Xtract One has found a niche in providing weapons detection at stadiums and arenas. These customers already have budgets, and it is easy to shift the money to a newer, faster technology. Madison Square Garden in New York City is among its customers. Cost savings solution Xtract One can increase throughput to 30 to 50 people per entrance per minute (compared to 5 to 6 people per minute when using metal detectors). The solution doesn’t require anyone to empty their pockets and the system alarms on items beyond guns and knives. Using Xtract One allows customers to reduce the number of screening lanes and security staff, providing additional cost savings, all while getting fans through the screening process in half the time. Purpose-built sensors The system uses purpose-built sensors looking for specific characteristics, such as reflective and density properties In addition to stadiums and arenas, Xtract One, formerly Patriot One, is also getting “inbound” interest from schools, hospitals, manufacturers, and other verticals that makeup 50% of their business. “We’re on a rocket ride, mainly because the weapons issues are not going away,” says Peter Evans, CEO and Director at Xtract One. The system uses purpose-built sensors looking for specific characteristics, such as reflective and density properties, all correlated by an AI engine. Providing early warning of violence ZeroEyes is another company focused on weapons detection. Their AI gun detection system works with video images to identify if someone is “brandishing” (carrying) a weapon. In other words, the system does not detect concealed weapons. Identifying someone carrying a weapon provides early warning of a possible violent act. Increased response with AI-enables images Images are identified by AI and sent to a monitoring center where a human confirms the image before contacting first responders. Knowing the location of a shooter enables staff to lock entry points, move people to safety, and direct first responders. The company was founded to leverage existing camera views to stop mass shootings and gun violence by reducing response times.
Case studies

Security requirements for critical infrastructure are changing rapidly. Recent events, such as the discovery of a drone at Leipzig Airport, have once again demonstrated how quickly modern technologies can become a security challenge. This makes dialog between industry, authorities and emergency services all the more important. Security Essen, which will take place at Messe Essen from 22 to 25 September 2026, is placing precisely this exchange at the heart of two key program highlights: the European Drone Conference and the Emergency Services Forum. Unmanned aerial systems open up a wide range of potential applications – from inspecting critical infrastructure to supporting security and emergency services. Protection of critical infrastructure At the same time, they present new challenges for operators of sensitive facilities. The European Drone Conference on 23 and 24 September will therefore bring together experts from the security industry, public authorities, academia and politics to discuss current developments, the regulatory framework and effective protection strategies. The conference is organized by the Drone Expert Committee of the German Security Industry Association (BDSW), together with Security Essen and the Confederation of European Security Services (CoESS). Experts discuss drone deployment, detection and countermeasures Around 20 specialist presentations will examine drone technology from various perspectives – ranging from regulatory issues and the protection of critical infrastructure to detection and counter-drone systems. Managing new risks In his statement, Cornelius Toussaint, Vice-President of the BDSW and Chair of the Drone Expert Committee, will focus on security and drone technology in Germany. Marcus Schermann (DB Sicherheit GmbH) will discuss the protection of critical infrastructure, using multicopter operations as an example. Drone management, with a particular focus on detection and countermeasures, is the main theme addressed by the two speakers, Ralf Holstein and André Danner (German Business Protection GmbH). The program is complemented by presentations on research and development, as well as international keynote speeches from the worlds of politics and the security industry. The central question is how to capitalize on the opportunities offered by the technology whilst effectively managing new risks. Public safety authorities Emergency Services Forum (Blaulichtforum) takes place for the first time In collaboration with Feuerwehr-Magazin (Fire & Rescue Magazine) and Rettungs-Magazin (Emergency Medical Services Magazine), the Emergency Services Forum 2026 will make its debut at Security Essen. On 22 September, the new forum will bring together public safety authorities and organizations (BOS), the security industry and public authorities, focusing on a key question: How are new threat scenarios and technologies changing security and emergency response? On stage, experts from the fire service, police, civil protection, the security industry and defense will discuss current challenges: What role will drones and autonomous systems play in future operations? Shared situational picture How well is Germany prepared for CBRNE incidents and hybrid threats? And how do control centres, communication technologies and networked systems ensure that a shared situational picture emerges in an emergency? The focus will also be on cooperation between civilian and military actors. Specialist conferences included in the trade fair admission ticket Both the European Drone Conference and the Emergency Services Forum will take place directly in Hall 5. Admission is already included in the Security Essen trade fair ticket. Tickets for Security Essen 2026 are available online. A day ticket costs €49. The trade fair is open from 9 am to 6 pm from Tuesday to Thursday and from 9 am to 4 pm on Friday.
iDenfy, the global RegTech solution provider that delivers identity verification and fraud prevention tools, has implemented Czech Bank iD into its electronic identity verification software. The addition of the new digital ID or non-document verification method for the Czech market gives businesses a native alternative for verifying Czech citizens through their existing bank login credentials, without asking for a physical document during the onboarding process. Czech Bank iD is a nationwide, bank-issued digital identification system introduced in the Czech Republic in 2021. It allows citizens to use their internet banking credentials to authenticate themselves for both e-government and private sector services. Separate identity document The system is currently used by over 5,000,000 internet banking users, which corresponds to an adoption rate of 57% across the Czech Republic with 9 million people. Czech Bank iD runs on the OIDC protocol and operates through a bank delegation model, meaning the verification is confirmed directly by the user’s bank rather than through a separate identity document. iDenfy’s non-document verification platform was built to operate alongside the platform’s standard document-based KYC flow. Businesses can configure the platform to automatically route users to the Czech Bank iD path when traditional document capture is unavailable or produces insufficient image quality, a scenario that iDenfy’s internal data consistently shows as a recurring source of session drop-off. The combined flow is available to all iDenfy clients at no additional cost and can be activated in the dashboard settings without any additional integration work. Additional integration work To perform a successful verification, Czech Bank iD checks the person’s given name, family name, middle name, full name, date of birth, nationality, sex, phone number, and full address details. Where available, it can also return document data, such as document type, number, issue date, expiration date, issuing country and authority. This gives businesses a verification result that is both broad in scope and consistent in structure, since the data is returned directly by the bank network rather than extracted from a scanned image. As defined by Regulation (EU) 2024/1183, each of the EU 27 will have to implement the EU Digital Identity Wallet for citizens and residents by the end of 2026. Every bank, payment, and electronic money institution will have to support wallet-based credentials as Strong Customer Authentication measures. Bypassing security controls The Czech Republic has the third-highest risk of cyber fraud globally, according to security firm Gen Digital, which conducted research from Avast, AVG, and Norton companies. Social engineering attacks, a form of psychological manipulation in which criminals trick people into giving up private data, downloading malware, or bypassing security controls, made up 86% of the threats that happened in the country. iDenfy states that for businesses that serve Czech market users, the ability to verify identity through a credential that more than five million adults already use for banking and government access can remove a document capture step that often contributes to onboarding drop-off. It still maintains a secure enough compliance procedure to keep the process trustworthy for both the user and the business so it can validate a real person behind it. Digital identity networks “Czech Bank iD has become one of the most widely trusted digital identity credentials in the Czech Republic. Our clients that serve that market can now meet Czech users on those terms and present a verification path that feels familiar and requires no additional physical document capture at the point of onboarding,” said Domantas Ciulde, the CEO of iDenfy. It is worth mentioning that iDenfy’s KYC software currently covers over 16,000+ government-issued documents across over 200+ countries and territories. If a case is not resolved automatically, it is reported to iDenfy’s internal compliance review team, which works 24/7 to review identities and fix any onboarding issues. “Czech Bank iD is deeply embedded in how Czech citizens already access banking, government, and private sector services. For our clients, adding Czech Bank iD is not just an onboarding improvement. It is a direct connection to one of Central Europe’s most established digital identity networks,” added Domantas Ciulde. Czech Bank iD support is available now across iDenfy’s identity verification platform.
Willis Tower, an iconic symbol in Chicago for over 50 years, has undergone significant transformations to become a modern workplace and community hub that delivers the best experiences for its tenants, area residents and visitors. Originally known as Sears Tower, it was renamed Willis Tower after a change in ownership in 2009. Major renovations took place in 2017, culminating in a complete transformation in 2022. Currnetly, Willis Tower offers a range of amenities from short-term workstations to traditional leases, as well as dining, retail, and entertainment spaces. The Skydeck on the 103rd floor, 1,353 feet above street level, provides breathtaking views of up to 50 miles across four states, attracting millions of visitors annually. Challenge As part of Willis Tower’s transformation, the structural separations between the office and Skydeck areas were eliminated, creating a more open and accessible space for visitors and tenants. Recognizing the need for a customized strategic security plan, Director of Security Keith Kambic, CPP, spearheaded efforts to find the right partners to ensure the safety and security of tenants, visitors, and employees. Kambic’s first step was to engage with the national security and technology consulting firm Guidepost Solutions. The next priority was to establish a strong partnership with a Chicago-based integration partner and to identify the best security solutions in the market. Kambic chose 4S Security as the integration partner because of their holistic approach to achieving optimal results. The partnership with 4S Security elevated the security measures at Willis Tower to new heights. “We are different than the average integrator,” said Leor Elfassy, Director of Business Development at 4S. “We have software developers on staff who write integrations, and as a matter of business principle for the last 30 years, we only work with software manufacturers that allow us to do so.” Solution The upgrade to Willis Tower involved retrofitting the access control system to a cloud-based solution and the new Video Management System (VMS), Salient CompleteView, was selected based on its ability to integrate seamlessly with the access control platform. “In the end the client wants a single pane of glass that they can work from and Salient’s CompleteView is well-designed to let integrators bring their vision to life,” continued Elfassy. Salient’s open architecture was an essential factor in the decision, along with product features like Dynamic Resolution Scaling (DRS), a powerful bandwidth management tool, and agnostic integration to analytic platforms for future system enhancements. Specific features like snapshot and CompleteView’s interactive mapping feature were also important selection factors. While all of these product capabilities are important, in the end it came down to the personal attention of Salient team members – from the President to the system engineer – and their efforts to go above and beyond in every way. Salient’s dedication to working cohesively with the Willis Tower and 4S teams created an effective partnership that propelled the project forward. Kambic said, “when we selected Salient, we did so not only for their product, but because we could tell that both of our companies were cut from the same cloth – great service, and great people.” Both Salient and 4S provided learning tools prior to implementation to ensure a seamless transition to the new VMS for the Willis Tower security team. 4S created customized training videos and pamphlets and held onsite training sessions, while Salient educated the security team through its YouTube training videos. Results The result of the partnership between 4S and Salient was a 40% reduction in bandwidth usage across the Willis Tower network. In addition, the integrated system provided immediate awareness of events such as forced-open doors, tailgating, and panic alarms. Ongoing top-notch local support from both Salient and 4S ensures smooth and timely software release updates and exploration of new technological capabilities, advancing video surveillance through CompleteView. Pleased with the results, the Willis Tower team attests to the success of the partnership, efficacy of Salient’s product, andoutstanding level of service from Salient both before and after the sale.
In alignment with the State of Mississippi’s mission of “Empowering Mississippi citizens to stay connected andengaged with their government,” Salient's CompleteView Video Management System (VMS) is being installedthroughout more than 150 state boards, commissions, and agencies in order to ensure safety for thousands ofconstituents who access state services daily. Challenge Determining the right path to success wasn’t a quick process. The elaborate undertaking of converting all State of Mississippi buildings from its legacy video system, which included analog cameras across a disparate video platform, to match their standard of excellence took a lot of planning. This involved researching and interviewing multiple manufacturers of IP cameras and video management systems. The plan was strategic, as it was important to State officials to find an open architecture solution that could utilize as much existing technology as possible, thereby preserving current taxpayer investment. Solution After a thorough evaluation, the decision came down to three competitive VMSs, all based on total cost-of ownership, scalability requirements, software performance capabilities, along with support assessments. Salient’s CompleteView was ultimately determined the top choice. “In the selection process, three VMS manufacturers were deemed a reasonable fit. The choice of CompleteView over these competitors came down to one critical component, partnership. The culture at Salient embodies an unmatched support you don’t typically see in an industry leader. Their greatest value-add is that open line of communication between the RSM, technical support, and engineering. If I need something, I know I can pick up the phone and get immediate assistance” said Mike Cooper with MS Department of Public Safety. Once CompleteView was selected, another strategic decision was made to have personnel from The Statehandle the design and installation of CompleteView internally rather than engage outside consulting. This hasproved to be an effective option, allowing them to tailor each installation to suit individual property needs. The State works through the channel for procurement, then handles all programming and administration internally. This offers them the most flexibility while still achieving uniformity across each deployment as well as complete control of the process. Result The conversion to CompleteView is underway and will take approximately 3-5 years to complete. The State now benefits from a centralized platform that allows for greater administrative control, as well as a product that meets the State of Mississippi standard for NDAA compliance. According to Cooper, “we now have a platform that is easily managed and visibly organized in an efficient manner. We also appreciate having a system that’s permission based with tighter controls.” Finally, The State’s technical team is committed to keeping the system updated as Salient releases newer versions of its software each quarter. These upgrades ensure they are taking advantage of all security enhancements and feature improvements that CompleteView has to offer. The State has also planned integration of its access control system, Open Options, with CompleteView, tying video directly to specific door openings. This gives State personnel an enhanced view into their security operations, with quick and easy auditing of badge events through a single interface. Further initiatives will explore the addition of AI video analytics to add weapons detection, appearance search, and cross-camera tracking — all to help speed up investigations. Salient’s open platform makes these integrations possible. Staying present on these new releases and innovative integrations ensures an advanced level of protection from potential threats and works to achieve the ultimate end game – keeping community members safe.
The Community Builders (TCB) is a nonprofit organization whose mission is to build and sustain strong communities where all people can thrive. They work with businesses, institutions, and public officials to revitalize neighborhoods in ways where all people can live in healthy homes with equitable access to resources and opportunities to pursue their dreams. Their partnership with Salient Systems exemplifies the use of video technology in vulnerable neighborhoods to help achieve these goals. Challenge TCB operates and manages 150 sites and properties across the country, employing over 600 staff members. These locations range from campus environments to individual buildings, each presenting unique security challenges to ensure overall resident safety. The primary focus for implementing a video management system is not only to ensure safety and security but also prevent property maintenance issues. Under Joe Giggey’s leadership as senior director of Information Technology, TCB established enterprise- level security standards. These standards enabled access to video remotely through smartphones, iPads, and laptops for a central team of sites in 30 cities. Additionally, seamless integration with existing cameras and access control systems was required, considering TCB’s extensive network of 30+ access control systems and about 6,800 different camera models. Affordability was another crucial factor, as is often the case for nonprofit organizations. Having an easy-to-administer VMS, reliable search and video export functionalities, scalability for future property acquisitions, and centralized management in a distributed environment were also significant requirements. Solution Salient’s CompleteView VMS met all the specified criteria, marking the beginning of the partnership between TCB and Salient in 2016. The deployment of CompleteView has grown to 85 site recording servers and over 2,300 camera licenses. Given the widespread nature of TCB’s properties, certified regionalized integrators have been selected to install CompleteView across TCB locations. These integrators have been trained and received certification from Salient Systems professional trainers on installation, executing upgrades, expanding systems, and customizing the deployment ensuring effective implementation and ongoing support. In addition, manufacturer support by Salient’s own System Engineering team has been utilized and according to TCB personnel, “has been phenomenal.” Results TCB staff help address complaints, educate residents on lease rules, and avoid evictions. Salient’s CompleteView has assisted in resolving disputes, and investigating incidents. In addition, the ability to verify details of incidents in progress helps pinpoint the location and gives first responders details about the situation they may face on arrival. Video footage provided by Salient’s VMS, CompleteView has proven invaluable in multiple instances and according to Giggey “The VMS paid for itself immediately, highlighting the effectiveness and value of this partnership.” The collaboration between TCB and Salient Systems has become an exemplar of how technology can be harnessed for the greater good, building trust and effecting positive changes in vulnerable neighborhoods. With ongoing support from Salient Systems, TCB is committed to making a lasting impact and ensuring strong communities where all people can thrive.
The HilverZorg Foundation in the Netherlands is a large organization that provides residential nursing care at seven locations as well as home nursing care for all phases of aging. One of the facilities, Zonnehoeve, is HilverZorg’s expertise center for people with dementia. Located on the Zonnestraal estate, in the middle of the beautiful Loosdrechtse forest, residents can enjoy peace and the outdoors. Zonnehoeve is comprised of multiple departments and a ward with single rooms and apartments. Computerised key management The Challenge - Keeping the residents safe at Zonnehoeve necessitates that the provision of keys is done in a good, reliable, and safe way. At one point, over 500 issued keys were distributed, and challenges occurred when many would take keys home. For security reasons this proved to be inconvenient and unsafe. The Solution - It was soon determined that procedures to access keys between residents and nursing staff, was vitally important to be supplied by computerised key management. The organization then started looking for an alternative for the distribution of keys with registration which could serve as a basis for tightening the procedures. The key management system KeyWatcher® met the set criteria and wishes. In addition, the KeyWatcher® had already proven its functionality and reliability with its use in other departments of the organization. Old-fashioned key cabinets Morse Watchmans Solution – Because allocated keys are only released to users with the appropriate authorization, the KeyWatcher® helps to pursue a certain policy and to ensure that procedures are followed. On a minimum-sized wall surface the ergonomically executed system eliminates old-fashioned key cabinets, unreliable handmade journals and sloppy ID tags. It files the history of each key including the user, date and time of distribution and return of the key. The solidly executed stainless steel cabinet has been designed to prevent abuse and it is manipulation-proof. By using the KeyPro™ Performance Software users can manage, if they are authorized, one or more KeyWatcher® systems through the network of any work station within the organization. They are able to change the data in the database, retrieve reports, release keys, cancel alarms etc. This way, the opportunity is created to manage and check the access to buildings and rooms, subject to time and place, 24/7. Key management system Implementation - After opting for the KeyWatcher® key management system, Zonnehoeve decided to install the system at a central point which is only accessible by staff. The Key Watcher manages the access to the keys and the keys can be tracked when they are in use, including the times and user names. The personnel are authorized different levels of access to the smart keys with keys. This way, efficient control is managed and carelessness or inadvertences will be prevented. By means of the KeyPro™ Performance Software the KeyWatcher® systems are managed at a distance both centrally and locally through a modem connection and the transactions and reports are filed. The Result - Thanks to the use of the KeyWatcher® key management system of Morse Watchmans and the KeyPro™ Performance Software, Zonnehoeve has been able to create a stricter key policy and to tighten the procedures concerning management and reporting. The possibility of time-saving and single use for example by temporary workers, have also been of importance in successfully deploying the system.
Round table discussion

Artificial intelligence (AI) transforms physical security from a passive, reactive function into an autonomous, proactive one. Rather than just alerting human guards after an event, new systems driven by intelligent agents analyze, decide, and act in real time—handling routine deterrence, investigating anomalies, and reducing alarm fatigue. We asked our Expert Panel Roundtable: What is agentive (or agentic) AI and how is it changing physical security?

When working in the technology marketplace, it’s always good to expect the unexpected. Increasingly, readiness to anticipate and embrace uncertainty is the baseline for survival in the world of technology. If we in the physical security industry know anything, it is that technology is in a state of perpetual disruption. Therefore, looking ahead to the next 12 months, surprises are inevitable. We turn to our Expert Panel Roundtable for guidance, asking our panelists: What will be the biggest surprise for security in the year ahead?
In many cases, architectural design and layout dictate optimal placement of security devices like cameras, access control readers, and sensors. Poor design can lead to blind spots, reduced coverage, and ineffective surveillance. However, planning that involves all the various stakeholders can maximize both security and design elements. We asked this week’s Expert Panel Roundtable: When are building design and physical security systems complementary? When are they at odds?
Products

Videos


Security service: Manufacturers & Suppliers
- Bolide Security service
- Dedicated Micros Security service
- Dahua Technology Security service
- VIVOTEK Security service
- Seagate Security service
- Hanwha Vision Security service
- ITI Security service
- Vigilant Vision Security service
- Vanderbilt Security service
- OT Systems Security service
- Messoa Security service
- HID Security service
- Tamron Security service
- Nedap AEOS Security service
- LILIN Security service
- AMAG Security service
- Parabit Security service
- Pelco Security service
- Panasonic Security service
- Videotec Security service