Physical security

Suprema, a pioneer in intelligent access control and physical security solutions, is hosting its global partner conference, ‘Suprema Global Partner Program (SGPP) 2026,’ at Lahan Select Gyeongju in Gyeongbuk, South Korea, on November 11–12. SGPP 2026 brings together more than 300 participants, including key global partners as well as executives and employees from Suprema’s headquarters and eight overseas subsidiaries across North America, Latin America, the UK, Europe, t...

Security services provider The Keyholding Company has today announced it is rebranding as Forcefield. The change of name reflects how the business has evolved over recent years, from a provider of keyholding and mobile security services into a technology-led security company built around a single security management platform. The rebrand signals the arrival of a new type of security, one that gives clients a clearer and more cohesive view of their physical security. Forcefield’s approach...

Managing access control for a single facility is very different from overseeing dozens of locations across multiple regions. At large, complex organizations, security teams must manage more access requests, frequent role changes, and compliance requirements across multiple sites. Access control systems are also often connected to identity management platforms, business applications, and corporate networks. This growing complexity is changing how organizations view access control. Older access c...

ASSA ABLOY invites attendees to visit booth #407 at ISC East 2026, November 3 - 5, at the Javits Center in New York City, to explore the latest innovations in its growing digital access portfolio. Attendees can connect with ASSA ABLOY experts and see solutions designed to address evolving security needs across a wide range of applications. “The strength of our partnerships with security professionals is essential to meeting the changing needs of the industry,” says Angelo Faenza, He...

Most organizations operating at enterprise scale have more or less solved digital identity, consolidating directories, adopting single sign-on, and automating the workflows that govern application access, so that provisioning follows role changes and access revokes when employment ends. It is, by any measure, one of the more quietly impressive feats of enterprise IT over the past decade. Physical access has generally not followed, which creates exposure that rarely surfaces until an audit or an...

Advancis is pleased to announce a new global partnership with Convergint, expanding the collaboration between two organizations focused on helping enterprise and multinational customers manage increasingly complex security, identity and operational environments. Through this partnership, Convergint will be able to offer Advancis software solutions across its international organization, combining Convergint's extensive integration expertise, global reach and customer relationships with Advancis'...
News

The digital transformation of buildings is accelerating – and so are the expectations placed on security and facilities managers. In a landscape where cost pressures, compliance demands, and user convenience collide, the ability to extend digital control and automation is a major advantage. However large or small the premises, connecting digital access with complementary systems helps achieve this. “We can work with our customers to implement a new integration-ready digital access solution from scratch. Here we encourage them to adopt platforms which are ‘open’ to some degree: this simplifies ongoing scalability and ensures they are future-proofing this investment,” says David Moser, SVP & Head of Digital Access Solutions at ASSA ABLOY Opening Solutions EMEIA. “Alternatively, we can extend the reach, functionality, and connectivity of an existing security or access system with compatible technologies which administrators continue to control from their existing, familiar interface. This way we create more joined-up knowledge and information for the business.” Extending digital control Connecting digital devices such as battery-powered locks, mobile-operated padlocks, electromechanical door devices, biometric readers, or electronic escape route technology can become a first step to transforming a fragmented building system into a cohesive, responsive network. It is straightforward, for example, to replace access points’ mechanical locking with wireless locks and then integrate these seamlessly with existing access management software. One interface still controls everything. This ensures the legacy system adapts to evolving needs and reduces the overhead of multiple standalone solutions being managed in parallel. “Integration can also break down operational siloes, fostering collaboration between security, facilities, and IT teams as well as day-to-day efficiencies that business leaders will notice on the balance sheet,” adds Moser. “Integrating visitor management with an access system, for example, helps create a convenient contactless check-in experience. Integrating company digital ID with room booking software, and room access, removes unnecessary manual admin. And so on.” The overall result of increased connectivity is not only a more secure environment, but also an efficient and future-proof one. What follows are just 5 among the many practical, actionable benefits. Toggling between platforms Besides added security, the most obvious benefit of extending an existing access system is the simplification of daily operations. Instead of toggling between platforms, security managers have one unified interface for configuring, monitoring, and auditing building performance across every connected device and site. Such consolidation within a familiar environment reduces staff training needs and minimizes human error. This quickly translates to lower admin costs which are sustainable over the long term. Making visible real-time audit trails and status updates for more openings ensures greater transparency and accountability. This additional functionality – and much more – is available by extending an access solution with proven, trusted devices. Data-driven efficiency and risk reduction The additional data generated by an extended digital access system is not merely informative. Improved space utilization analytics, for example, provide insights into how and when areas of a building are used. This real-time intelligence allows organizations to adjust their physical footprint and energy consumption, trimming the costs of under-utilised spaces. For facilities managers who face budget constraints, this alone may quickly generate a measurable ROI. Predictive risk management can bring another operational boost. By analyzing patterns in access events – such as repeated failed attempts or unusual entry times – security teams can anticipate and prevent incidents before they occur. This shift from reactive to proactive security not only enhances safety but also reduces the likelihood of breaches or regulation violations. Compliance and the threat landscape Extending the capacity and connectivity of a system can enable organizations to meet compliance demands while adapting to their specific security challenges, including the growth in hybrid cyber-physical security threats. ENISA’s 2025 Threat Landscape report highlights the increasing sophistication and convergence of cyber-physical threats, noting that attackers are now exploiting vulnerabilities across both digital and physical systems to maximize their chance of success. Digitalising access at more openings is one way to close security gaps. Here, of course, compliance with standards such as ONVIF and OSDP ensures customers choose a future of effective interoperability. Smarter credential management Key and digital credential handling are streamlined when businesses do not deploy multiple access systems or workflows at the same premises. Users no longer need to juggle multiple fobs, cards, or keys. Instead, they rely on one programmable credential for access across all their authorized openings. This simplification not only improves user experience; it also cuts overhead by reducing the time spent issuing, tracking, and deactivating credentials. Savings are especially significant when equipping and connecting doors which are currently secured with mechanical locks. Fewer lost or duplicated keys helps to reduce emergency rekeying costs and the need for unplanned service visits. Fitting wireless locks to these openings brings an easy cost-management win. Scalability with future-proof systems For organizations of every size and type, scalability is critical. No one can perfectly anticipate what is ahead. A trusted integration partner provides ongoing, region-specific support and certified solutions tailored to local standards – ensuring seamless deployment and compliance. Where appropriate, extending control can future-proof an existing system without requiring businesses to start again from scratch. As new devices and technologies emerge, a flexible, connection-ready platform can continue to evolve, without costly overhauls, by the incremental addition of connected devices. This adaptability ensures that security managers are not locked into outdated systems, but instead have a scalable, forward-looking solution that grows with them. ASSA ABLOY’s connected digital access solutions “Security managers may not know what comes next. But with a connected system, built on architecture which enables even greater connectivity in the future, they do not need to,” says Moser. “ASSA ABLOY offers a vast and growing range of connectable solutions designed to plug directly into any new or existing access system. Extending the reach of control, with this suite of devices and solutions, helps them prepare their premises for what’s ahead.” ASSA ABLOY’s suite of connectable digital access solutions includes the following: Aperio® Wireless Locks: Seamlessly integrated with over 130 access control systems, enabling centralized management of previously mechanical access points, with support for online and offline operation, RFID cards, mobile credentials, and a wide range of lock types. ABLOY® CUMULUS: A cloud-based, mobile-first platform providing easy integration of digital access devices and mobile access through open APIs and SDKs, with full audit trails and real-time status monitoring. CLIQ® Programmable Keys & Cylinders: Combining mechanical security with electronic access management, offering more than 60 cylinder and padlock variants plus intuitive, connectable management software and integration capabilities. ABLOY® Electric Locks: Meeting compliance standards for high-security, high-traffic doors and integrating seamlessly with access control, alarm, and building management systems for real-time security and safety monitoring. effeff Electric Strikes: The gold standard in door strike technology, enabling convenient remote unlocking at the push of a button and seamless integration with access control, intercom, and building management systems. effeff ePED® Electronic Escape Route Technology: Electrically controlled panic exit devices that combine certified safety, compliance, and integration with access control and security systems for safe emergency egress. Control iD Biometric Readers: Featuring advanced facial and fingerprint recognition, operating as standalone solutions or integrated with access control systems for scalable, secure access management.

Mappedin, the indoor operating platform transforming the way venues are experienced and managed, announces a technology integration with Brivo, the global pioneer in cloud-native AI-driven physical security. The integration brings Brivo's access control and video management capabilities directly into Mappedin Security Center, delivering a unified, map-based security operations experience for enterprise and campus environments. Disconnected security systems Ideal for enhancing modern facilities that already rely on multiple, disconnected security systems for access control, video surveillance, and incident management, the integration capabilities include: Seeing all access events in real time on an interactive map Viewing live video from Brivo-connected cameras based on camera locations displayed on a map Correlating access and video events based on locations Configuring alert rules to highlight specific events with visual indicators on a map Managing lockdowns and emergency responses from the map Monitoring building-wide security status on unified dashboards These combined capabilities give security teams and building operators a foundational layer of indoor building intelligence to keep physical assets, tenants, and visitors safe. Multi-floor venues “Security teams need to know what is happening, and more importantly, specifically where it is happening and what resources are nearby,” said Brian McIlravey, Director of Enterprise Security and Public Safety. “Our partnership with Brivo provides a layer of intelligence for security operators and responders so that they can make faster, more informed decisions. Together we’re delivering better safety outcomes for our customers.” Brivo's open API platform and Mappedin's SDK connect Brivo-managed access points and cameras to their corresponding locations on Mappedin's interactive 3D indoor maps. The combined integration creates a solution that supports multi-building, multi-floor venues, and scales from single buildings to large campuses. “Security events don’t happen in dashboards; they happen in physical spaces,” said Tijmen Vos, Brivo VP Product. “By combining Brivo’s unified access control and video platform with MappedIn’s indoor mapping technology, we’re giving security teams the spatial context they need to act faster and smarter. It’s another step toward making physical security more connected, intelligent, and actionable.”

Brivo, the AI innovator and global pioneer in cloud-native physical security, launches Brivo Reseller MCP, the first Model Context Protocol server for security systems integrators. By connecting AI assistants and partner portal tools through the MCP, resellers can create dashboards, identify customers up for renewal, review service tickets, understand growth patterns, and do analysis in minutes that would normally take days or weeks—all from inside the LLM they normally use. Brivo also introduced a private beta for Brivo MCP for end users. “Brivo meets our customers and partners wherever they do their work. Today many people spend a lot of time working in tools like Claude, ChatGPT and Gemini—because these tools are so powerful,” said Steve Van Till, Brivo Founder and President. “You can now use whatever AI tool you like to help manage your Brivo system using natural language prompts. We meet you where you need us to meet you.” Comprehensive sales analysis Using Brivo in conjunction with an AI assistant gives security resellers powerful new ways to grow their business. For example, a reseller can now get a comprehensive sales analysis by asking an AI assistant a question such as, “Show my account, door, and panel growth by month for the last 12 months, my accounts by pricing tier, and how I am tracking against my sales target.” Global Brivo resellers will use the MCP to increase operational efficiency and value for customers. “Claude is already part of our team's daily workflow, so the Brivo Reseller MCP fits right in. Our Alarm Support team will use it to catch offline panels and reader errors before customers call, resolve issues remotely before rolling a truck, prep account summaries ahead of customer reviews, and reconcile door counts and editions against what we bill." —Merle Hughes, VP of Service, NAVCO, Fullerton, Calif. Interrogating client data “We're excited to explore and interrogate client data, identify trends, and create tailored insights on our own terms rather than being limited to predefined reports and dashboards.” –Jo Kaye, Co-Founder and Director of Balthorne Security Solutions, London, UK. “Brivo Reseller MCP can help us connect information with insight, allowing our entire organization to become more proactive, more informed, and more valuable to our clients throughout the life of the relationship.”—Chris Gilbert, Founder and President of Security Pros, Sellersburg, Ind. Key benefits and capabilities: Equipment status: Find offline control panels and review firmware, reader, and door errors across customer accounts. Account details: View sites, doors, panels, editions, enabled features, settings, and billing cycles in one place. Usage and growth: Monitor credential usage, administrator counts, and account or hardware growth over time. Practical outputs: Create formatted customer reports, support tickets, and quotes. Convenience: View security data alongside CRM, billing, email, support, and project software. Role-based permissions: Queries and actions align with existing Brivo admin profile settings. Plain-language prompts: Allow resellers and end users to manage portfolios or ask account questions in natural language. The first release is read-only, meaning Brivo MCPs cannot take actions such as changing settings, edit accounts, or lock and unlock doors.

Intersec Europe will make its debut in Frankfurt am Main from 14 to 16 September 2027. For the first time, this new European platform brings together solutions for physical security, cybersecurity and AI in an integrated approach – with a clear focus on the protection of buildings, businesses and critical infrastructure. At the heart of the event are the specific requirements of operators and end users, as well as decision-makers who shape security strategies and are responsible for investment decisions. With Intersec Europe, Messe Frankfurt is expanding the globally recognized Intersec brand with a standalone event in Frankfurt am Main. Specific requirements of operators With Intersec Europe, taking place in Frankfurt am Main from 14 to 16 September 2027, Messe Frankfurt is establishing a new international trade fair for integrated security solutions for the European market. Emerging threats and new EU-level regulations are changing the requirements placed on businesses, public authorities and operators. Intersec Europe addresses these developments by combining the exhibition with a conference, networking and business matchmaking. The focus is on products, technologies and services designed to protect buildings, business premises, public spaces and infrastructure. Exhibiting companies will present integrated security solutions ranging from video surveillance, access control and perimeter protection to fire detection and alarm systems, cybersecurity and AI applications. Leading industry players are supporting Intersec Europe right from the start, thereby underlining the importance of the trade fair. Integrated security solutions These include: Abus, Assa Abloy, Dormakaba, ECO Schulte, GEZE, Hodapp, NSC, Salto and Winkhaus. Wolfgang Marzin, President and Chief Executive Officer of Messe Frankfurt, comments: “For more than 20 years, we have been staging Intersec Global in Dubai, one of the world’s leading international trade fairs for the security industry. In Frankfurt, we are now drawing on this experience, our global network and the strength of our international trade fair portfolio, comprising 13 events. With Intersec Europe, we are creating a dedicated platform for the European market.” As a pan-European event, Intersec Europe brings leading security technology providers together with the decision-makers who plan, procure and deploy products and solutions for buildings and critical infrastructure. These include specialist planners, engineering and consultancy firms, system integrators, security professionals, building and infrastructure operators, as well as technical procurement professionals. Technical procurement professionals Intersec Europe is the latest addition to Messe Frankfurt’s global ‘Safety, Security & Fire’ trade fair portfolio and builds on the internationally established Intersec brand. The portfolio comprises 13 events in total and supports the dynamic growth of the security industry in key markets worldwide. Intersec is represented in Dubai, Argentina, Saudi Arabia and China. Under the Secutech brand, Messe Frankfurt offers platforms in Taiwan, Thailand, India and Vietnam. Further specialist conferences and events in Bulgaria, Romania, Croatia and India complete the portfolio.

Amthal Group Companies has partnered with AURA to connect customers needing a physical security response to alarm activations or requests for assistance, with a nationwide network of vetted, SIA-licensed security responders. The service connects a dedicated Amthal mobile app and EMCS alarm receiving centres with AURA’s nationwide network of more than 180 accredited private security companies and thousands of Security Industry Authority (SIA)-licensed professionals. Significant crime risks When an incident requires a physical response, AURA identifies the nearest available responder and coordinates their attendance. Customers can track the responder’s progress and view estimated arrival times through the Amthal app, giving them visibility of the call-out while it is underway. “With police attendance at alarm activations less frequent and businesses continuing to face significant crime risks, connecting customers with an available, vetted security responder is central to this partnership service,” said James Wilson, Head of Customer Growth UK at AURA. “By bringing together response coordination, live tracking and digital reporting, AURA provides a clear process from the initial request through to attendance at the premises. This will help Amthal’s customers understand how a call-out has been handled and gives them a record of the response to support compliance.” Alarm receiving centre The service is designed for a range of environments, including commercial and retail premises, construction sites, residential properties and vacant buildings. It provides an option for businesses that need to manage security outside normal working hours, particularly when the main keyholder is unavailable. Requests can be made directly through the Amthal app or triggered by an alarm activation received by an alarm receiving centre. Responders can investigate incidents and carry out external checks, with access to the premises available through authorized, secure keyholding arrangements where required. Additional monitoring centre Following attendance, customers receive a digital report containing a time-stamped record, GPS data, photographs and relevant incident details. This provides an account of what happened, when the responder attended and the findings from their visit, supporting incident reviews and compliance records. Jamie Allam, CEO of Amthal Group Companies, added: “AURA gives our customers instant access and total protection when on-site attendance is needed. It helps businesses managing multiple locations, vacant properties or sites outside normal working hours arrange a physical response when an incident occurs. It complements our existing monitoring systems, bringing security technology and on-site mobile response together as part of our wider offering.” Managed by Amthal and powered by AURA’s technology and responder network, the service integrates with existing alarm receiving centres, monitoring systems and the Amthal app, without requiring additional monitoring centre personnel.
NIS-2 and CER are raising the requirements for the security and resilience of critical infrastructure and essential and important entities. Recent attacks on critical infrastructure demonstrate why these requirements matter in practice. In this context, the video security technology deployed is also coming under greater scrutiny: Operators must not only manage physical threats but also address cyber risks, supply chain security, and system availability. As part of its current Act Now initiative, Dallmeier supports operators with decades of experience in critical infrastructure protection, cybersecure video security technology “Made in Germany,” and practical expert guidance. Information security management For Dallmeier, a comprehensive security strategy encompasses three dimensions: physical resilience through state-of-the-art video surveillance, cyber resilience through “Security by Design” and ISO 27001-certified information security management, and geopolitical resilience through “Made in Germany” and a secure supply chain. For operators, the interplay between these dimensions is essential to comprehensively address the various requirements of a resilient video security infrastructure. The new EU CER guidelines published in July 2026 illustrate how directly video technology is affected by regulatory requirements. Control measure C30 specifies concrete requirements for video systems. These include, for example, real-time monitoring of critical assets, facilities, and access routes, continuous recording of security-relevant areas, reliable time synchronization across surveillance systems, regular verification of recording status, and defined and regularly reviewed retention periods. Additional requirements address reliable system availability through critical spare components and backup power, regular review and verification of video recordings, and ensuring forensic usability. Video security technology Dallmeier has been developing video security technology “Made in Germany” since 1984, combining physical security, cybersecurity, and geopolitical resilience into a holistic approach. The company also draws on this extensive experience to address the current challenges associated with NIS-2 and CER. Comprehensive best practice guides help operators of critical infrastructure and essential and important entities interpret regulatory requirements and better understand their implications for video security. “We are not just selling cameras – we are enabling compliance and holistic resilience for our customers,” says Jürgen Seiler, Head of Business Development at Dallmeier electronic Webinars provide practical insights For security professionals seeking a concise overview of how NIS-2 and CER affect their video security systems, Dallmeier offers dedicated webinars. The English-language webinar “Securing the Weakest Link: Supply Chain Risk in Video Surveillance under NIS-2 & CER,” featuring Jürgen Seiler, focuses on supply chain risks and explains their significance for critical infrastructure resilience in the context of NIS-2 and CER. It also provides an overview of the European legal framework and the three dimensions of resilience. The second webinar, presented in German, focuses specifically on NIS-2 and the resulting requirements for video security. In approximately 20 minutes, participants learn about the requirements for critical infrastructure operators and essential and important entities, the role of video surveillance systems in NIS-2 risk assessments, and how to design video security solutions that are verifiable, audit-ready, and future-proof. Recordings of both webinars are available on the Dallmeier Act Now website. Project-specific consultations Operators already facing specific challenges can discuss their individual requirements directly with Dallmeier experts. Jürgen Seiler and the Dallmeier expert team are available for project-specific consultations. Further information, comprehensive best practice guides, webinar recordings, and contact options are available on the Dallmeier Act Now initiative website: In 1984, Dieter Dallmeier founded what is now Dallmeier electronic – not in the proverbial garage, but in a garden shed in Regensburg, Germany. Today, the company, which can justifiably call itself a hidden champion for video information technology "Made in Germany", has several hundred employees worldwide, more than 250 of them at the company headquarters in the center of Regensburg alone. The customers: From commercial enterprises to World Cup stadiums Dallmeier's camera, recording, software, and analysis solutions optimize security and processes for B2B end customers in a wide range of industries in over 60 countries. The focus is on users from the casino, smart city, airports, logistics, stadiums, and industrial sectors. But also, banks, critical infrastructure facilities as well as medium-sized companies from all sectors. Low total cost of ownership "Made in Germany" With pioneering innovations, Dallmeier has succeeded time and again in placing itself at the forefront of technology: From the world's first digital image storage system with motion analysis in 1992, the patented "multifocal sensor technology" Panomera® with its "Mountera®" mounting system, to the latest Domera® camera family, which allows up to 300 camera variants with only 18 components. These and many other innovations provide real, tangible customer benefits. And with a low Total Cost of Ownership (TCO) and a high Return on Investment (ROI) they can easily compete with systems produced and supplied from low-wage countries. Maximum vertical integration With "Made in Germany", they also guarantee the customers the highest standards in data protection, cybersecurity, and ethical responsibility. With high quality and short supply chains, we also ensure – almost incidentally – sustainability and environmental protection. From our prestigious headquarters in the centre of Regensburg.

Expert commentary

There was a time when physical security and cybersecurity occupied two very different worlds. One was concerned with the nuts and bolts of locks, doors and perimeter protection. The other focused on networks, software and digital threats. Today’s modern access control systems – used in everything from offices and hotels to hospitals and data centres – combine the two, fusing mechanical engineering and cloud platforms. That means that a door is no longer simply a physical barrier. Instead, it’s a connected endpoint within a much wider digital ecosystem. And it’s changing expectations across the industry. Increasingly, developers, architects and operators are turning their backs on separate products in favour of integrated access solutions that combine doors, locks, access controls, environmental monitoring and digital management into a single, connected system. A new connected approach to security This change is part of a wider shift in the way that security itself is perceived This change is part of a wider shift in the way that security itself is perceived. Traditionally, physical security was about keeping unauthorized people out. Today, it’s about making sure the right people have the freedom to move within a restricted space. That is particularly important in places such as hospitals, data centres and other critical infrastructure, where security helps protect essential services while minimizing disruption. And it’s why our Research & Security Center (R&S) in Berlin, Germany, brings together both disciplines under one roof. Their job is to test products against both physical attacks and cyber threats. Employing unconventional tactics Sometimes, that means employing unconventional tactics, such as using professional lockpickers to test the security and resilience of new physical products. While modern locks are still based on mechanical engineering, they are more advanced than they look. Improvements in design, materials, and manufacturing mean they are stronger, more reliable, and harder to tamper with. But there’s more to locks than just security. Some systems can even use the motion of inserting and turning a key to generate a small amount of electrical energy, which provides energy to power extra functions without wiring or batteries. This means they are not just standalone locks but can also be used as part of wider digital access systems. Bridging physical and digital security For instance, great strides have been made recently in terms of biometric authentication However, as everyone knows, digital systems have their own security risks, especially now that artificial intelligence (AI) is part of the emerging threat. This means the cybersecurity team needs to ensure that systems are robust enough to withstand a wide range of risks – from attempts to breach access platforms to phishing attacks – as well as other tactics designed to exploit human behavior. It’s here that researchers adopt a ‘hacker’s mindset’ to keep systems safe. And that means continuously testing, probing, and strengthening systems to identify vulnerabilities against existing real-world threats while also anticipating what might be around the corner. Mobile-based access control systems For instance, great strides have been made recently in terms of biometric authentication, including facial recognition and fingerprint scanning. Similarly, smartphones are increasingly being used to secure credentials for mobile-based access control systems. But improvements in technology also come with their own risks. For instance, For instance, AI-generated deepfake videos and voices are becoming more convincing, making it easier to trick people into giving access, sharing information or approving actions they should not. And as I alluded to earlier, criminals are now using AI and automated tools to identify weaknesses and exploit them much faster than before, sometimes with little or no human involvement. But it’s also true that it’s being used to bolster defences. Work is currently underway to use AI to analyze data in real time to identify unusual entry times, identify multiple failed authentication attempts, or spot any other anomalies that might suggest someone is trying to gain entry illegally. Modern access control Cloud-based platforms allow security teams to issue and revoke credentials remotely Increasingly, the value of modern access control lies not just in the hardware, but in the software that sits behind it. Cloud-based platforms allow security teams to issue and revoke credentials remotely, monitor activity across multiple sites and respond quickly to emerging threats. This makes security a real-time, always-on, continuously managed service rather than a collection of standalone products installed and largely forgotten about. The importance of regulation and compliance This is something that policymakers are aware of. In the European Union, for example, the EU’s NIS2 Directive relates to cybersecurity protecting network and information systems and significantly broadens both the scope and the obligations for compliance. It also takes an “all-hazard” approach to security, which means protecting not just digital networks and systems, but also the physical environments in which they operate. Similarly, the EU’s Cyber Resilience Act is designed to ensure that all digital products are safe from cyber threats. Its goal is to ensure that connected devices and software are built, updated, and maintained with security in mind, helping protect users in an increasingly connected world. And by introducing clearer requirements and standards, the CRA will help consumers and organizations identify products with strong security features and configure them more securely from the outset. Security by design Security can no longer be treated as something that is bolted on at the end of the development process In both cases, it is incumbent on vendors not only to meet or exceed these rules and regulations but also to keep customers, the wider industry, and other stakeholders informed about developments. For me, these regulations also reflect a broader shift in thinking. Security can no longer be treated as something that is bolted on at the end of the development process or addressed only after a vulnerability has been identified. Instead, it needs to be considered from the very beginning and maintained throughout a product's lifecycle. For manufacturers, that means continuously assessing risks, testing products against emerging threats and ensuring they remain resilient as technology and the threat landscape evolve. As I said at the beginning, the reason is simple. Today's buildings are no longer just bricks and mortar. They are connected environments where doors, locks, cameras, sensors and access control systems increasingly communicate with one another and with cloud-based platforms. You might want to think about that the next time you walk into a secure building.
The eagerness to adopt AI in physical security is increasing as teams want to implement technology solutions for faster, smarter operations. At the same time, the conversations surrounding AI have changed. The focus now includes not only efficiency gains but also concerns about accountability and trust. According to the Genetec 2026 State of Physical Security report, AI ranked alongside access control and video surveillance as a key priority. However, approximately 40% of the over 7,000 physical security leaders surveyed expressed concern about how AI systems use their data. The potential for malicious purposes followed close behind at 36%. You may recognize this tension in your own organization. There is an expectation that AI can help operations and an understanding that AI entails risks. Balancing the two includes careful deployment and policies. Higher stakes demand a higher standard AI can quickly spot the difference and elevate the event to the security team Most AI applications in physical security revolve around automation. Basic examples include triggering events, filtering and classifying alarms, and enabling faster searches across video and event data. These applications tackle the persistent security challenges of too much noise and too little context. AI takes on some of the lifting, cutting the false positives that overwhelm operators and adding context to the events that remain. For example, someone loitering near an entrance may not be a notable event. While someone loitering and trying door handles is a priority. AI can quickly spot the difference and elevate the event to the security team. From there, the human operator can confirm the issue and next steps. AI narrows the operator's focus rather than replacing their judgment. Higher standard of supervision While these uses improve operator efficiency, they need to be implemented responsibly. Irresponsible AI usage in physical security is more than a simple inconvenience. The outputs affect safety and security. AI applications within physical security demand a higher standard of supervision. This oversight is often referred to as “human in the loop,” but perhaps a better phrase is "expert in the loop." The person validating an output needs the knowledge to question it, contextualise it, and overrule it if needed. How to deploy responsible AI Deploying responsible AI starts by defining where AI can add value to your specific organization Deploying responsible AI starts by defining where AI can add value to your specific organization. AI works best as a tool with a defined job. What is the problem that needs to be solved? What challenges are holding back the team? Start by identifying the problems, then work backward to a solution. Otherwise, you may be implementing technology that doesn’t fully meet your needs. Next, define parameters around AI usage within your team. Document exactly what AI is permitted to do and not allowed to do within your operations. Information should include which use cases you've approved, what data the system can access, and how issues escalate. By defining these elements, your team has clear guidelines on when AI tools are part of your security procedures and for what purposes. Cross-functional monthly meetings Because AI can behave unpredictably, it’s good to prepare for when something does go wrong. Even a well-built model will eventually drift from its thresholds. This is where governance comes in. Governance is what keeps responsible AI holding up over time. It sets the review cycles that catch an issue before an incident does. Governance related to AI entails data privacy, liability, and regulation. Input from legal, compliance, cybersecurity, and IT teams is important. Getting these groups together starts with something as simple as cross-functional monthly meetings to review use cases and emerging challenges. Consider also working with other manufacturers, integrators, and end users across your ecosystem. In doing so, you create shared standards that make issues diagnosable. Responsible AI as a practice, not a project The goal is to protect individual rights and build trust without hampering technological advancement Responsible AI usage in security is not a box to check or a project to complete. It's an ongoing practice, especially as the compliance bar rises. As more AI security risks surface, governments are drafting legislation to regulate how organizations can develop and implement AI-enabled technology. The goal is to protect individual rights and build trust without hampering technological advancement. Identified risk category For example, the 2024 AI Act in the European Union (EU) sets obligations for various AI applications based on their identified risk category. These requirements include creating adequate risk assessments and mitigation practices, using high-quality training datasets to reduce bias, and sharing detailed documentation on models with governing authorities as needed. In the US, multiple states have implemented legislation on AI use, and national legislation has been discussed. Organizations can begin by implementing documented processes for guidelines and governance: Conduct risk assessments: Evaluate how automating a specific process may impact critical systems or safety protocols Identify non-critical applications: Start by implementing AI into processes that aren’t central to your most critical operations to curb major business disruptions Prioritise human-centred design: Ensure that AI applications always empower humans with the information they need to make the best decisions Design for explainability: Ensure AI decisions can be explained and traced, so the expert in the loop can question, verify, or overrule them when needed. Broaden data protection strategies: Apply cybersecurity measures and best practices to AI-enabled solutions, including regular audits and system updates Choose trusted vendors: Work with vendors who follow responsible AI principles, considering biases, data protection, and cybersecurity Core pillar of physical security The industry is slowly converging on shared standards for AI governance. This is good news for early adopters who wish to shape the industry rather than react to it. The potential applications of AI in security are exciting. But as this technology evolves, so do the risks. Strong governance builds trust, a core pillar of physical security. Responsible AI protects that trust and earns more of it. Start by defining your outcomes, building guardrails, and creating accountability structures to support your organization’s responsible use of AI technology.
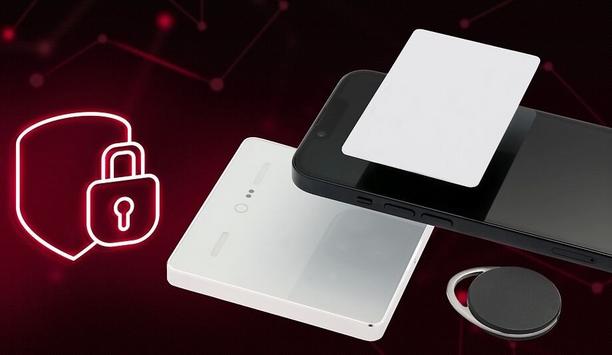
In logistics hubs, production facilities and distribution centers, the access control system is invisible—until it isn't. For decades, the 125 kHz card has been the workhorse of industrial credentialing: inexpensive, reliable and universally understood. It does exactly what it has always done. That consistency has served many organizations well, even as security needs and credential From authentication to smart buildings, gain expert insights about unified access. The same card technology that opened the warehouse gate in 2005 is opening it today. And while operations teams have upgraded conveyors, ERP systems and warehouse management platforms, the front door has often remained on technology selected for an earlier era. Major operational event Why? It is rarely about a lack of awareness. More often, organizations are balancing cost, time and operational risk. In a facility that never stops, a full systemwide upgrade can feel less like a routine project and more like a major operational event. The path forward is continuous modernisation: deploying an agile access layer that adapts to new security requirements and credential technologies over time, rather than replacing everything at once. Universal reader technology makes that possible, without the “Big Bang” shutdown. Why legacy systems can benefit from modernisation The 125 kHz card (also named proximity, prox or low-frequency) helped set a practical standard for convenience and broad compatibility, but many organizations are now evaluating where its security model can be improved by newer options: Increased cryptographic protection. Traditional low-frequency credentials transmit a fixed identifier, which can make them harder to align with today’s expectations for encrypted and dynamic authentication. Increased credential validation. Traditional proximity systems do not provide the kind of mutual authentication or challenge‑response mechanisms that are increasingly common in newer credential platforms. Better protection from duplication/cloning. Because the credential model is comparatively simple, 125 kHz cards present fewer barriers to duplication or cloning than modern encrypted credentials which are inherently designed to better distinguish authorized users from copied identifies. An opportunity to secure the full path. Many legacy deployments also rely on Wiegand communication between reader and controller, creating a strong case for modernisation to encrypted, supervised protocols that help protect credential data in transit. Keeping the interoperability benefit of Prox. Newer open standard provides the same interoperability benefits while addressing improved security. The opportunity for the front door At the same time, security teams face an expanding threat landscape and compliance requirements A traditional access control upgrade is not just a technology swap. It means new readers at every door, new credentials issued to every employee and contractor, platform reconfiguration and installation labor across a facility that cannot afford to stop. Against that backdrop, the rational choice is often to do nothing. At the same time, security teams face an expanding threat landscape and compliance requirements that increasingly demand encrypted credentials. And with Apple Wallet corporate badges and BLE mobile credentials moving into the mainstream, employees and contractors will soon expect to use their phone as their badge, at least as an option if not the primary means of credential presentation. Four specific friction points keep organizations locked in place long after they know they should move. The logistical bottleneck - Replacing a proximity-based system has traditionally meant doing everything at once: new readers, new credentials, new platform configuration, every employee and contractor rebadged before the cutover date. For a site running 24/7 with extensive staff and rotating contractors, that isn’t just an upgrade. It’s a logistical nightmare requiring a hard shutdown. The rebadging event alone, coordinating hundreds or thousands of people through a credential transition on a fixed timeline, can consume weeks of HR and security operations bandwidth. The Credential Soup - Most logistics organizations are not running one clean credential population. They are running three or four: legacy prox for permanent staff, a different format inherited from an acquisition, a contractor badge system managed by a third party, a mobile pilot that never fully rolled out. None of them talk to each other, and no single reader handles all of them. Frozen Infrastructure - Static readers support only the credential formats they shipped with or have limited format support for updates. When a new vulnerability is disclosed or a new mobile standard is released, the hardware has no path to adapt. The only option is physical replacement, which means another capital project, more installation labor, and the same shutdown risk all over again. The Cyber-Physical Gap - IT departments run zero-trust architectures and encrypt everything on the network. Then the same organization unlocks its server room with a Wiegand-protocol reader transmitting credentials in plain text. The IT security perimeter ends at the network edge. The physical front door is a different conversation entirely, and often nobody's budget. The way forward: Continuous modernisation of access credentials A continuous modernisation plan is both easier and more cost-effective than a one-time “rip-and-replace” event The answer to the Big Bang problem is not a better-planned Big Bang. It is a fundamentally different approach to access infrastructure that treats modernisation as an ongoing capability rather than a one-time event. A continuous modernisation plan is both easier and more cost-effective than a one-time “rip-and-replace” event. It significantly lowers the labor and logistical costs of rebadging the entire organization at once and eliminates the need for forced downtime entirely. Instead, organizations upgrade incrementally (by site, by department, or as credentials expire), keeping operations running and spreading costs over time. And with future-proof universal reader technology, the reader stops being a fixed asset and becomes a platform that continues to evolve as needs change. Start with a universal infrastructure The foundation of continuous modernisation is a universal reader that can handle whatever credentials are already in the building (legacy proximity, modern smart cards, mobile credentials) while remaining ready for whatever comes next. As access technologies continue to evolve, support for additional credential formats and security approaches can be added through firmware updates rather than hardware replacement, ensuring a secure and future-proof access system. The burden can further be eased by the use of a universal credential that can support existing formats along with new formats, enabling the credentials to work on existing readers as well as new readers. Let old and new credentials coexist Legacy 125 kHz cards continue to function in parallel until the organization is ready to retire them With a multi-technology reader in place, the rebadging process becomes a rolling transition rather than a synchronized event. New employees get modern credentials from day one. Existing staff transition as badges are renewed or departments are prioritised. Legacy 125 kHz cards continue to function in parallel until the organization is ready to retire them. Eventually, 125 kHz support or insecure credential support can be switched off, cleanly and deliberately, via a remote firmware update. That means no forced downtime, and no mass confusion at the turnstiles. This applies equally to secure migration to either modern symmetric credentials (such as HID Seos or LEAF) or emerging asymmetric credentials (such as PKOC, Aliro or LEAF Verified). Secure the whole chain, not just the card Upgrading credentials without addressing the communication layer is only half the job. Moving from Wiegand to OSDP Secure Channel (a bidirectional, AES-128 encrypted protocol) closes the replay attack vulnerability and adds tamper detection between reader and controller. Modern credentials and a secure communication layer together protect the entire authentication chain, from the card or smartphone all the way to the access control platform. This becomes critical when the reader is handling the decryption of a secure credential and then communicating to the panel in clear text. OSDP encrypts this last step of communication, while also offering industry best practices for managing reader devices. Choose infrastructure that doesn't choose for you Interoperability is not just a convenience feature. It is a strategic asset Interoperability is not just a convenience feature. It is a strategic asset. A facility running universal reader infrastructure compatible with most transponder technologies and credential formats (physical and mobile) is insulated from vendor lock-in and the next credential transition. Universal readers also act as merger-and-acquisition insurance: when a company acquires a facility running a different badge system or a contractor arrives with an unfamiliar card format, existing readers can be configured to accept the new credentials from day one. As access technologies and credential standards continue to evolve, organizations with adaptable reader infrastructure will absorb that shift as a firmware update. Those without it will face another capital project. A market in motion: beyond legacy credentials Emerging open standards (which reduce vendor dependency) and widely adopted proprietary platforms are both moving the market toward stronger cryptography. These credentials can be delivered on physical smart cards, mobile devices or both. Organizations selecting reader infrastructure today should ensure it is prepared to support this transition without requiring a hardware swap. Several initiatives are gaining significant traction: LEAF Identity: An interoperable credential framework built on strong symmetric encryption, already deployed across a meaningful number of installations and a proven replacement path for legacy proximity systems LEAF Verified: A next‑generation physical access credential platform built on NXP’s MIFARE DUOX that uses public‑key cryptography to eliminate traditional shared key management and enable interoperable, vendor‑neutral access control. PKOC (Public Key Open Credential): An open, vendor-agnostic credential specification from the Physical Security Interoperability Alliance using asymmetric public key cryptography, in which the private key never leaves the device and a derivative of the public key is the credential Aliro: An open mobile-first credential standard released in February 2026 by the Connectivity Standards Alliance (CSA), the organization behind the Matter smart home standard. Backed by Apple, Google, Samsung, and 220+ industry members providing native wallet, offline device support and mailbox features on top of asymmetric public key cryptography. HID Seos: A widely deployed proprietary credential platform that continues to drive responsible, large-scale secure symmetric-based encrypted deployments across small to enterprise environments for both card and mobile deployment, including wallet. Security that scales The same principles apply equally to a single site or a logistics operator running 5,000 employees The same principles apply equally to a single site or a logistics operator running 5,000 employees across a dozen sites. Because no single cutover date is required, a large organization can sequence the migration by site, by department or by credential expiry cycle. The operational risk that makes a traditional upgrade unthinkable at scale becomes manageable when the transition is invisible to the people walking through the doors. The pressure to act is reaching a tipping point. Apple Wallet corporate badges and BLE mobile credentials are arriving in earnest in 2026, as well as asymmetric smart card options. These technologies are rapidly moving from isolated pilots into mainstream enterprise deployment across logistics, manufacturing and production environments. Evolve security infrastructure Organizations that have already invested in universal reader and credential infrastructure that is firmware-updateable and mobile-ready will absorb that shift without a second thought. Those that haven't will face another rip-and-replace decision just as the mobile credential wave hits. Organizations that have already invested in universal reader and credential infrastructure Continuous modernisation is not a one-time project. It is a permanent capability: the ability to evolve security infrastructure at the organization's own pace, without forced downtime, without mass rebadging events, and without being held hostage to the next credential transition. Organizations that build that capability today are not just solving a security problem. They are future-proofing the way their facilities move. Universal access from ELATEC ELATEC's TWN4 universal readers are built on an agnostic design strategy: multi-technology, multi-frequency, and software-configurable, so organizations are not locked into a single credential technology or vendor. Key capabilities across the TWN4 family: Support for 100+ physical and mobile credentials and 60+ transponder technologies RFID, NFC, and BLE in a single reader platform Software-configurable via the ELATEC DevPack: credential formats, encryption settings, and security protocols can be updated remotely without hardware replacement Supports backward and forward compatibility as new standards emerge Available in a range of form factors for door access, desktop enrollment, OEM integration, and industrial applications
Security beat
Deploying artificial intelligence (AI) tools should be seen as a business initiative rather than a technology initiative, says Martin Soukup, CTO of Solink, a cloud-based video security and data intelligence platform. The approach makes a difference that plays out in practical terms. A technology initiative is tactical and solution-oriented, often solving an isolated problem within a single department's silo. In other words, it might solve just a security problem. In contrast, a business initiative is cross-disciplinary, driven by executive leadership to impact the entire organization in a measurable way. “Viewing AI tools as a business initiative ensures they adapt to multiple departmental needs and drive high-level strategic growth rather than just fixing a localised technical issue,” says Soukup. AI platform combines video and business systems Demonstrating the value of embracing AI as a business initiative is Solink’s new video intelligence platform Demonstrating the value of embracing AI as a business initiative is Solink’s new video intelligence platform that combines video with business systems to detect threats and send real-time alerts. The capabilities are designed to help security teams operate smarter and more efficiently, supporting the next generation of lean, intelligence-driven security operations centers (SOCs). And benefits of the platform extend beyond security to include other parts of the business. “At the end of the day, video cameras only tell part of the story, much like looking at a 2D shape,” says Soukup. “They capture dimensions and colors, but only from a single perspective, even with powerful AI analysis providing traffic metrics, wait times, product interaction, and compliance logs. The addition of operational data, such as inventory, shipping, labor, and sales data, fills out that shape into 3D, adding critical context.” For example, while a camera simply shows three people standing in a line, and AI data flags that those individuals have been waiting for over five minutes, operational data lets you know also that a cashier has not checked into their shift yet. Combining these data streams gives businesses full situational awareness, turning passive observation into immediate, contextual intervention. AI agents handle repetitive tasks The Solink platform uses AI Agents, which are software that operates autonomously to handle manual, repetitive, or high-volume tasks based on specific instructions and tools. For Solink users, AI Agents unify their existing camera and data source investments into a single automated workflow. “AI Agents transform Solink from a security tool into an operational investment that benefits all departments,” says Soukup. “Modern operational leaders are turning to AI to scale productivity without increasing overhead.” Integrating business intelligence Operations checks compliance, loss prevention investigates theft, and security assesses threats Customers already use Solink to centralize video, integrate business intelligence, and trigger real-world responses like real-world alerts, two-way communication, or smart locks. AI Agents tie these pieces together, analyze the data and identify what matters most, and then take action either without human intervention or with humans in the loop. Businesses currently watch video manually across separate workflows. Operations checks compliance, loss prevention investigates theft, and security assesses threats. However, a human must always watch the footage to get results. Solink AI Agents automate this entire workflow. If an operational event can be seen on camera and matters to the business, a Solink Agent can be integrated to automatically review, assess, and trigger the next step in the workflow across hundreds or thousands of locations simultaneously. Calling all stakeholders to the discussion When discussing applications, stakeholders should include revenue and marketing officers, compliance officers, and line-of-business executives. Agents leverage existing infrastructure by adding an intelligent automation layer that drives efficiency and grows revenue across the entire organization without large capital investment. Solink AI Agents will not replace employees; they empower lean teams to maximize their existing resources. Job descriptions will shift toward human-in-the-loop workflows where humans and machines collaborate. The AI Agent handles the high volume, filtering out noise and processing data at scale. Human employees set up and guide the Agents, give feedback to improve performance over time, and step in to make final decisions, managing the nuanced situations that require critical thinking, empathy, and deep context. Passive data visualization In contrast, a Solink AI Agent is deployed with a clear mandate for a specific task, deliverable, or outcome Given the convergence of physical and digital security, AI Agents, not dashboards, are the right unit of enterprise AI deployment. Dashboards typically aggregate data without evaluating the context or importance of the source. Data looks identical whether it comes from 10 sources or 100. In contrast, a Solink AI Agent is deployed with a clear mandate for a specific task, deliverable, or outcome. This approach shifts the focus from passive data visualization to active intent, creating a direct path of accountability and clear attribution for business results. With dashboards, everyone can see the problem, but nobody owns it. An agent with a mandate either did the job or it did not, and you can audit exactly what it saw and why it acted or did not. Overcoming obstacles to deploy AI agents The primary obstacles to integrating AI Agents into the physical security workflow are change management, building trust, and system interoperability. Physical security requires absolute reliability, which demands rigorous initial configuration to establish trust. Furthermore, Agents are only as effective as the data they can access. Overcoming these hurdles requires comprehensive team training, shifting organizational mindsets, and ensuring seamless integration with existing tools so the Agents have the full context needed to execute tasks accurately and integrate with human workflows seamlessly. Addressing common security challenges Several use cases are driving the deployment of AI Agents among Solink's customers Several use cases are driving the deployment of AI Agents among Solink's customers. Overnight guarding, loss prevention, and store readiness will be the first wave of use cases. These are proven, high-frequency scenarios in which Solink provides pre-built template Agents to address common security challenges out of the box. The second wave of use cases will include highly customisable occupancy tracking, health and safety, and food quality. Pre-built template Agents are coming for these next. In addition, custom, niche operational use cases can be tailored to a specific business environment. Just like hiring a specialized contractor, companies can deploy custom Agents to tackle unique operational challenges rapidly across all locations. Measuring the effectiveness of AI agents The effectiveness of AI Agents can be measured by multiple factors. Core Accuracy, and consistency and accuracy of detections and automated outputs. Business Outcomes delivered, such as reduced inventory loss, reduced fraud, and faster incident resolution. Financial Impact, measured through recovered budget, reduced operational overhead, and increased per-store conversion. There is a perception that AI Agents possess predictive or flawless capabilities, like stopping crime before it happens or operating perfectly in dark, chaotic environments. Not true, says Soukup. AI cannot understand ambiguous requests like "look for suspicious activity." Success requires explicit parameters, tools, and skills, defining what is acceptable, what is unauthorized, and how to handle the gray areas. Another misconception is that Agents need a fundamentally different security model than people. “I run security for this company as well as engineering, and I hold our own Agents to the same standard I would hold a third-party vendor,” says Soukup. “That means least privilege, full audit trails, anomaly detection, random audits, and no action they can't explain after the fact.”
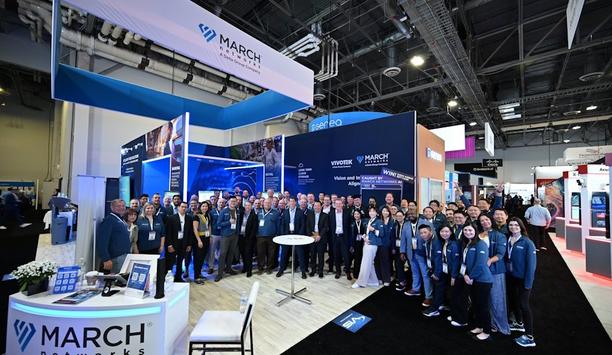
Combining VIVOTEK’s branded video security business with March Networks paves the way for the combined brands to meet customers’ increasing appetite for integrated solutions rather than individual components. The merger brings VIVOTEK's branded video security business together under one operating structure with March Networks’ enterprise-grade video surveillance, AI analytics, and cloud-managed security solutions. Customers now have access to a broader, more integrated portfolio spanning enterprise video management, advanced cameras, edge artificial intelligence (AI), cloud services, recording platforms, and business intelligence, says Net Payne, Chief Sales & Marketing Officer at March Networks and VIVOTEK. Distinct product strategies Given the combined companies, product development, sales, marketing, and customer support can move in step rather than in parallel. March Networks and VIVOTEK were already both part of the Delta Electronics family, but they previously operated as separate businesses with distinct product strategies, teams, and routes to market. March Networks and VIVOTEK announced the merger of their branded video security businesses last spring following Delta Electronics' acquisition of remaining VIVOTEK shares. “Aligning our complementary capabilities lets us innovate faster, simplify engagement, and respond more quickly to a market moving toward AI, cloud and intelligent video,” says Payne. This merger reflects a broader shift across the physical security industry, adds Payne. “Customers no longer see video purely as a tool for reviewing incidents after the fact,” he says. “They expect it to help identify risks earlier, simplify investigations, improve operations, and support better decisions across the organization.” Cloud video management Meeting customer expectations requires more than bolting AI features onto existing systems Meeting customer expectations requires more than bolting AI features onto existing systems. Rather, it requires cameras, edge intelligence, recording, software, cloud services, and business data working together as one coordinated platform. “By bringing March Networks and VIVOTEK together, we combine deep expertise across the full video technology stack while preserving the relationships, sector knowledge and customer focus both companies have built over many years,” says Payne. “Our goal is to make intelligent video more integrated, scalable, and practical for customers and partners worldwide.” Both entities bring strengths to the combined companies. March Networks brings experience in enterprise software, cloud video management and large-scale deployments; while VIVOTEK brings strength in imaging, camera technology and edge intelligence. Together they seek to ensure more choice when designing systems, a clearer path for future expansion, and technologies that work together more effectively without compromising the reliability, cybersecurity, and support customers expect from both companies. Advantages for channel partners Channel partners gain a broader portfolio to address a wider range of customer requirements, combining components as each deployment demands. Channel partners also benefit from expanded geographic reach, deeper technical expertise, and greater investment in training and enablement. “Importantly, this is designed to be a seamless transition,” says Payne. “Partners keep working with the teams and relationships they already know, while gaining access to new capabilities and certification opportunities. Over time, that alignment should make it easier to design, deploy and support complete solutions.” Because they are established and respected brands, March Networks and VIVOTEK branding will continue to be used. Rebranding is not a goal, and neither identity is being replaced by the other. Coordinated decision-making “The immediate priority is organizational alignment by making it easier for customers and partners to benefit from the combined portfolio,” says Payne. Product branding will continue to reflect the relevant portfolio and market context. As product roadmaps become more closely coordinated, customers can expect greater interoperability and a more cohesive experience, says Payne. Any future branding changes will be managed carefully and communicated clearly. Combining the businesses reduces duplication and enables coordinated decision-making across product strategy, engineering, sales, marketing, operations, and customer support. “Instead of developing capabilities independently, teams can share their expertise, align roadmaps, and direct investment to where it has the greatest customer impact,” says Payne. Combining specialized knowledge globally The combined organization operates across six continents and more than 75 countries The combined organization includes more than 300 research and development (R&D) engineers across four Centres of Excellence in Canada, Taiwan, Italy and Poland, thus bringing together a substantial base of specialist knowledge. The unified network also sharpens the ability to prioritise global opportunities, respond to regional needs and bring innovations to market faster. The combined organization operates across six continents and more than 75 countries, supported by more than 1,100 certified channel partners. That footprint provides greater capacity to support multinational customers while staying responsive to local market needs. Looking ahead, future growth will increasingly come from helping customers turn video into useful, actionable intelligence. “The market is moving beyond conventional surveillance toward solutions combining AI, cloud services, edge processing, video management and operational data — and our new structure brings these together as one connected solution rather than several isolated technologies,” says Payne. Broader technical expertise There will also be closer collaboration among specialists in imaging, hardware, software, analytics, and cloud, which is important given how much customer infrastructure, regulatory, and deployment requirements vary. The companies can support cloud, hybrid, and on-premise environments, giving organizations a practical path toward more intelligent video. More choice comes from bringing together complementary technologies across product groups. Greater scale is achieved through a larger engineering organization, broader technical expertise and more capacity to invest in innovation. Challenges for the industry at large Looking to the future for the industry at large, the greatest challenge will be managing the rapid growth of AI Looking to the future for the industry at large, the greatest challenge will be managing the rapid growth of AI responsibly, securely and at scale, says Payne. Video systems will generate more data and automate more decisions, but organizations must be able to trust how that intelligence is created, protected, and applied, he adds. “Cybersecurity, privacy, data sovereignty, system interoperability and AI accuracy are more important than ever,” says Payne. Addressing these elements requires expertise across the entire technology stack: from camera and edge processing to recording, cloud infrastructure, video management and analytics. “Together, March Networks and VIVOTEK can coordinate development across all these layers, giving customers flexible architectures that balance innovation with security, transparency and operational control,” says Payne.

The security landscape is undergoing a profound transformation, as evidenced by the innovations showcased at the ISC West Expo 2026. From dismantling of silos between physical and digital security to the ongoing transition to cloud and hybrid platforms, much of the discussion on the show floor was familiar, if somehow more urgent than ever. Clearly the industry is moving toward unified, cloud-native, and highly automated ecosystems. In a series of deep-dive meetings and demonstrations at the recent show, I got a first-hand glimpse of the future of the physical security marketplace. Spoiler alert: The future is now! HID Global: Tearing down the silos HID Global is addressing the long-requested convergence of physical and digital security. Recognizing that the industry has historically operated in silos, HID is now leading with a combined implementation team to leverage the power of both sides. HID is supporting the transition by combining its logical and physical security teams to help end users design secure, end-to-end journeys for their employees. By leveraging its massive existing footprint in physical access, HID is uniquely positioned to help organizations upgrade their cybersecurity posture without a total "rip and replace" of their hardware. HID is seeing a surge in demand for converged credentials that unite building access with digital identity. On the digital front, HID has implemented FIDO (Fast Identity Online) and passkeys to replace traditional passwords with more secure, biometric-backed authentication methods. Acre Security: Bridging the gap to the cloud Acre Security previewed a cloud-native video solution, reinforcing its cloud-first security strategyAcre Security is currently consolidating brands, bringing established names like Feenics and AccessIt under a single corporate umbrella. A primary theme for the company at ISC West is the migration of legacy systems to modern infrastructure. To facilitate the transition, they are launching "The Bridge," a technology designed to help on-premise customers transition to the cloud at a pace that suits their operational needs. The company is also expanding its portfolio into video. Attendees at the show received a preview of a new cloud-native video solution slated for release later this year, signaling Acre’s commitment to a holistic, cloud-first security suite. Acoem: Real-time acoustic threat detection With a 35-year foundation in vibration and acoustics—including military sniper detection—Acoem is providing gunshot detection through edge processing. Unlike systems that rely on the cloud and may suffer from latency, Acoem’s technology processes data at the sensor level for instant alerts. Their sensors are engineered for massive outdoor spaces, covering a 500-foot radius (roughly 11 football fields) and can detect high-powered rifle shots from up to half a mile away. The system provides critical intelligence by distinguishing between muzzle blasts and "mach noise" from bullet travel, delivering an audio file to the end-user that maps the location and direction of the threat. They use AI to filter out environmental false positives, such as skateboards hitting metal rails. Alarm.com: The all-in-one dealer ecosystem Beyond hardware, Alarm.com is leveraging AI to streamline the sales process Alarm.com is doubling down on "giving tools to dealers to help them be successful," with a focus on unified commercial solutions. A highlight at ISC West is their new fire communicator, which integrates fire monitoring into their single app, completing what they call the "fourth leg of the stool." The product allows fire systems to benefit from the same real-time customer engagement and push notifications that have long been available for intrusion and video. The key products, such as commercial-grade hardware, are now available for immediate purchase. Beyond hardware, Alarm.com is leveraging AI to streamline the sales process. Their new AI Proposal Builder uses customer meeting notes to automatically generate customized, value-driven sales proposals for dealers. Allegion: A global shift in credentialing Following the acquisition of ELATEC, Allegion is adopting a more global market approach and expanding its OEM business. The company is involved in the development of Aliro, the newly unveiled mobile credentialing standard. Allegion’s strategy is built on versatility: While Aliro serves the burgeoning mobile market, they also offer PKOC for plastic cards, allowing them to provide solutions regardless of the user's preferred credential type. The ELATEC acquisition has effectively filled previous gaps in their use-case portfolio, positioning them as a comprehensive provider for both physical and digital access needs. AtlasIED: Engineering for life safety Transitioning from audio to a fully automated threat detection company, AtlasIED showcased its new IPX line at ISC West. This modular platform uses a single PoE++ port to power various "plug-and-play" modules, allowing for easy system upgrades. Their gun detection technology achieves a 99% confidence rating by "stacking" AI models; it cross-references audio data with infrared signatures to detect muzzle flashes and air quality sensors for particulates. With systems already running in 80% of U.S. international airports, the company maintains 24/7 domestic engineering support to manage these "life-safety adjacent" environments. Axis Communications: Unifying connectivity Axis Communications is advancing network video with 4G/5G surveillance, reducing cabling needs Axis Communications continues to lead in network video, with a new focus on offering surveillance through 4G and 5G networks to eliminate the need for extensive cabling in long-range applications. Axis also introduced several specialized hardware pieces, including the P1486-LE global shutter camera for high-speed traffic monitoring and the Q2802-TE, which integrates thermal and visual monitoring into a single unit. To assist technicians, they launched a new installer app that uses Bluetooth for easier camera pairing and management directly from a mobile device. Axon: De-escalation through enterprise wearables Focusing on frontline safety, Axon is expanding from law enforcement into the enterprise sector with its retail and healthcare-focused body camera. Weighing only 0.25 lb, these cameras are designed to be less intimidating, using colorful designs and acting as a primary de-escalator for aggressive behavior. A clear front display signals when recording is active, striking a balance between safety and a non-intimidating appearance. These devices feature live-streaming and panic alarms that connect workers to a Global Security Operations Center (GSOC). To ensure the footage is legally viable, Axon maintains a rigorous audit trail that authenticates every action recorded. Genetec: The value of the unified platform Genetec is advocating for unified platforms that reduce the time between incident detection and resolution. They argue that AI is becoming a commodity and that the true value lies in unified platforms that reduce the time from incident to resolution. Their approach emphasises the "outcomes" customers need, such as allowing security teams to coalesce around an investigation quickly. Genetec remains a strong supporter of open systems for enterprise customers, ensuring they have the choice to integrate diverse technologies rather than being locked into a manufacturer’s “walled garden.” This flexibility is critical for high-end security environments that require tailored, responsive systems. Johnson Controls: Large-scale enterprise solutions Johnson Controls has made a significant push into the enterprise video market with C-Cure IQ, a standalone VMS designed for major hubs like airports and large campuses. Through a partnership with Scylla, they have integrated 11 advanced analytics—including facial recognition and weapons detection—directly into their cameras. They also showcased new multi-sensor panoramic cameras capable of "stitching" multiple images into a single 360-degree view. While innovating in video, Johnson Controls also confirmed modern upgrades to their intrusion line, including their legacy DSC Neo line. The new DSC PowerSeries Neo 5, a high-end residential and commercial platform, features an all-new user interface and built-in PowerG+. They have also begun shipping the IQ5 family lineup, which is powered by a Qualcomm DragonWing processor. ONVIF: Standardising the future of AI and cloud ONVIF continues to lead the charge in establishing common languages for the security industry. A major focus is their new "Cloud Profile," which enables cameras to connect directly to the cloud through a standardized protocol. They are also expanding into audio standards to ensure IP-based speakers can seamlessly connect to Video Management Systems (VMS). To combat the rise of sophisticated digital manipulation, ONVIF is developing "video signing" standards. ONVIF is actively seeking more diverse enterprise participation to help shape these emerging AI standardsThis feature protects the integrity of video for evidentiary purposes by embedding a digital signature and timestamp directly into the footage at the camera level. Additionally, the organization has formed an AI Working Group to develop common communication methods for "AI agents" within physical security systems. ONVIF is actively seeking more diverse enterprise participation to help shape these emerging AI standards. Roberto Licari is the new ONVIF Ambassador, seeking to attract new companies (even outside the security sector) to ONVIF as they look to expand their offerings. SwiftConnect: Bridging digital and physical identity SwiftConnect is redefining access control by shifting the focus from physical cards to digital identity. As a cloud-based "connected access network," the platform bridges the gap between IT identity providers (like Okta or Azure AD) and legacy physical access control systems. At the show's Security Experience Center demonstrations, SwiftConnect showcased its ability to integrate mobile credentials within Apple and Google Wallets across multiple technology platforms. By aligning physical security with Zero Trust principles, they ensure that access is governed by the same rigorous standards as digital networks. Their software-centric approach allows for a more seamless employee experience while simplifying the management of complex, multi-site building security. This emphasises a future where the mobile device becomes the primary tool for navigating the physical workspace. Wasabi Technologies: Redefining cloud storage economics With cloud technology becoming a baseline requirement at every booth, Wasabi Technologies highlighted its "hot cloud storage" as a cost-effective alternative to major hyperscalers. Their model claims to be 80% less expensive than competitors, notably removing hidden fees. Wasabi is increasingly bundled at the "back end" of security solutions through partnerships with integrators and end users. A key feature for law enforcement and high-security sectors is their "Object Lock" capability, which ensures that video evidence remains untampered with and immutable during defined retention periods. By providing high-performance storage without the unpredictable costs typically associated with the cloud, Wasabi is positioning itself as the foundational layer for data-heavy video surveillance applications that require long-term, secure retention. Wasabi is positioning itself as the foundational layer for data-heavy video surveillance applications ZKTeco USA: Versatile and integrated access ZKTeco USA showcased a range of integrated solutions, including turnstiles, visitor management, and access control. Their Atlas access control series offers versatility, supporting everything from traditional readers and keypads to QR codes and fingerprint scanning, with the flexibility to operate on-premise or in the cloud. For tight environments, they introduced the Mars 100 turnstile, which features a compact 2x3-foot footprint. They also highlighted the Omni series, an all-in-one standalone reader-controller that manages access, intercom, and visitor functions in a single device. Innovation in portability was evident in their new walk-through metal detectors, which consist of two poles with an 8-hour battery life—ideal for schools and temporary events. While they offer their own Armatura readers, ZKTeco emphasized that their solutions can integrate with other industry leaders to fit diverse customer needs.
Case studies

Genetec Inc., the pioneer in enterprise physical security software, announces that Newark Central School District (NCSD) in New York has expanded its deployment of Genetec Security Center across seven buildings. The district has connected video surveillance, access control, emergency communications, and sensors to help staff assess incidents and coordinate their response. NCSD serves approximately 1,800 students and nearly 600 staff. Its security environment had grown over time, and administrators were managing several technologies separately. The district needed a clearer view of activity across its buildings and a more coordinated way to respond when incidents occurred. Managing several technologies “It was a multi-year project, but we can confidently say it was worth it. With the help of Convergint and Genetec, we’ve improved our processes and have a clearer picture of what’s happening across our district,” said Mike Ishler, Co-Director of Technology at NCSD. “Our students and staff feel safer, and our community has greater confidence in what we’re doing to keep it that way.” Working with Convergint, NCSD expanded its existing Security Center deployment to connect video surveillance, access control, emergency communications, and other sensors through a single platform. By retaining its existing camera infrastructure and deploying upgrades in phases, the district was able to enhance its security capabilities while managing costs. Existing camera infrastructure Today, NCSD manages more than 400 cameras, 200 doors, 500 cardholders, 30 vape sensors, and several automatic license plate recognition (ALPR) cameras through Security Center. By bringing these technologies into one platform, the district has improved security operations in several key areas: Faster incident response: Automated alerts provide designated personnel with linked video to quickly assess incidents, while centralized monitoring and lockdown procedures help coordinate emergency response. Simplified access management: Integration with Microsoft Active Directory automatically assigns building access based on employee roles, reducing manual tasks and keeping permissions up to date. Reduced vaping incidents: When a vape sensor is triggered, Security Center bookmarks the event and notifies school administrators and the school resource officer for further investigation. Vaping incidents decreased by approximately 93%. Security Center’s open architecture gives NCSD the flexibility to introduce additional technologies as its needs change. Through an ongoing service agreement with Convergint, the district has access to remote support, maintenance, and on-site help when needed.

Genetec Inc., the pioneer in enterprise physical security software, announces that the City of Carmel, Indiana, has deployed Genetec™ Security Center to unify security and operational systems across more than 40 municipal sites, helping city departments coordinate resources, improve emergency response, and manage day-to-day operations more efficiently. Carmel’s public safety teams use Security Center to monitor video, alarms, emergency calls, response vehicles, and IoT sensors through an interactive city map. First responders can access the same information from mobile devices, helping teams coordinate resources and respond more efficiently when incidents occur. Direct first responders That coordination proved especially valuable when a rare tornado struck Carmel. Using Security Center, city teams quickly mapped the storm’s path and assessed its impact across the community. They identified the hardest-hit areas and used that information to direct first responders, utility crews, and public works resources where they were needed most. “By bringing all our departments onto one city-wide platform, we’ve reduced complexity. The result is better decisions for our community, higher response efficiency, and more cost-effective operations that benefit our residents,” said Morgan Rinehart, Network Architect at the City of Carmel. Making informed decisions Beyond public safety, Carmel is using Security Center to support services across the community. With information from multiple systems available through a unified platform, departments can better understand conditions across the city and make informed decisions about how to deploy resources. For example: Engineering and street teams can monitor road conditions, coordinate snow removal, and manage traffic during construction detours without sending personnel into the field to assess conditions Parks teams can monitor crowd levels, facility usage, and safety across the city’s waterpark and trails Public events teams can monitor pedestrian traffic in community plazas and during gatherings The unified platform also gives Carmel’s IT team a centralized view of system health. Teams can monitor device status, identify potential vulnerabilities, review cybersecurity information, and manage firmware and software updates from one platform, helping the city manage its growing number of connected devices. Providing additional flexibility Carmel is also taking a hybrid approach to its security infrastructure, with the cloud-based Security Center SaaS platform providing additional flexibility when temporary projects or large events require expanded video coverage. The city can deploy mobile cameras and connect with systems operated by local schools, sports organizations, and critical infrastructure partners. Looking ahead, Carmel plans to continue expanding the platform as its smart city initiatives evolve. This includes connecting more systems and community partners. By building on an open platform, the city can add new capabilities as its needs change while maintaining a consistent approach to security and operations.

The Sanoat Qurilish Bank (SQB) in Uzbekistan enhanced its security and operations with Dahua’s integrated solution, combining ANPR, under-vehicle scanning, facial recognition, and DSS Pro for centralized management. This improved inspection accuracy, strengthened access control, and enabled faster, more efficient security responses. Overview - SQB is one of Uzbekistan’s key financial institutions, required a stronger, more intelligent security infrastructure to protect its facilities, personnel, visitors, and vehicle entry points. As a banking environment with high daily traffic and strict security requirements, SQB needed a solution that could reduce operational risks, improve inspection accuracy, and unify fragmented security systems under one centralized platform. Key financial institutions Challenges - The bank encountered several key challenges in its existing operations and security systems. Vehicle inspection at entry and exit points was not comprehensive enough, creating potential risks from unauthorized or hazardous vehicles. Manual inspection processes also increased operating costs and were vulnerable to human error. At the same time, visitor control needed improvement, as internal visitors could access important office areas without strict management. The bank’s existing security systems, including CCTV, access control, and under-vehicle scanning, came from different brands, making unified management difficult. Meeting rooms also suffered from low efficiency due to traditional presentation and note-taking methods. Smart security solution Solutions - To address these needs, Dahua provided an integrated smart security solution covering vehicle inspection, personnel access, visitor management, conference room modernisation, and centralized system control. At vehicle entrances, Dahua deployed bollards, under-vehicle scanning systems, ANPR cameras, and gate barriers to support comprehensive vehicle checks and maintain visual records for future audits. This helped improve perimeter security while making inspections smoother and more traceable. For personnel and visitor management, Dahua introduced access control, visitor management, elevator control systems, and facial recognition technology in key areas. These systems enabled accurate identity verification and stricter access permissions, helping SQB protect sensitive office spaces and improve overall site security. Reduced equipment maintenance Dahua also upgraded the bank’s meeting environment with integrated conference room equipment, including electronic whiteboards, lifting screens, and audio and video recording capabilities. This created a cleaner, more efficient meeting space, reduced equipment maintenance complexity, and made meeting content easier to record and trace. A major highlight of the project was the deployment of Dahua DSS Pro, which integrated CCTV, access control systems, and UVSS into one unified management platform. By connecting multiple subsystems, DSS Pro enabled security guards to monitor devices centrally, identify abnormal events faster, and respond more efficiently. Efficient daily operations Results - As a result of successfully implementing Dahua’s Integrated Smart Security Solution, SQB strengthened its physical security, improved vehicle and personnel management, reduced dependence on manual inspection, and achieved more efficient daily operations. The project also demonstrated the value of Dahua’s integrated security ecosystem, combining smart devices, AI-enabled identification, and centralized platform management to meet the demanding security needs of the banking sector.

At the Toronto Zoo, every person on site – whether that’s a keeper, security officer, scientist, or volunteer - shares one vision: create a world where people, wildlife, and wild spaces thrive. Thirty minutes from downtown Toronto lies a 500-acre campus that is home to over 2000 animals across 200 species. Welcoming 1.3 million guests each year, Toronto Zoo is a world-class operation on a mission to connect people, animals, conservation science, and traditional knowledge to fight extinction. When Toronto Zoo Supervisor of Health & Safety Services, Graham Birtles, set out to modernise the Zoo’s legacy access and alarm infrastructure, he discovered that the partner he already trusted for animal enclosure fencing was the same one now leading the way in physical security and access control. World-class operation The Toronto Zoo opened in 1974 with a goal that extended well beyond exhibition. Today, its work spans conservation science, breeding programs for endangered species, community education, and climate advocacy. Its Guardians of Wild program extends that belief outward, inviting staff, guests, and partner organizations to champion wildlife beyond the Zoo’s borders: in policy, community relations, and corporate engagement. “My everyday is somebody else’s once-in-a-lifetime experience,” says Graham. “We want every person who comes through these gates to leave understanding what the Toronto Zoo is about, and what they can personally do to make a change.” Delivering that experience safely for guests, staff, and the animals themselves demanded a security platform fit for the job. Rapid emergency response Before Gallagher Security, the Zoo’s access control and alarm infrastructure had not kept pace with the scale of operations. Mobile alerting was unavailable to officers in the field, credentialling hundreds of seasonal staff required plastic cards that were slow to issue and difficult to track, and there was no integration with the Zoo’s video management system to support rapid emergency response. There was also a unique challenge facing the Zoo team: the electric perimeter fencing around animal enclosures - the secondary layer of protection between the animals and the wider Zoo environment - operated as an entirely separate system, disconnected from the broader infrastructure. Following an animal containment incident that was escalated to security leadership, the need to bridge those two systems became urgent. Graham found the solution at a security trade show, when his integrator walked him toward a familiar orange booth. Higher voltage requirements “I said, I already know Gallagher. They’re my fence people. They’ve been taking care of our fencing systems for over 50 years at the Toronto Zoo.” What Graham didn’t yet know was that Gallagher also delivered enterprise-grade physical security, making Toronto Zoo’s path to world-class operations clear. Working together, Gallagher Security and Gallagher Animal Management designed and implemented an integration between Gallagher Command Centre and the Zoo’s Animal Management energiser systems, enabling real-time communication between animal fencing infrastructure and the security platform for the first time. Higher voltage requirements The implementation required calibration for significantly higher voltage requirements than traditional smaller animal environments, ensuring safe and effective management across large species habitats. The Zoo team worked closely with Gallagher’s experts to configure their setup, and the solution is now fully operational within the orangutan habitat. “Now we can see the voltage of our fences at all times,” says Graham. “We can send alerts to our wildlife care team the moment something touches the hot wire so we can make sure the animals are safe.” When an alert is triggered, integrated CCTV allows the wildlife care team to immediately verify the event and assess the situation before responding; a critical functionality for animal safety. The Zoo’s security needs extend well beyond its animal habitats, and the Gallagher platform has delivered. Persistent administrative challenges Mobile Credentials have addressed one of the most persistent administrative challenges on site. With hundreds of contractors and seasonal catering staff requiring access at any given time, the previous reliance on plastic cards was slow and difficult to manage. Now, time-limited mobile credentials are issued on sign-in and revoked automatically on sign-out, removing the risk of residual access. For officers in the field, Gallagher Mobile Connect removed the need to return to base to manage alarms. Officers maintain full situational awareness from their vehicles around the clock, long after the central control center closes. Further integration with 27 Axis intercoms in high-risk spaces - housing venomous snakes, spiders, and other dangerous species - ensure staff working alone in those environments are never out of reach. Restricting workshop equipment “We can monitor alarms throughout the Zoo; not just for traditional break-and-enter or door-open scenarios. We are monitoring life-safety systems, fire systems, animal conditions, and more,” says Graham. What has distinguished the Toronto Zoo’s deployment is not any single feature, but the broad range of problems the Gallagher platform has been called on to solve. New challenges from across the organization are allowing Graham and his team to unlock more value from their security system. Whether it is monitoring environmental conditions within animal habitats, restricting workshop equipment to trained operators, or ensuring staff cannot access sensitive areas until their training is verified, the answer has consistently been found within the same platform. Conventional vendor relationship “I like that I can call on the Gallagher team and they will work with us to find a solution,” says Graham. “Gallagher has become a house brand here at the Toronto Zoo. It’s integrated with everything we do,” Graham Birtles, Supervisor of Health & Safety Service. The Zoo’s collaboration with Gallagher has not been a conventional vendor relationship. Graham describes it as a convergence of purpose. “When we partner with organizations such as Gallagher, they become Guardians of Wild,” he says. “Because they help me and the Toronto Zoo accomplish our mission.” The Gallagher platform will play a central role in the Zoo’s next chapter. A new Community Conservation Centre, developed with a local university, will soon bring classrooms, laboratories, and a new otter river habitat into a shared community space; with Command Centre managing access for students, professors, and visiting groups. “Gallagher understands our mission,” says Graham. “They are very helpful, and everything they have put in place for us has worked. The flexibility has been fantastic.” This installation was deployed in partnership with Met-Scan Canada Ltd

Genetec Inc, the pioneer in enterprise physical security software, announces Cairo Bank has successfully deployed the Genetec Security Center platform transforming how the financial institution monitors, manages, and optimizes operations across one of Egypt’s largest branch networks. Cairo Bank is one of the largest and oldest financial institutions in Egypt, serving over three million customers through more than 230 branches. The security advancement was driven by new regulatory requirements from the Central Bank of Egypt, alongside Cairo Bank’s broader digital transformation agenda aligned with Egypt Vision 2030. Beyond compliance, the bank needed a scalable operational intelligence foundation to strengthen oversight, improve customer experience, and support long-term expansion and financial inclusion. Necessary operational foundation The implementation unifies video surveillance, access control, and intrusion detection into a single platform, allowing operators to centrally manage more than 6,000 cameras across 122 active branches, with deployment across the full network nearing completion. The platform provides the necessary operational foundation for a centralized Command and Control Room, where operators can monitor branch activity, coordinate response, and support decision-making across the institution. The system also separates operational responsibilities. IT and security teams can monitor device health and system status without accessing sensitive video feeds, supporting strict data governance and privacy requirements. “Unification and scalability were just the starting points. From day one, I knew we wanted functionalities that add value to all aspects of our operations. Security Center delivered everything we wanted in one easy-to-use solution,” said Major General Hesham Tawfiq, Head of Security at Cairo Bank. Enhancing operational consistency Beyond traditional surveillance, the platform introduces automation and analytics capabilities that support both security and operational decision-making across its branch network. These capabilities are now embedded across the entire branch network, helping Cairo Bank strengthen compliance reporting, improve risk detection, and enhance operational consistency at scale. The platform also provides insights into branch activity patterns, customer flow, and operational trends, extending the value of security data beyond incident monitoring while keeping governance and operational control central to the deployment. Existing infrastructure investments Security Center’s open architecture allowed Cairo Bank to integrate best-of-breed hardware while preserving existing infrastructure investments. It also enables the bank to add technologies and expand the deployment over time without standardising on a single hardware provider. “We are honored to work with a forward-thinking institution like Cairo Bank that continuously seeks new ways to leverage technology,” said Firas Jadalla, Regional Director, Middle East & Africa at Genetec Inc. “By unifying systems, the bank is building a consistent operational foundation for its branch network, allowing it to respond to changing regulatory and operational requirements while retaining control over how its environment evolves.” Providing technical support Integrated Technics, the systems integrator responsible for delivering the project, led the proof of concept, system design and implementation. The company continues to provide technical support and system optimization as the deployment expands. “The Command and Control Room gives Cairo Bank a real-time operational hub built on Security Center, bringing video surveillance, access control and intrusion detection into a single interface. This enables operators to monitor activity across the branch network, coordinate responses and make faster, more informed decisions,” said Walid Alagamy, CEO of Integrated Technics.

Genetec Inc., the global pioneer in enterprise physical security software, announces that TEPCO Power Grid has deployed Genetec™ Security Center as the foundation for a next-generation physical security platform that supports its broader digital transformation strategy and scales with its growing operational requirements. The platform will centralize management of more than 30,000 cameras and support future innovation across the TEPCO Power Grid network of 1,600 substations and service centers. TEPCO Power Grid manages and operates the transmission and distribution network that delivers electricity from power plants to homes and businesses across the Tokyo metropolitan area. The company is using advanced technologies to improve operational efficiency, strengthen disaster response, and modernise critical infrastructure. Modernising critical infrastructure As its camera network expanded over the years, TEPCO Power Grid needed a platform capable of supporting large-scale camera management, integrating with image analysis technologies, and expanding access to video across a broader range of devices. After evaluating several options, the company selected Genetec Security Center for its functionality, scalability, proven track record, and customization capabilities through its software development kit. “The response from users has been very positive, and we're already seeing new ideas emerge for how the system can be used across the organization. Beyond supporting our current operations, we see an opportunity to leverage accumulated video data alongside AI technologies to support future operational and technology initiatives, and we look forward to continuing our collaboration with Genetec,” said Tomoyuki Soma, Group Manager, System Development General Affairs Group, System Development Center, DX Promotion Department, TEPCO Power Grid. Improving operational efficiency TEPCO Power Grid selected Security Center for its scalability and open architecture. The platforms broad camera support allowed the company to bring together camera models from multiple manufacturers into a unified environment, helping preserve existing hardware investments while giving teams room to evolve. The Security Center software development kit also enables the company to customize the system and integrate additional technologies as requirements evolve. Security Center gives TEPCO Power Grid a unified view of its camera network while allowing teams across the region to support sites in their respective areas. Activities such as adding cameras and updating maps, which were previously managed centrally, can now be performed by individual workplaces, helping improve operational efficiency. Digital transformation strategy Authorized personnel can also use the Security Center web app to view video from computers and mobile devices. During an incident or emergency, managers and field teams can remotely assess the situation and coordinate their response. The platform also helps teams identify camera malfunctions across the network, making it easier to locate and address issues TEPCO’s 1,600 geographically dispersed sites. In addition to video management, the company sees potential opportunities to leverage accumulated video data and integrate emerging technologies as operational requirements evolve. The company is also evaluating additional capabilities available within the Security Center platform as part of its longer-term digital transformation strategy.
Round table discussion

Inflation surged dramatically because of supply disruptions and high energy costs following the COVID pandemic and given the Russia-Ukraine conflict. More recently, inflation has cooled significantly, although it still has not achieved the historically targeted rate of 2%. Factors such as tariffs and the Iran war continue to drive broader inflation. The physical security market faces its own multiple trends that continue to drive inflation of the industry's products and services. We asked our Expert Panel Roundtable: What is the current state of price inflation in the security market, and what is the outlook for the near future?

Passwords originated in ancient times, used by Roman military forces around the first century BC. Since then, passwords have evolved from physical words to the computer access control tools used today. Passwords are easy to implement, widely supported, and familiar to users. However, they are easily forgotten, stolen through phishing, prone to reuse, and vulnerable to credential-harvesting or brute-force attacks. We asked our Expert Panel: What is the role of passwords in physical security?

Critical national infrastructure encompasses sectors such as energy, utilities, healthcare, and data centers – environments that underpin economic stability and public safety. With so much at stake, the importance of effective security systems is that much higher. We asked our Expert Panel Roundtable: What are the unique aspects of the critical infrastructure market, and how should the security industry adapt?
Products
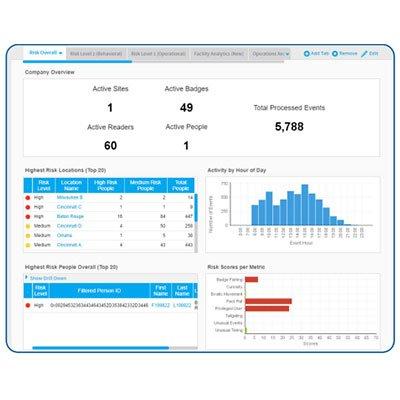
White papers
Integrated Systems Enable Critical And Compliant Security For Transportation
Download
Access. Intrusion. One Estate.
Download
An End User's Guide To Physical Security For Data Centers
Download
Combining Security And Networking Technologies For A Unified Solution
Download
What is a universal RFID reader?
Download
Maximizing Enterprise Security Systems In The Cloud
Download
The Power Of Integration In Physical Security Systems
Download
Preventing Loss, Securing Assets
Download
Using Artificial Intelligence (AI) To Automate Physical Security Systems
Download
Integrating IT & Physical Security Teams
Download
Verkada Workplace Safety Survey
Download
How To Create A Successful Physical Security Roadmap
Download
5 Easy Steps To An Upgraded Video Surveillance System
Download
Improving City Mobility Using Connected Video Technology
Download
5 Ways To Strengthen Physical Security With An Integrated System
Download