Mercury Security, part of HID Global - Experts & Thought Leaders

Latest Mercury Security, part of HID Global news & announcements

Mercury Security, a pioneer in open architecture access control hardware and a HID brand, announces its Mercury S4 I/O Module family. The new generation of intelligent modules is designed to help organizations modernise and expand physical access control infrastructure, building on the infrastructure they already have in place. As organizations expand facilities, adopt cloud and mobile technologies, and respond to evolving cybersecurity requirements, many are also looking for ways to modernise aging access control infrastructure without the cost and disruption of repeated hardware replacements. Mercury S4 I/O Modules extend the company's trusted intelligent controller architecture with a secure, modular platform that enables organizations to expand systems more efficiently, keep systems running and prepare for future technology requirements. Future technology requirements "Security infrastructure is expected to last for years, even as technology continues to evolve," said Steve Lucas, Vice President of Sales at Mercury Security. “We designed the S4 platform so customers can continue to expand and adapt their systems over time and protect the investments they have already made. These modules represent the next evolution in the Mercury access control ecosystem, offering a stronger cybersecurity posture, improved system performance and the introduction of a high-density option that reduces the overall system footprint." As IT closets and equipment rooms continue to shrink, system integrators face growing pressure to do more with less physical space. The Mercury S4 platform directly addresses this challenge. The new MR54-S4 Reader Interface Module delivers four-door capability in the same space previously occupied by a two-door interface module, effectively doubling door capacity within the same footprint. Each module supports up to 12 inputs and up to 8 readers in a single unit. By increasing door density within an existing footprint, integrators reduce installation complexity through simplified wiring and improved reliability, and organizations expand capacity without adding panels or consuming valuable space. Physical security environments Cybersecurity was a central design consideration throughout development. Mercury S4 I/O Modules incorporate a secure-by-design architecture with hardware-based protections engineered to address evolving cyberthreats and regulatory expectations while providing the resilience required for mission-critical physical security environments. Protections include secure boot, which establishes a hardware root of trust by preventing unauthorized or tampered firmware from running. Building on that foundation, hardware-enforced trust through an EAL6+ Secure Access Module—a top-tier Common Criteria security certification—secures key management, while post-quantum cryptography capability extends that protection to help safeguard deployments against future threats. Critical infrastructure systems This is particularly timely, as the United States and the European Union have both moved to accelerate the shift to post-quantum cryptography, with the White House directing federal agencies in June 2026 to begin their migration and the European Commission publishing a coordinated roadmap directing member states to secure high-risk and critical infrastructure systems by 2030. Most importantly, the platform aligns with recognized industry frameworks including the Center for Internet Security (CIS), the National Institute of Standards and Technology (NIST) and evolving Cyber Resilience Act (CRA) requirements to help reduce risk and support long-term compliance. Wholesale hardware replacement Rather than requiring wholesale hardware replacement as technology evolves, Mercury designed the platform to accommodate future capabilities through modular architecture. For organizations managing hundreds or even thousands of doors, that means fewer panel replacements, less rewiring and fewer technician visits across facilities. Because labor often represents the largest cost of an infrastructure upgrade, reducing those onsite interventions can significantly lower lifecycle costs while allowing security teams to modernise at their own pace. Together, the Mercury S4 I/O Module family provides organizations with a flexible foundation for expanding access control systems while preserving openness, interoperability and investment protection that have long defined Mercury-based deployments. Access control professionals Built on Mercury's open architecture, the S4 family combines stronger cybersecurity and increased processing power, delivering 6x the memory and 8x the storage of prior generations, along with broad interoperability within a modular design that adapts as customer requirements evolve. The platform supports both forward and backward compatibility, allowing security leaders to upgrade their infrastructure incrementally while minimizing disruption to existing deployments. These design priorities closely reflect what Mercury is hearing from the market. Through the company’s ongoing industry research into the needs of access control professionals, clear themes continue to evolve around staying current with evolving cybersecurity and data protection standards and the importance of forward and backward compatibility in future infrastructure planning. These findings underscore the growing demand for access control platforms that balance modernisation with long-term investment protection. The Mercury S4 I/O Modules are available now through Mercury's trusted OEM partner network.

Mercury Security, a pioneer in open architecture access control hardware, announces the commercial launch of its embedded application environment. With developer onboarding active and partner applications in progress, the platform moves from concept to execution, enabling technology partners and OEMs to build and deploy secure applications directly on Mercury MP Intelligent Controllers equipped with the latest Mercury firmware. Embedded application environment Mercury introduced its embedded application environment one year ago to expand what access controllers can do. Today’s announcement marks the platform’s transition from preview to commercial launch. The platform extends Mercury’s open architecture by allowing approved applications to run directly at the edge. By embedding business logic and integrations on the controller itself, organizations can accelerate innovation, strengthen security and scale functionality without reengineering their core infrastructure. Structured developer program Supported by a structured developer program, technology partners follow a four-step onboarding process that includes submitting proposals, collaborating with Mercury on technical evaluation, accessing development tools and completing a security review prior to distribution. This framework ensures applications meet performance and cybersecurity expectations while helping partners bring solutions to market faster. The launch highlights the growing community of OEMs and developers building on Mercury’s platform. By providing a secure, open environment at the controller, Mercury empowers partners to create new capabilities that operate directly at the edge. Delivering additional value Innovation is no longer confined to upstream systems. Applications can now enhance integration, analytics and orchestration within the controller itself. This ecosystem approach allows partners to differentiate their offerings, while delivering additional value for end users. “This is a milestone moment,” said Steve Lucas, Vice President of Sales at Mercury Security. “We’ve laid the groundwork with a secure, open controller platform and validated distribution through OEM channels. We’ve created an environment where partners and developers can build apps on MP Controllers. Now, we have the program and tools to support a growing list of certified app developers.” Partner application highlights Mercury is working with three new partners to demonstrate the range of innovation possible within the app environment: Commend Edge Bridge: The Commend Edge Bridge app will deliver real-time, hardware-level data directly and securely to Commend device displays and audio products, without requiring any middleware. HiveWatch: The HiveWatch app on Mercury controllers will securely connect access control hardware to HiveWatch’s cloud security operations platform. Security teams will gain centralized visibility into physical security events, with the ability to isolate device health events at the panel level, enabling faster diagnostics, proactive maintenance, and more efficient incident response. KeyShare Connect by PassiveBolt: The KeyShare Connect app will enable government-issued digital IDs — such as mobile driver’s licenses — to be verified for physical access within a Mercury-powered environment, running natively on the Mercury controller at the edge. Together, PassiveBolt and Mercury will help eliminate the need to issue, manage, or pay for separate access credentials. These partner applications will join the Mercury KS210 device app, which enables OEMs to integrate up to 32 KS210 OSDP server cabinet locks per controller. Embedded application environment Security and governance are foundational to the embedded application environment. Applications undergo structured testing to ensure performance integrity and alignment with enterprise cybersecurity expectations. Controllers designed on open standards allow partners to integrate more efficiently while giving end users flexibility to adapt over time. As regulatory requirements evolve and integration needs expand, the Mercury app environment supports phased modernisation rather than wholesale replacement. Attendees can experience the embedded application environment in action at ISC West, Booth 8053. Demonstrations will showcase how applications run directly on Mercury controllers and how the developer program supports structured innovation across the ecosystem. With the app environment now commercially available, Mercury reinforces its commitment to providing the secure, open foundation that powers modern access control and enables what’s next.
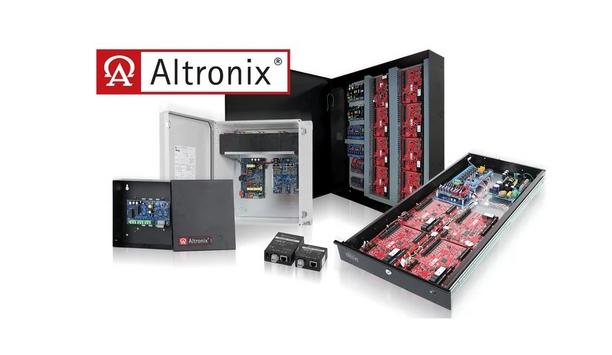
Altronix, the globally recognized company in power and networking solutions, is showcasing its latest innovations that elevate security and system performance at GSX 2025 in Booth #2155. Making its debut is the new eFlow Pro Series auto-ranging power supply/charger with enhanced features providing greater versatility for myriad access control and security applications. Altronix’s latest innovations at GSX 2025 Altronix is also showcasing new Access & Power integration products, Networking solutions for single pair ethernet Altronix is also showcasing new Access & Power integration products, Networking solutions for single pair ethernet, Fiber, and PoE with LINQ™ network power management upgrades. “We are continually expanding the Altronix product portfolio to provide security professionals with greater versatility, efficiencies and reliability,” said Alan Forman, President of Altronix. He adds, “The introduction of our eFlow Pro Series, along with myriad access and network power integration upgrades demonstrate our commitment to innovation.” Featured solutions on display from Altronix include: The new eFlow15UB - Universal Power Supply/Charger with auto-ranging input 90VAC to 256VAC input allows for selectable 12VDC at 14A and 24VDC at 10A outputs, providing system installers globally with greater flexibility and convenience. Its enhanced features include: a removeable AC input terminal block, Lithium or SLA battery charging, fire alarm disconnect, short circuit and overload protection and more. eFlow15UB also allows for LINQ network technology for remote monitoring, power management, and diagnostics via LINQ2 Module. Altronix LINQ™ network communications now integrates with Milestone XProtect VMS to receive device events, including connectivity status, value threshold breaches, as well as service and battery notifications directly in the XProtect Smart Client. The integration provides a ‘single-pane-of-glass’ to monitor the health and status of Altronix devices and any equipment it powers to best sustain uptime of mission critical systems. NetWay Spectrum with integrated EBC48 rapid battery charger delivers up to 90W per port and recharges 32AH batteries in under eight hours. These hardened PoE switches utilize fiber for remote deployments and provide extended backup to keep systems operating where only intermittent power is available. New 277VAC input options support a variety of applications at the edge. Pace™ Long-Range Ethernet Solutions extend Ethernet connectivity up to 1000m over a single pair or up to 500 meters over structured cabling, enabling the deployment of IP devices at longer distances. Pace also supports T1L industrial devices like sensors and controllers for a wide range of industrial/building automation applications utilising existing single pair infrastructure. Trove™ Access and Power Integration Solutions are available in pre-wired and pre-configured kits that support over 50 major access control brands, including AMAG, AXIS, Brivo, Galaxy, PDK, Software House, and all Mercury platform controllers, such as Avigilon, Genetec, LenelS2 and more! Trove is available in outdoor, scalable wall or rack-mount configurations, simplifying installation and maintenance with a single point of service. Circ™ Redundant Power Solutions support seamless transition between two independent 115VAC or 230VAC inputs, ensuring uptime during power outages and failures to maintain critical security operations. Tempo724Q Programmable Timer is a dual-channel 24/7 network timer ideal for applications, including access control, lighting, automation, and more. Features include dual form “C” relay contacts, advanced LINQ technology for remote diagnostics and scheduling, and reliable synchronization across systems. Altronix’s advanced A&E portal and specification program Altronix is also launching an advanced A&E (Architects & Engineers) portal and specification program, designed to provide direct support to the A&E community. This includes streamlined access to Trove power specifications and other tailored resources. Altronix power and data transmission products are backed by a lifetime warranty.
Insights & Opinions from thought leaders at Mercury Security, part of HID Global
You’re no psychic. You probably don’t have the power of clairvoyance. But guess what? When it comes to your security, none of that matters. You can still create future-proof security by properly equipping yourself. Here’s how. Understanding access control Security is changing faster than ever before. With new threats inside the workplace and smaller security teams taking on more tasks, IT and security personnel must automate their processes using new technology. One difficult aspect, however, is choosing the right technology. By analyzing technological trends and assessing your current and future needs, you can preemptively find solutions. Ultimately, in the long run, these solutions will save you time and expense. Ultimately, in the long run, these solutions will save you time and expense But how do you distinguish a momentary trend from a long-term solution? Do you really need to pay extra money for that feature, or will you stop using it in a year? To properly invest in future-proof access control, IT and security teams must look at three different aspects of technology: Flexibility, Scalability, and Efficiency. Access control system Flexibility: Hardware It’s not the sexiest thing to talk about, but hardware is crucial to any security system. Readers, locks and controllers are the backbone of any access control system, and choosing the right hardware is essential when it comes to planning for the future. Broadly speaking, hardware falls into two categories: proprietary and non-proprietary. For those teams considering a new installation, choosing between proprietary access control and non-proprietary access control is a decision that will affect your organization over the long term. Long-Term unseen expenses Proprietary Hardware Pros: Upfront costs can be less expensive; One vendor for hardware and software. Cons: Locked into one vendor; Long-term unseen expenses. Imagine buying a microwave that only cooked foods produced by the microwave manufacturer Imagine buying a microwave that only cooked foods produced by the microwave manufacturer. In a booming economy, the manufacturer produces all sorts of tasty treats—popcorn, lasagna, pies. But when the economy takes a dip, the manufacturer scales back its production and announces it will only sell liver and onions. Now maybe you’re a liver and onions fan, but on the off chance you like variety in your diet, this would be a problem. Your microwave has been rendered useless and has essentially become a liver and onions cooking machine. Potential system vulnerabilities Like the microwave example, proprietary hardware leaves companies at the mercy of the manufacturer. If the manufacturer goes out of business, the system will cease to function, and customer support will be non-existent. Consequently, your security team will likely have to install an entirely new hardware system. Costly, right? Let’s consider a less dramatic scenario. What if a manufacturer, instead of closing, decides to scale back its operations? It provides less frequent updates and fewer new feature releases. Without these updates, your security becomes more vulnerable and outdated. In the long run, choosing proprietary hardware can end up costing teams a lot more than they are saving and expose potential system vulnerabilities. Non-Proprietary hardware Pros: Free to switch software vendors; Long-term system flexibility. Cons: Upfront costs can be more expensive. Non-proprietary hardware gives teams the power to switch software providers at any point Where proprietary hardware fails, non-proprietary thrives. The most important aspect of a non-proprietary system is the flexibility it grants. Non-proprietary hardware gives teams the power to switch software providers at any point, without replacing the hardware. In the aforementioned microwave scenario, the customer was relegated to a life of liver and onions because of their proprietary microwave. However, had they chosen a non-proprietary microwave, then they could have eaten any meal. They wouldn’t be limited to the food options sold by the manufacturer. Non-proprietary hardware also accounts for much of the current marketplace. If your team currently uses non-proprietary hardware—Mercury Security, HID, Wavelynx, or STid-- but is considering switching to a cloud-based provider, then something called a software takeover could be useful. A software takeover is a process by which a new software provider replaces a former one, though no new hardware is installed. Scalability: on-Prem or the cloud? Whether working for an enterprise, hospital or school district there is always potential for expansion. As an organization grows or shrinks, so must its access control. At your latest ‘all-hands’ meeting, the CEO announces that you will be aggressively expanding At your latest ‘all-hands’ meeting, the CEO announces that you will be aggressively expanding. They want security to be up and running in three new countries by the end of the quarter. Luckily, you have just finished migrating from on-premises access control to the cloud. You handle scaling the operation with relative ease. IT and security teams must choose between cloud access control and legacy on-premises equipment. The greatest determination of scalability lies with the server. Cloud-Based access control Pros: Easily scalable; Less regular maintenance; More secure; Integrations; Centralised storage. Cons: On-going subscription costs; Migrating from on-premises access control. When asked about the trends shaping the near future of access control, 38% of respondents said cloud hosting would be an important feature. Though this was a lower percentage compared to the responses at the beginning of Covid-19 (50% mentioned cloud), cloud security is poised to grow by as much as 13.7% each year. connecting software stacks Here are some facts about cloud-based access control: Security: In the past, what held the cloud back were concerns about cyber security. But advances in security, including 256-bit encryption for data at rest and data in transit, have significantly improved the cloud. Integrations: Talk to any IT director who has already made the migration from on-prem to cloud, and they’ll mention ‘integrations.’ The cloud gives administrators the ability to more quickly connect their software stacks. Some popular integrations include visitor, video, identity, and notification management. Though integrating on-premises access control is possible, it takes significantly longer and is more costly than integrating with the cloud. Remote Access: Since COVID-19, IT and security professionals have been searching for remote ways to work. However, remotely connecting to an on-premises access control system often requires a VPN. The cloud allows teams to work remotely and access any of the buildings in their portfolio while off site. Physical access control Efficiency: Software Features Another important aspect of physical access control is its software features Another important aspect of physical access control is its software features. While the needs vary from industry to industry, some overlap exists. For instance, a global dashboard can give oversight across buildings on college campuses or offices of a national enterprise. A security team in New York can monitor the access events or provision a new employee in Tokyo. Broadly speaking, IT and security teams are looking for software that boosts day-to-day efficiency and is customizable. These features include: Custom Reports- Spreadsheets or PDFs that give you an aggregated view of access events that have occurred over a given period. Custom Roles- Administrators the ability to create an organizational framework by access permissions. Badges- Create branded physical or digital badges according to permission level. Emergency Add-ons- Custom door plans and Muster reporting can help in crisis situations. For example, if there is an active shooter, certain doors can be left open or locked automatically to prevent the shooter from gaining access to certain areas. Cloud access control has made it easier to implement new features. Ultimately, the cloud gives IT and security administrators more power to quickly request and deploy the features they find most worthwhile. Final thoughts on security With the rapid technological transformation brought about by cloud and mobile access control, it’s important that IT and security teams stay ahead of the curve. In order to decide which system is the right choice for you, it’s important to evaluate not only your current but also future needs. Creating a checklist of the most important features and deciding whether to host all the server yourself are two important steps to pinpointing the perfect access control system. For more information, ask access control providers for a free demo.
Open Options, based in Addison, Texas, provides a truly open access control architecture that will strengthen the ACRE portfolio and increase the breadth of solutions offered by the global provider of security systems. The acquisition of Open Options is also an opportunity for ACRE to focus on growth opportunities in North America and “balance the scales a bit,” says Joe Grillo, CEO of ACRE, which significantly grew its reach in Europe, the Middle East and Africa with the acquisition of Siemens Security Products in 2015. “Open Options is also a company that's growing, is profitable and fits seamlessly into our vision for the access control space in which we operate,” says Grillo. Independent Operations The strength of Open Options in the Southwest provides significant additional coverage for ACRE in that region of the United States The Open Options brand will continue to operate independently under the ACRE umbrella. Open Options CEO and Founder Steve Fisher will continue in his role as leader of the company, says Grillo. “There is a strong and competent management team in place that will continue to provide leadership going forward.” Open Options’ open-architecture access control solutions will add value to the solutions ACRE already offers under the Vanderbilt brand. In a market that has traditionally been proprietary, the open-platform solution offered by Open Options helps deliver more opportunity to offer customers a full-scale solution based on their needs, says Grillo. In addition, due to its origin as a Texas-based company, the strength of Open Options in the Southwest provides significant additional coverage for ACRE in that region of the United States. Technical And Financial Resources On the other hand, ACRE provides a greater level of technical and financial resources that Open Options can utilize to help them grow even faster. These resources were not as available to the company if it remained independent, Grillo notes. ACRE’s divestiture of Mercury Security in 2017 facilitated this investment. As discussions began earlier this year, ACRE realized the potential of adding to its access control portfolio in the North American market, says Grillo. Open Options and Mercury have been "partners" for 20 years; Mercury provides hardware panels for Open Options systems. Each company will manage and make decisions about their reseller channels independently “The Mercury brand continues to be a strong one, so we're interested in continuing to nurture that relationship, and in fact we have become a larger and stronger partner to Mercury as ACRE,” says Grillo. “After owning Mercury for a number of years, we had the understanding of the company, the product portfolio and the partner relationships that defined it, so we were confident that the deal would be a positive one for the ACRE brand.” Meeting Customer Needs “Open Options and Vanderbilt share some customers already and we can leverage that by gaining more share of their business while providing them with a portfolio that will meet a broader set of customer needs,” says Grillo. “Where possible, we can look for synergies in channel partners that are not currently shared to provide access to both brands. This will be a benefit to Open Options, Vanderbilt and our customer base. However, importantly, each company will manage and make decisions about their reseller channels independently.” Are there more acquisitions on the horizon for ACRE? “We're always looking for opportunities that fit into the nature of our business,” says Grillo. “Companies that have growth potential and share similar go-to-market strategies and visions for the future are of particular interest to ACRE. "We're still operating in a highly fragmented market, so we're going to see continued consolidation in both access control and beyond, which means ACRE will be looking for the right opportunities to follow along that path.”
One of the biggest recent security divestitures in the news was the sale of Mercury Security to HID Global, which occurred around a year ago. The seller in that transaction was ACRE (Access Control Related Enterprises), also the parent company of Vanderbilt and ComNet. We recently spoke to founder and CEO Joe Grillo, a 30-year industry veteran, about the mergers and acquisitions (M&A) market, ACRE’s future, and new opportunities opened up by the Mercury sale. Q: What’s new with ACRE? Grillo: We have an opportunity to have organic growth and to have some scale on a global basis to be a decent size player" ACRE is a company I founded in 2012, and since then we have had six acquisitions and one divestiture. We’ll never focus on ACRE as a brand, but we currently have more visibility of ACRE as a parent company with our two strong brands, ComNet and Vanderbilt. Last year was a very busy year [with the sale of Mercury Security to HID Global] because it takes as long to sell a brand as to buy one, maybe more so. Q: What’s next? Grillo: What you are seeing from us this year is that we are again in a buying mode. No announcement yet, but we expect one by the end of the year. We are well-funded, have great partners, and see an opportunity to continue to grow acquisitively as our highly fragmented space of access control continues to consolidate. From the standpoint of ACRE, with the ComNet and Vanderbilt brands, we are also doing more integration on the backside – not what the customer sees. We will continue to grow toward a $200 million business. We were there when we owned Mercury, and we will get there again. We have an opportunity to have organic growth and to have some scale on a global basis to be a decent size player. Because ACRE are owned by a private equity company, we are brought into every opportunity: ComNet is a good example" Q: Do you see the M&A market being more competitive – more companies looking to acquire? Grillo: There’s a lot of money chasing not-so-many deals, so evaluations can get expanded. But as interest rates creep up, it is definitely a challenge to find the right valuation, the right financing and the right strategic fit. It is a very strategic market. Q: There have been some big acquisitions lately. Were you guys involved at all in evaluating those opportunities? Grillo: Because we are owned by a private equity company, we are brought into every opportunity. An example of that was ComNet. I would not have been aware that the founder passed away two years ago and that there was this opportunity to own the business. So we look at everything; anything that’s out there we look at. The biggest recent announcement in our world was S2 (being sold to UTC/Lenel), and, yeah, we looked at that. It didn’t fit our profile – it was too expensive. Great business, and it’ll be interesting to see how it fits into the UTC environment. There was also Isonas [which was recently sold to Allegion], but the size didn’t add enough scale, but I like the technology. ComNet sells communication networking solutions and products, which is more attractive than video systems for ACRE Q: So what are you looking for in an acquisition? Grillo: It’s hard for us to find something that moves the needle, and you have to find that right balance. Is it something we can digest and have the financing for, and also is there room on the back end? We are private equity-owned, so we know there will be an exit for our investors, too. So we have to find the right balance, good valuations, the right size and digestible. If you look at our acquisitions, we have done two “carve outs.” The Vanderbilt name didn’t exist until we bought the business from Ingersoll Rand, and then we bought the [intruder] business from Siemens. That’s how Vanderbilt came about. You get a lot of value when you carve out a business, but there’s a lot of work. In the case of Mercury or Access Control Technology (ACT) that we acquired; they were growing and profitable but they stretch your finances a lot more. So you have to find the right mix in there. Q: Does video interest ACRE at all? Grillo: We have to find the right balance, good valuations, the right size and digestible"ComNet is our video play. ComNet sells communication networking solutions and products, and 70 to 80 percent of that is used for video systems. But unlike cameras, which don’t interest us, it’s actually good margins, highly specialized repeat business and with good channel partners. So where are we going to play? Cameras – no (because of commoditization). We have some recorder technology (from the Siemens acquisition) and we have the communication networking technology (with ComNet). On the software side, we have looked at a lot of the VMS companies, and a lot of them have been on the market. But the valuation expectations can be high because they are software companies. And we really believe in partnering as a good thing, too. If we integrate to Milestone or Salient or some of these companies, we will never lose an access control client because they chose a particular VMS. Q: ACRE is also looking to grow organically, isn’t it? Grillo: From a technology perspective, we are a product company and we are continuing to bring new products to the market with the ComNet communication networking business and the access control business. And in Europe, we have a third leg of the stool, which is the very successful intrusion and burgular alarm business we acquired from Siemens (SPC products now sold under the Vanderbilt brand). That business continues to do well and is now one of the highest performing segments in our portfolio.The intrusion and burgular alarm continues to do well and is now one of the highest performing segments in our portfolio" Q: But you don’t have to own a company to make it part of your solution. Grillo: An important word is integration. We have to integrate to all the wireless locks. We have to integrate to the VMS systems. But we don’t have to own them. Q: How has the Mercury Security divestiture impacted the rest of your business? Grillo: It has opened up the opportunity for us to look at Mercury partners as possible acquisition targets without worrying about conflicts with the very good business of Mercury. We have more flexibility now compared to the Mercury era. Q: How will the economic cycle impact the security market? Grillo: Interest rates are a much bigger issue than the overall economic cycle. We talk a lot about it with our owners – clearly interest rates are tightening up. If you go out to do acquisitions or to borrow money to do something with your business, it will be tougher than it was two years ago, and it may get worse in the next two years. Security is less impacted by the economic cycle than some industries.

The Key To Unlocking K12 School Safety Grants
Download
Honeywell GARD USB Threat Report 2024
Download
Physical Access Control
Download
The 2024 State Of Physical Access Trend Report
Download
The Security Challenges Of Data Centers
Download
Mercury Security MR62e IP-enabled Interface Module
Mercury Security LP1501 PoE+ Edge-capable Intelligent Controller
Mercury Security LP1502 Intelligent Controller




