Cisco Systems, Inc. - Experts & Thought Leaders





Latest Cisco Systems, Inc. news & announcements
As AI agents take on more of the work inside the enterprise, the biggest barrier to adoption isn’t capability – it's confidence. Customers need to trust that AI is secure, governed, and worth the cost before they let it run at scale. Today, Cisco closes that gap through new Splunk innovations, giving customers the ability to safely and cost-efficiently scale AI wherever their data already lives. This includes an expanded partnership with NVIDIA to bring Splunk AI to on-premises customers. “One of the biggest roadblocks to enterprise AI today is that it’s too hard to deploy,” said Jeetu Patel, President and Chief Product Officer, Cisco. “Customers want to know: Can I trust it to do the job? Can I afford it? And, most importantly, can I secure it? By running Splunk AI on the infrastructure customers already trust, they can move faster to put AI to work in their business with confidence and control.” Self-managed Splunk AI, accelerated by NVIDIA For customers who can’t move sensitive data to the cloud, Splunk AI has remained out of reach – until now. Cisco and NVIDIA are expanding their partnership to bring self-managed AI directly to Splunk Enterprise customers, across their own on-premises, private cloud, and air-gapped environments. Cisco Secure AI Factory with NVIDIA is the reference architecture that brings the full AI stack together, built from Cisco AI PODs. The newest of these configurations, Cisco AI POD for Splunk, brings Splunk AI to on-premises customers with new AI runtime software, Cisco infrastructure, NVIDIA accelerated computing, and Kubernetes-based architecture – pre-validated and optimized for Splunk AI workloads. Cisco AI POD for Splunk is available today. For customers who have their own infrastructure, partners like bitsIO, Wipro, and World Wide Technology are ready on day one to help customers stand it up. Splunk AI Assistant (available now) and Agent Launchpad (coming later this year) run on this layer. Together, they bring ad-hoc agentic investigations and custom agent building for a broad variety of use cases including the agentic SOC to teams that run Splunk in their own data centers. Customers can also self-host a selection of open and proprietary generative AI models for their Splunk Enterprise workloads, including the Cisco Deep Time Series Model, Google Gemma 4, and OpenAI GPT-OSS 20B, with NVIDIA Nemotron open models in the coming months. Teams can use the model best suited for the job without sending data outside their environment. “Enterprises need to bring AI where their data lives, especially when security and sovereignty requirements require critical workloads to stay on-premises,” said Justin Boitano, Vice President of Enterprise AI at NVIDIA. “By enabling Splunk AI workloads to run with NVIDIA Nemotron open models on NVIDIA accelerated computing, Cisco and NVIDIA are working together to bring AI agents directly to Splunk and giving organizations a high-performance, full-stack foundation for agentic security operations wherever they run their infrastructure.” Observe agent performance and track token spend in one view New observability innovations give Cisco customers one full-stack view into how their AI agents are actually performing. AI agents behave in ways that the people running them can’t always predict, running up costs that stay invisible until the invoice lands. Splunk Agent Observability, with its new Tokenomics capabilities, is closing that visibility gap and giving organizations a real-time view into agent performance and AI token spend. This enables teams to see exactly where and why AI costs accumulate before they become a budget problem. Splunk Agent Observability, announced initially as an on-premises offering, is now available in Splunk Observability Cloud and in Cisco Cloud Control, extending visibility to customers working across the Cisco portfolio. It evaluates agent and model behavior, observes performance across the AI stack, and applies runtime guardrails that block inaccurate or unsafe actions, like hallucinations or leaking sensitive data. As part of Splunk Agent Observability, the new Tokenomics solution extends that visibility to spend – tracking and attributing token expenditure across AI agents and employees’ use of coding agents like Claude Code, Codex, and Cursor. It will also forecast consumption patterns to project where spend is headed before a billing period ends, using the Cisco Deep Time Series Model. These insights help organizations to operationalize a tokenomics framework and tie AI spend to business outcomes. Cisco is also helping organizations strengthen their infrastructure resilience by minimizing visibility gaps and cost barriers that hinder autonomous troubleshooting. The Observability Studio enables teams to ensure new applications are “born observable,” measurable and production-ready from the start. The new Network Intelligence App brings Cisco network topology, device health, and events into Splunk, so network teams can trace an alert straight to the device behind it and the network around it. Also, the new editions for Observability Cloud – Essentials and Premier – simplify how customers buy and expand observability across their business, with cost-effective log analytics to debug application and infrastructure problems. Trusted autonomy for the agentic SOC The AI threat landscape is on track to outpace the human-led defense model. Never has it been more critical for organizations to be able to understand and address potential exposure and vulnerabilities across their entire IT landscape – from the infrastructure to the applications. Stopping these AI-era threats requires an agentic SOC capable of reasoning and defending at machine speed, without compromising the data sovereignty and human governance enterprise leaders demand. Splunk is advancing the agentic SOC by combining enterprise-wide telemetry with specialized AI agents powered by leading frontier and domain-specific models. New purpose-built agent capabilities expand the Splunk Agentic SOC Workforce and mirror how elite security operations teams work across detection engineering, proactive threat hunting, autonomous investigation, coordinated response, and policy governance. By correlating rich, full-stack machine data across network, cloud, application, and identity environments, these agents deliver deep reasoning and transparent, explainable verdicts that cut alert noise and accelerate mean time to remediate. Attackers are now using AI to hunt for vulnerabilities at scale, probing infrastructure, applications, and identity systems continuously and indiscriminately. Recent exploitation campaigns have made complete exposure visibility a board-level requirement. New Exposure Analytics enhancements deliver on that with broader asset coverage, historical change tracking, and business-specific risk insights. Connecting exposure context to live security activity across Splunk, Cisco, and an extensive third-party ecosystem, so teams see their entire estate rather than one vendor’s slice of it. Agents use that context to pinpoint what matters most and where risk is active. New capabilities in Splunk Enterprise Security Essentials bring agentic security operations and greater autonomy to far more security teams. Splunk Enterprise Security Premier adds deeper agentic autonomy and the full power of Splunk Enterprise Security. Building the agentic enterprise together: Cisco’s Splunk and AWS The same urgency is driving Splunk’s next chapter with AWS. Splunk and AWS are expanding their long-standing relationship into joint product development through a multi-year agreement. The work advances the agentic SOC to match the speed of AI-driven attacks. Those attacks now move faster than human-led response processes can answer. Matching that speed takes deep security intelligence and the scale to act on it instantly. Splunk brings the data platform and detection depth security teams already run on. AWS brings global cloud scale. Together they will put agentic support in the hands of analysts across detection, investigation, and response. Security teams won’t give up oversight to move faster. What’s ahead is agentic action at scale, with the governance and analyst control enterprises require.
Nutanix, a hybrid cloud pioneer and AI innovator, announces the general availability of Nutanix Enterprise AI (NAI) 2.8, and the upcoming general availability of Nutanix Kubernetes Platform (NKP) 2.19, along with new incentives, programs, and resources designed to help partners accelerate growth on emerging AI opportunities. Many enterprises face a major roadblock when deploying AI: AI is accelerating the shift to containers, while critical applications and data remain spread across both virtualised and containerised environments. This divide can force enterprises to add infrastructure silos, move data or rearchitect existing workloads to support AI alongside the applications and data they already run. Dual-native architecture Nutanix addresses this with a governed, dual-native architecture that runs traditional applications and modern AI side by side, allowing the infrastructure to flexibly support the workload, integrated with silicon partners to provide choice and flexibility to customers. By bringing AI to where enterprise data already lives, Nutanix helps customers reduce silos and accelerate ROI without costly rearchitecting or added networking and data layer complexity. Expanding on NCP capabilities, NAI and NKP are designed to enable organizations to securely run, manage, and govern AI, containerised applications and virtualised workloads through a consistent control plane. These complement the core platform capabilities for near-bare metal performance for AI on virtualised infrastructure introduced with NCI 7.6. Together, they give enterprises a flexible alternative to infrastructure stacks that limit architectural choice, drive up costs, and require disruptive platform changes. Adaptable multitenant cloud foundation For partners, the new Powered by Nutanix: Verified Services program aims to enable them to capitalize on major industry shifts and next-generation AI deployments by empowering them to build validated, high-margin services practices that span the full customer lifecycle. To operationalise these flexible new offerings, Service Provider (SP) Central provides an adaptable multitenant cloud foundation, giving service providers the control they need to grow infrastructure, platform, cloud-native, and AI services on their own terms. “Enterprise AI should not require customers to rebuild the systems that already run their business,” said Thomas Cornely, Executive Vice President, Product Management, Nutanix. “With our dual-native architecture, customers can bring AI to their existing applications and data while running each workload on the infrastructure best suited to it, with consistent operations and governance across VMs, containers and AI. This gives organizations a practical path to production without creating new silos or limiting future choice.” Unified and secure platform NAI delivers a unified and secure platform to deploy, manage, and scale AI workloads across hybrid environments. It enables enterprises to enforce governance over their agents and models, gain total visibility over token usage, and streamline AI development with a simple interface with built-in observability metrics and easy to use model-as-a-service while ensuring security, scalability, and integration with existing infrastructure. Key NAI updates include: Agent Gateway: This now includes a generally available MCP Gateway which serves as a secure, unified front door for AI agents to access tools and data without custom engineering. To complement this, Nutanix has also released MCP Server for NCP to help customers build agentic AI applications with secure access to the infrastructure managed by Nutanix. Private Inference: New advanced inference and fine tuning capabilities enable scalable, multiGPU inference for LLMs via tensor parallelism, delivering high-throughput serving and low-latency response times for enterprise LLM workloads. In addition, this enables batch inference and speculative decoding. Key features include: 1) Parameter-Efficient Fine-Tuning which supports Low-Rank Adaptation (LoRA) fine-tuning for smaller models (<8B parameters), helping organizations to cost-effectively customize open LLMs on private domain data using single-GPU compute while seamlessly deploying adapters straight to serving pipelines; 2) Scalable multiGPU serving which enables high-throughput multiGPU inference via tensor parallelism, delivering fast, distributed serving across enterprise hybrid cloud environments; and 3) Speculative decoding which accelerates LLM inference token generation by up to 2.5x using lightweight draft models, cutting output latency without sacrificing model accuracy. Enhanced Security against Rogue AI: With the rise of agentic AI and the risk of models breaking out of sandboxes, security is paramount. NAI provides robust protection against rogue models through our platform and APIs, featuring fine-grained Identity and Access Management (IAM), custom roles and seamless model sharing. This enforces least-privilege security, helping ensure agents operate securely and restricting access to only authorized roles, as well as support for air-gapped NVIDIA NIM deployment. Running agentic applications With NKP, organizations can simplify container operations across containers running on bare metal and VMs without piecing together complex, custom stacks. The upcoming release will provide an AI-optimized platform for building and running agentic applications at scale, including the following features coming soon: NKP Metal: Built to bring HCI-grade simplicity to bare-metal Kubernetes, with automated OS, firmware, and container deployment, and persistent, enterprise-grade storage natively, eliminating the complexity of patchwork platforms. NKP Full Stack: While NKP Metal is intended to bring simplicity to bare-metal deployments, NKP on AHV remains the cornerstone for organizations requiring robust, agile virtualised environments. Combined with Nutanix Flow, NKP on AHV is designed to deliver stronger network-level sandboxing for AI agents, helping provide essential isolation to mitigate the risk of rogue attacks and lateral movement. AI Applications Catalog: Offers a one-click deployment path for curated, validated AI/ML software (Kubeflow, Milvus, Slurm) to help bypass manual integration challenges. Hardware and Compliance: Planned expansion of ecosystem support with validated GPU integrations, alongside dynamic resource allocation for modern AI workloads. CNCF Certified Kubernetes AI Conformant Platform: NKP has attained formal CNCF certification to validate that NKP provides the standardized APIs and capabilities required to reliably operate enterprise AI workloads. Maximising GPU utilization Demanding AI workloads require infrastructure that keeps data moving, maximises GPU utilization, and reduces deployment risk. Nutanix Unified Storage (NUS) recently achieved NVIDIA-Certified Storage validation at the enterprise level, providing a trusted, interoperable foundation that helps eliminate data bottlenecks. NUS establishes a low-latency, high-throughput data path directly to GPUs, maximising GPU utilization and ensuring linear scalability for large-scale production AI workloads. According to Gartner®, “By 2029, 55 percent of enterprises will migrate 100 percent of workloads from VMware to alternative infrastructure delivery solutions”. To help partners capitalize on this market shift, next-generation AI deployments and other emerging opportunities, Nutanix recently launched the Powered by Nutanix: Verified Services program. This program provides the framework to support the broader partner ecosystem in transitioning from traditional, one-time deals to high-margin, recurring revenue streams by building validated services practices. Backed by streamlined onboarding, comprehensive service delivery kits, and exclusive badging across hybrid cloud infrastructure, Kubernetes, and VM migration, the program equips partners to own the full customer lifecycle, drive faster time-to-value, and maximize long-term retention. Broad portfolio of infrastructure Nutanix is also announcing the general availability of SP Central, a unified multitenant control plane that gives displaced VMware service provider partners greater choice in how they build and monetise services. Service Provider Central gives providers one consistent foundation to build and monetise a broad portfolio of infrastructure, application, cloud-native, and AI services, with the flexibility on deployment location and licensing they need. This is designed to help providers improve utilization and protect margins while giving customers more choice in how and where they run applications and AI workloads. “The Nutanix Cloud Platform gives us a dual-native architecture that is governed and brings AI to our applications and data across virtual machines and containers. This helps speed AI innovation across the production environments our organization depends on,” said Jasim Abdul Rahman, Group Chief Information Officer, Power International Holding. Prioritising platform consistency Industry Analyst Commentary - “By introducing a “dual native” model that unifies services such as networking, security, and data protection across both VMs and containers, Nutanix is leaning into a competitive landscape where consistent policy enforcement and lifecycle management are becoming key differentiators. Enterprises are increasingly prioritising platform consistency as application portfolios span legacy, refactored, and cloud-native designs,” said Matt Flug, IDC. Ecosystem Partners Commentary - “As enterprises deploy agentic AI to automate complex workflows, they need infrastructure that delivers the performance, security and control required for production environments. Cisco is bringing that foundation. Together with Nutanix’s governed, dual-native cloud operating model, we’re giving organizations greater choice in how they deploy and operate AI while maintaining the control they need across their environment,” said Jeremy Foster, Cisco GM & SVP, Cisco Compute. Highly regulated industries "At Continent 8 Technologies, we've worked closely alongside Nutanix to help shape the next generation of cloud services for regulated industries. Our continued collaboration with Nutanix, including the development of Service Provider Central, is built around helping our customers adopt modern cloud and AI capabilities without adding unnecessary complexity. Together, we're enabling organizations in highly regulated industries to innovate faster and focus on their core business, while maintaining the security, compliance, and operational control they require,” said Edward O’Connor, Chief Technology Officer at Continent 8 Technologies. “The rise of agentic AI is redefining how AI services are delivered, making security and sovereignty foundational requirements. Through our collaboration with Nutanix, we are enabling enterprises and service providers to build high-performance, multitenant AI platforms with hardware-enforced isolation and security. This ensures that sensitive data and models remain protected in use, delivering the secure scale and efficiency required for next-generation AI factories,” said Bill Pearson, VP, Data Center Software, Intel. NAI 2.8 and SP Central are generally available now. NKP 2.19 will be available soon.

Across the enterprise, the “office” is no longer a fixed location—it’s wherever an employee happens to be. For chief information security officers (CISOs) and chief technology officers (CTOs), this creates a growing challenge: how to secure mobile access without compromising user experience or adding complexity for IT teams. Samsung and Cisco are addressing this challenge with the next advancement in Zero Trust Access for Samsung Galaxy mobile devices. By bringing more intelligent, unified protection to the mobile experience, this collaboration helps organizations support secure access across more of how employees work today. Broader corporate network Read on to learn how Samsung and Cisco are helping organizations protect mobile productivity while keeping deployment and policy management simpler across the enterprise. The Cisco Zero Trust Access (ZTA) client for Samsung Knox already helps organizations secure access to private applications. Through Secure Private Access (SPA), employees can connect to the internal tools they need without exposing the broader corporate network. Organizations can also enforce app/destination-specific policies on managed devices. This strategy helps ensure that access to corporate resources is secure, seamless, and based on Zero Trust principles. Secure access policies But modern work now extends beyond private applications. Employees browse the open web, use software-as-a-service (SaaS) applications, and interact with generative AI (genAI) tools throughout the day. These workflows create more traffic types for IT and security teams to manage. To support this shift, Samsung and Cisco have introduced policy-based routing (PBR) as the underlying engine of the Cisco ZTA client for Samsung Knox. PBR allows the client to distinguish between different types of traffic and dynamically steer traffic from endpoint devices based on Cisco Secure Access policies and resource categorisation at runtime. Zero trust security policy Depending on the destination and zero trust security policy, the client can decide whether to: Proxy access to the resource through the Cisco Secure Access gateway Block access to the resource Allow access through the default network path Together, the existing SPA framework and PBR enable Samsung and Cisco to extend Zero Trust Access beyond private applications and across more of the mobile work experience. Mobile work experience With PBR, Samsung and Cisco can extend protection across a wider range of mobile traffic. For Galaxy mobile users, the Cisco ZTA client for Samsung Knox helps support two connected access experiences through the Cisco Secure Access cloud: An illustration outlining the two access experiences supported by the Cisco ZTA client for Samsung Knox: Secure Private Access (SPA) for authenticated access to private applications, and Secure Internet Access for web filtering, malware protection, and visibility into internet activity. More consistent experience A single-client approach helps reduce complexity for users and IT teams alike. With fewer agents to manage, organizations can minimize agent fatigue while supporting a more consistent experience across Galaxy mobile devices. By bringing intelligent cloud-based security together with hardware-backed protection from Samsung Knox, organizations can extend Zero Trust principles across mobile devices without introducing additional tools or friction. Access policy management also becomes simpler for IT teams across mobile traffic and enterprise resources. Public internet traffic As mobile work continues to expand across private applications and public internet traffic, organizations need security that keeps pace without adding complexity. With Samsung Knox and Cisco Secure Access, IT teams can support a more secure, consistent experience across Galaxy mobile devices. For IT admins, this means simpler deployment and more unified policy management. For end users, it means secure access that works quietly in the background, helping them stay productive without unnecessary friction. Together, Samsung and Cisco help organizations put Zero Trust into practice across everyday workflows—protecting users, devices, and access wherever work happens.
Insights & Opinions from thought leaders at Cisco Systems, Inc.
In the UK there is a new data reform act working its way through the legislative process. As the law changes, the market changes – so this year will see many companies trying to read the tea leaves and adapt their offerings to take advantage of the emerging changes. The security marketplace is, apparently, constrained by the need for great privacy – it appears to be a zero-sum game – you can have privacy, or you can have security, you can’t have both. In the second half of the year, it is likely that more firms will require services which enable the use of video analytics to extract operational value from visual data, while using AI-powered tools to protect privacy as standard. Privacy-Enhancing technologies One of the areas where there is a huge interest is among retailers, who use video cameras not only to reduce shrinkage and protect employees, but also for video analytics (to understand customer behavior). Several other industries such as transport, retail, and healthcare have also had an increased rollout One area which is extremely interesting and very poorly understood is the extent to which these videos troves are protected under GDPR. The short answer is they are protected, and the second half of 2022 will see more retailers adopting privacy-enhancing technologies to allow them to open up their security footage to help optimize operations and marketing. There will undoubtedly be a rise in live video capture for safety and accountability. Seven US states now mandate body-worn cameras for police officers, and they are also common practice with UK police. Several other industries such as transport, retail, and healthcare have also had an increased rollout. CCTV camera operators In parallel, both public and private organizations are turning more towards video analytics, as they can be useful in many different contexts; they can help in saving time for CCTV camera operators, help efficiency in monitoring places for crime, and can be integrated into other systems – i.e., counting footfall at different locations – as well as use for smart parking, automatic license plate recognition, and facial recognition. 2022 will bring further growth in consumers investing in personal video surveillance for their homes. With the pandemic having forced many to stay at home, home security has become more of a priority. Ring, which produces doorbell cameras, is increasingly popular: they are now the largest corporate-owned civilian-installed surveillance network in the U.S. Personal security cameras Countries like China have already incorporated heavy use of facial recognition technology Interestingly, some of the first GDPR cases and fines have arisen surrounding these cameras, with questions surrounding lawfully processing data and invasion of privacy. As a result, we could see more of a legal requirement for individuals to process footage from their personal security cameras in compliance with GDPR. While the privacy and human rights issues surrounding facial recognition remain heavily discussed, its use will become a lot more ubiquitous – but with concurrent pushes for regulation. Countries like China have already incorporated heavy use of facial recognition technology, and in the West, particularly in smart cities, it is being adopted in different areas; namely, in airports, retail stores, hospitals, and in the workplace, as well as verifying identities online. Trialing facial recognition The police in the UK have also been trialing facial recognition AI for ‘predictive policing’ to tackle crime and use these video analytics for intelligence gathering. In the second half of the year, the EU will reach resolution on its new AI Act that looks to ban facial recognition for a range of sectors. The EU will reach resolution on its new AI Act that looks to ban facial recognition for a range of sectors Companies’ attitudes toward privacy are shifting. Attitudes towards security methods for securing data are changing, with it no longer being a simple check-box exercise, but important for brand reputation and marketing purposes. Investing more money and effort into securing data privacy, as well as weighing out the benefits of data localization, will become more commonplace for businesses when trying to keep customer data secure. Managing personal data Cyber-attack will continue to be one the largest risk for data management, alongside data misuse from employees. Recent statistics from CISCO have shown that over 50% of consumers would switch to companies they believe have better policies around the handling of data. Consumers are wanting greater trust and transparency from the businesses they engage with, leading to companies changing the way that their internal and external practices deal with and manage personal data. Privacy is no longer about compliance and more to do with business reputation and trust – and customers and employees are becoming more cognisant of this. The author of this article is Simon Randall, CEO of Pimloc, the video privacy and security company.
Enterprise security directors often count on an integration firm to handle jobs ranging from day-to-day activities to long-term, technology-laden projects. However, before entering a relationship, you must know what's reasonable to expect from an integrator – as not all are created equal. Here are some tips that might make the selection process easier. Completing comprehensive classwork An integrator's experience working in an enterprise environment is an obvious consideration. Ideally, that experience fits well with your business. Any enterprise experience is a plus, but local, state, and federal regulations create precise yet very different rules for securing a utility instead of a hospital. That's also true for university campuses, manufacturing facilities, and many other operations. Many manufacturers offer certifications awarded after completing comprehensive classwork and testing Look for certifications indicative of an integrator's commitment to staying on top of industry changes. Organizations such as ASIS International and the Security Industry Association offer certifications showing an integrator's team members have mastered security principles and skills. Many manufacturers offer certifications awarded after completing comprehensive classwork and testing. Also, ensure an integrator sells and services equipment that integrates with your current security systems. Using multiple systems for the same function is less efficient. Project update meetings Go beyond an integrator's slick brochures and websites to ask tough questions about previous experience. How would the integrator handle a hypothetical situation in one of your facilities? Ask the integrator if there will be one project manager for all jobs. And ensure that person handles all interactions with security subcontractors. Ask if the integrator provides regularly scheduled project update meetings. It's frustrating to wonder how your project is progressing. Ask if the integrator's team can work during the hours and days that result in the least interference to your daily operations. Ask for onsite system training to save time and eliminate travel costs. Gathering sensitive data Look for an integrator with proven experience working with an enterprise IT department A malfunctioning component may be more than an inconvenience – it may be a severe security threat. You need to know how quickly your integrator can respond when things go wrong. Ask about available service plans. And consider the embedded staff approach in which the integrator places employees on your site full time to handle day-to-day and emergency activities. Much of the security equipment – video, access control, intercoms, visitor management, and more – is wireless and dependent upon networks operated by your IT department. Network-based devices provide more opportunities for hackers to gather sensitive data or cause critical equipment to malfunction. Don't trust your security operations with an Integrator unfamiliar with at least basic cybersecurity principles. Look for an integrator with proven experience working with an enterprise IT department. At a minimum, ensure the integrator can set and change security device IP addresses and port locations. Certifications from providers such as Cisco, Microsoft, and IBM indicate an understanding of various IT technologies. Potential security partners Knowledgeable integrators work with the well-encrypted Open Supervised Data Protocol (OSDP), now an internationally recognized standard. Run from any integrator who suggests operating an access control system with used Wiegand technology offering no encryption between cards and readers. It's easy for hackers to capture data and clone a working credential. Technology moves at a rapid pace. Your modern system of a few years ago may be long-of-tooth. You need an integrator capable of bringing new and innovative ideas to the table. You want an integrator who conducts in-house testing of new products, not relying solely on a manufacturer's claims. You want an integrator capable of thinking outside the box to solve a complex security problem. These ideas are just a start in assessing an integrator's value to your enterprise operation. However, they will help you sort through potential security partners to find one that best meets your needs.
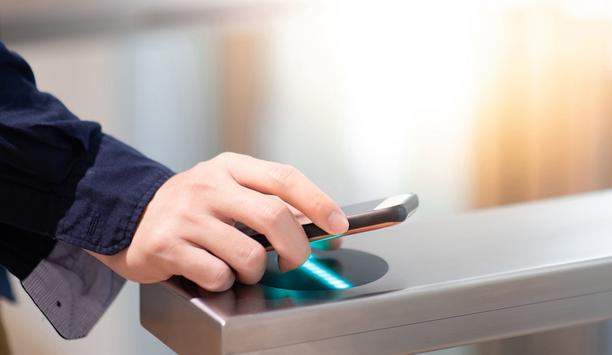
There is a broad appeal to the idea of using a smartphone or wearable device as a credential for physical access control systems. Smartphones already perform a range of tasks that extend beyond making a phone call. Shouldn’t opening the door at a workplace be among them? It’s a simple idea, but there are obstacles for the industry to get there from here. We asked this week’s Expert Panel Roundtable: What are the challenges and benefits of mobile access control solutions?