ASSA ABLOY Opening Solutions - Experts & Thought Leaders










White papers from ASSA ABLOY Opening Solutions

Securing The Modern Data Center
Download
Modernizing Access Control
Download
How Biometrics Are Reshaping Security In A Connected World
Download
The Key To Unlocking K12 School Safety Grants
Download
Access Control System Planning Phase 2
Download
Access Control System Planning Phase 1
Download
Multi-Residential Access Management And Security
Download
Securing Data Centers: Varied Technologies And Exacting Demands
Download
Boost Efficiency And Streamline Security With Integrated Access Control
Download
School Security Checklist
Download
Latest ASSA ABLOY Opening Solutions news & announcements
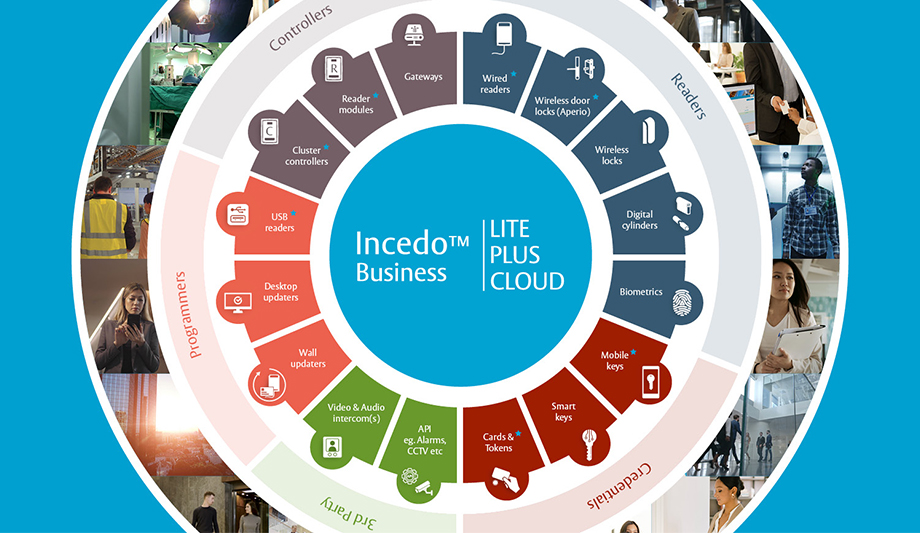
The world is constantly changing, with people, data and goods moving more fluidly than ever before. The security solution needs to move with it. New Incedo Business connects all security software and hardware within one platform. One can easily scale it up or down, based on one’s needs, to keep people moving and business growing. Together. People need different access times and entry points, and the access and security requirements change day to day – so, a static solution is no longer an option. Instead, a single, all-encompassing security platform should deliver connectivity, convenience and simplicity, keeping one’s premises secure and filtering access to manage the ever-changing movement of people. This is where Incedo Business comes in: a new solution for all types of premises, handling security while leaving one free to focus on growing the business. Incedo ensures employees, customers and goods are where they need to be. Incedo makes life and tasks easier and more efficient for everyone, from installers to end users. Facility managers enjoy more control and flexibility than they ever thought possible, maximizing return on investment, with Incedo Business able to scale quickly when needed. System administrators can do more within available budgets: initiating, cancelling or amending access profiles, and monitoring movement around their site in real time. Building users, meanwhile, get the individual access times and entry permissions they need. They can move freely without compromising the security of other people and equipment. Integrators can upgrade connected technologies and systems quickly, minimizing risk and meeting customers’ raised expectations of modern technology. Installers no longer need to wrestle with incompatible systems: easy interoperability is built into Incedo, meaning no more delays or unnecessary complexity. With Incedo’s modular platform approach, one simply chooses the security hardware and credentials one needs and the appropriate management system option. One can set exactly who can access which doors, and when, from the user-friendly Incedo Business software interface. When Incedo Business launches, one can pick the most suitable options from a growing range of Incedo-enabled security and access control hardware. Road-tested, award-winning ASSA ABLOY wireless digital locks and wired ASSA ABLOY wall readers secure all interior and exterior doors. Also already available, a choice of card and token credentials helps users enjoy safe and convenient access to, and movement around, the premises. Incedo mobile keys add the flexibility to open doors with a smartphone. Incedo’s system management options, Lite, Plus and Cloud, scale from entry level up to cloud-based administration. One can manage multiple sites and third-party integrations, including security solutions like CCTV. Scale up and down, add or remove hardware and credentials on demand, or switch system management options, all within a single environment. Migration between Lite, Plus and Cloud options is always seamless in any direction, ensuring total flexibility for the business. Incedo moves with you, today and in the future However your business moves, an Incedo system moves along. Having a flexible platform, able to adapt as the organization changes, reduces total cost of ownership: one never needs to retrain staff or start over from scratch. New Incedo-enabled hardware from ASSA ABLOY and third-party providers will continue to be connected to, and made available within, the evolving Incedo platform. One picks the hardware and software configuration one wants, and can change one’s mind as often as one likes. Incedo guarantees flexibility and scalability in every way, to meet the security needs today and in the future. And because the security and operational challenges at a university, small hotel or hospital are not the same as those faced by a public building or corporate HQ, the Incedo ecosystem will introduce new, advanced user interfaces for the specific industry. “Incedo Business transforms the experience of using and managing a building. It is also the seed from which our revolutionary Incedo ecosystem will grow in the months and years ahead,” says Stephanie Ordan, VP Digital and Access Solutions at ASSA ABLOY Opening Solutions EMEA. “A future where doors are smarter, connectivity and movement are seamless, and access management is genuinely intelligent. This is our vision for Incedo and for those who will be using it.” Incedo™ Business embodies ASSA ABLOY’s vision to create a safer and more open world, keeping everyone on the move. Together. To learn more and download a free solution guide, visit https://campaigns.assaabloyopeningsolutions.eu/Incedo-business

Digitalising access presents a specific challenge in heritage buildings: how to protect these premises against 21st-century threats while preserving the unique building fabric? Choosing a programmable smart key system provided the solution at a historic Prague monastery. The Franciscan Monastery is a living space which, in addition to its spiritual mission, hosts exhibitions, baptisms, and community meetings. Managers must therefore effectively control access to individual parts of the building, to retain an overview of the movement of people, and at the same time react flexibly to events. Streamline key management The original access system could no longer meet their requirements. Key management was complex; there was a lack of clarity; and risks associated with the loss or non-return of site keys increased. They wanted to upgrade access security to streamline key management and minimize risks associated with missing keys. Another essential element was that any software for this enhanced control over key and space management should be user-friendly and operable even by non-technical staff. Above all, preserving the historic character of the building was non-negotiable. No invasive installation process was possible. Leaning into ASSA ABLOY expertise in the heritage sector helped monastery managers to identify the right solution. Combining mechanical robustness Based on these requirements, a CLIQ system was the preferred choice. The ASSA ABLOY eCLIQ smart key solution combines mechanical robustness with intelligent electronics; it enables modern access management without any need for cabling. “Even in historic buildings, our eCLIQ smart key system can be implemented efficiently while preserving safety, aesthetics, and flexibility,” explains Ondřej Gajdoš, Acquisition Sales Manager at ASSA ABLOY Opening Solutions. Thirty-five wire-free cylinders were installed and 90 programmable keys distributed, with everything now managed in intuitive software which allows staff to easily set and edit access rights according to evolving needs – whether for employees and visitors, or to stage one-off events. One CLIQ advantage for the monastery is the ability for staff to respond immediately to any risky situation. If someone loses their key, for example, its authorisations are quickly blocked without any need to replace cylinders – saving time and money while also safeguarding security. Streamlining daily operations The CLIQ solution is also wire-free, so installation took place without interfering with the historic structure. It fully respects the architectural value of the building. By deploying CLIQ, the monastery has gained a modern access management tool that significantly increases security while streamlining daily operations. The solution brought not only a higher level of security and more efficient key management, but also the necessary flexibility for more dynamic use of space around the site. If needed, expansion of their system in the future is totally seamless: the CLIQ system’s reach can scale as the monastery’s needs evolve.

ASSA ABLOY invites attendees to visit booth #407 at ISC East 2026, November 3 - 5, at the Javits Center in New York City, to explore the latest innovations in its growing digital access portfolio. Attendees can connect with ASSA ABLOY experts and see solutions designed to address evolving security needs across a wide range of applications. “The strength of our partnerships with security professionals is essential to meeting the changing needs of the industry,” says Angelo Faenza, Head of Digital Access Solutions at ASSA ABLOY. “ISC East offers the opportunity to connect directly with the integrators and other security professionals that are shaping the industry every day. We’re committed to being there for our partners, ensuring everyone can count on us to help them navigate the new challenges and deliver the right solutions for the people and facilities they serve.” Discussing industry advancements Through its commitment to being Always There, ASSA ABLOY works directly alongside security professionals to understand their challenges and develop solutions that keep pace with the changing industry demands. At booth #407, attendees can connect with ASSA ABLOY experts in person, explore the company’s latest solutions, and discuss industry advancements and how ASSA ABLOY is supporting the change. Featured solutions at ISC East booth #407 include: Corbin Russwin and SARGENT LNK100 with Aperio® technology - Coming soon, the newest addition to ASSA ABLOY’s Aperio real-time wireless lock portfolio, the LNK100 helps extend centralized access control to interior and secondary openings without making every door a major infrastructure project. It supports a range of traditional and mobile credential technologies. ISC East attendees can get an early look at the LNK100 ahead of its commercial availability. Centrios Exit Trim – Built to bring modern access control to push-bar openings, the Centrios Exit Trim combines commercial-grade durability, mobile management, simple installation, and multiple credential options. Its innovation was recognized at ISC West 2026, where it won the SIA New Products Showcase Award for Best in Access Control Devices and Peripherals Hardware – Wireless. RITE Touch RT2050 – A standalone digital lock designed for swinging and sliding all-glass doors, combining a sleek surface-mounted design with PIN, fingerprint, and MIFARE credential options. The RT2050 brings flexible keyless access to offices, conference rooms, healthcare facilities, and other interior spaces. Securitech Red Button Locks - Securitech Red Button Locks bring immediate lockdown capabilities to schools and a wide range of security-sensitive environments. Designed to complement today’s evolving access and security strategies, these solutions provide a simple, intuitive way to secure an opening when seconds matter. Securitech can also work with customers to develop custom locking solutions tailored to the unique security requirements of their environment. DoorBird D22 IP Video Door Intercom - The next-generation DoorBird D22 combines advanced video communication, flexible access control, and seamless system integration in a modern architectural design for commercial, multifamily, and mixed-use applications. Control iD iDFace Max - Control iD iDFace Max brings facial identification and much more to the door. One device delivers face, card, PIN, and QR code access, a built-in SIP intercom for visitor calls, a customisable kiosk mode, and a 7-inch touchscreen, all rated IP65. SiteOwl - A physical security lifecycle management platform that connects system design, installation, device information, service history, and field operations in one environment, helping security teams and integrators manage projects and systems more efficiently. SHH Option for SARGENT PE80 Series and Corbin Russwin PED4000 and PED5000 Series Exit Devices. A new option designed to reduce operational noise at the opening while maintaining Grade 1 performance, giving security professionals a solution for applications where security and acoustics both matters. ASSA ABLOY experts will be at booth #407, ready to answer any questions and showcase these technologies.
Insights & Opinions from thought leaders at ASSA ABLOY Opening Solutions

There was a time when physical security and cybersecurity occupied two very different worlds. One was concerned with the nuts and bolts of locks, doors and perimeter protection. The other focused on networks, software and digital threats. Today’s modern access control systems – used in everything from offices and hotels to hospitals and data centres – combine the two, fusing mechanical engineering and cloud platforms. That means that a door is no longer simply a physical barrier. Instead, it’s a connected endpoint within a much wider digital ecosystem. And it’s changing expectations across the industry. Increasingly, developers, architects and operators are turning their backs on separate products in favour of integrated access solutions that combine doors, locks, access controls, environmental monitoring and digital management into a single, connected system. A new connected approach to security This change is part of a wider shift in the way that security itself is perceived This change is part of a wider shift in the way that security itself is perceived. Traditionally, physical security was about keeping unauthorized people out. Today, it’s about making sure the right people have the freedom to move within a restricted space. That is particularly important in places such as hospitals, data centres and other critical infrastructure, where security helps protect essential services while minimizing disruption. And it’s why our Research & Security Center (R&S) in Berlin, Germany, brings together both disciplines under one roof. Their job is to test products against both physical attacks and cyber threats. Employing unconventional tactics Sometimes, that means employing unconventional tactics, such as using professional lockpickers to test the security and resilience of new physical products. While modern locks are still based on mechanical engineering, they are more advanced than they look. Improvements in design, materials, and manufacturing mean they are stronger, more reliable, and harder to tamper with. But there’s more to locks than just security. Some systems can even use the motion of inserting and turning a key to generate a small amount of electrical energy, which provides energy to power extra functions without wiring or batteries. This means they are not just standalone locks but can also be used as part of wider digital access systems. Bridging physical and digital security For instance, great strides have been made recently in terms of biometric authentication However, as everyone knows, digital systems have their own security risks, especially now that artificial intelligence (AI) is part of the emerging threat. This means the cybersecurity team needs to ensure that systems are robust enough to withstand a wide range of risks – from attempts to breach access platforms to phishing attacks – as well as other tactics designed to exploit human behavior. It’s here that researchers adopt a ‘hacker’s mindset’ to keep systems safe. And that means continuously testing, probing, and strengthening systems to identify vulnerabilities against existing real-world threats while also anticipating what might be around the corner. Mobile-based access control systems For instance, great strides have been made recently in terms of biometric authentication, including facial recognition and fingerprint scanning. Similarly, smartphones are increasingly being used to secure credentials for mobile-based access control systems. But improvements in technology also come with their own risks. For instance, For instance, AI-generated deepfake videos and voices are becoming more convincing, making it easier to trick people into giving access, sharing information or approving actions they should not. And as I alluded to earlier, criminals are now using AI and automated tools to identify weaknesses and exploit them much faster than before, sometimes with little or no human involvement. But it’s also true that it’s being used to bolster defences. Work is currently underway to use AI to analyze data in real time to identify unusual entry times, identify multiple failed authentication attempts, or spot any other anomalies that might suggest someone is trying to gain entry illegally. Modern access control Cloud-based platforms allow security teams to issue and revoke credentials remotely Increasingly, the value of modern access control lies not just in the hardware, but in the software that sits behind it. Cloud-based platforms allow security teams to issue and revoke credentials remotely, monitor activity across multiple sites and respond quickly to emerging threats. This makes security a real-time, always-on, continuously managed service rather than a collection of standalone products installed and largely forgotten about. The importance of regulation and compliance This is something that policymakers are aware of. In the European Union, for example, the EU’s NIS2 Directive relates to cybersecurity protecting network and information systems and significantly broadens both the scope and the obligations for compliance. It also takes an “all-hazard” approach to security, which means protecting not just digital networks and systems, but also the physical environments in which they operate. Similarly, the EU’s Cyber Resilience Act is designed to ensure that all digital products are safe from cyber threats. Its goal is to ensure that connected devices and software are built, updated, and maintained with security in mind, helping protect users in an increasingly connected world. And by introducing clearer requirements and standards, the CRA will help consumers and organizations identify products with strong security features and configure them more securely from the outset. Security by design Security can no longer be treated as something that is bolted on at the end of the development process In both cases, it is incumbent on vendors not only to meet or exceed these rules and regulations but also to keep customers, the wider industry, and other stakeholders informed about developments. For me, these regulations also reflect a broader shift in thinking. Security can no longer be treated as something that is bolted on at the end of the development process or addressed only after a vulnerability has been identified. Instead, it needs to be considered from the very beginning and maintained throughout a product's lifecycle. For manufacturers, that means continuously assessing risks, testing products against emerging threats and ensuring they remain resilient as technology and the threat landscape evolve. As I said at the beginning, the reason is simple. Today's buildings are no longer just bricks and mortar. They are connected environments where doors, locks, cameras, sensors and access control systems increasingly communicate with one another and with cloud-based platforms. You might want to think about that the next time you walk into a secure building.
A lot has been said about door security — from reinforced door frames to locking mechanisms to the door construction — all of which is crucial. But what security measures are in place beyond the perimeter door in case the worst happens and it’s somehow breached? Hopefully, many more levels of access control are in place to prevent, or at least slow down, a perpetrator’s ability to compromise protected assets. Additional interior layers Interior security measures must operate as an integrated, multilayered system that eliminates single points of failure. These inner protections safeguard not only the physical infrastructure but also the operational integrity, confidentiality, and availability of the systems housed within. Beyond simply preventing unauthorized individuals from getting inside, the goal is to create a controlled, monitored, and resilient environment in which every movement, action, and access attempt is verified, logged, and, when necessary, challenged. As modern buildings, data centers, and infrastructure sites host critical functions and potentially sensitive intellectual property, these additional interior layers become essential to protecting both organizations and their proprietary assets. Interior security controls One of the most important interior security controls is granular access segmentation One of the most important interior security controls is granular access segmentation. While a perimeter door may verify an individual’s right to enter the building, the interior should treat every room, cage, and corridor as its own security zone. Role-based access control and strict least-privilege principles should limit personnel to only the areas they absolutely require. For example, a network engineer may need access to routing equipment but not storage racks; a janitorial contractor might be allowed into shared hallways but not any equipment rooms at all. These access restrictions should be enforced using intelligent keys, biometric scanners, mantraps, and, at particularly sensitive locations, two-factor authentication. Segmenting access in this way limits the potential damage from a single compromised badge or insider threat and ensures that a single breach does not cascade into a total facility compromise. Low-light and infrared capabilities Biometric authentication within a building adds a layer of confidence beyond perimeter controls. Technologies such as facial identification help prevent the use of stolen, cloned, or borrowed credentials. These systems complement anti-tailgating measures, such as sally ports or mantraps, which ensure that only one authenticated person passes through at a time. Interior surveillance is another essential measure. High-resolution cameras equipped with low-light and infrared capabilities should cover every hallway, door, rack row, and logistical pathway. Camera feeds must be continuously recorded, and retention policies must align with regulatory requirements. Intelligent video analytics, such as motion pattern recognition and heat mapping, enable the detection of atypical behaviors — such as someone lingering near a cage they are not authorized to access or movement at odd hours. Physical tamper-detection mechanisms Cabinet security provides a vital layer of granularity in the access hierarchy, ensuring that even within secure facilities Integrating surveillance with access control systems creates a strong correlation; when someone successfully passes through a secured door and enters a room, the system can track whether the number of people seen on camera matches the number authenticated, and alert security if a discrepancy occurs. However, it is increasingly important that access control not stop at the room level, because the most sensitive assets are often housed in cabinets, racks, or storage units within already-secured spaces. Cabinet security provides a vital layer of granularity in the access hierarchy, ensuring that even within secure facilities, assets remain protected. Physical tamper-detection mechanisms on racks, cable trays, and server chassis add another dimension: they can detect if a panel is opened, a cable is unplugged, or a device is removed without authorization. Secure destruction protocols Another internal measure is the use of secure storage and chain-of-custody procedures for any components that contain intellectual property or personally identifiable information. Hard drives, backup media, and even printouts should be stored in locked cabinets accessible only to people with proper clearance. When decommissioning hardware, secure destruction protocols such as shredding or degaussing should be performed in controlled areas and thoroughly logged. Every movement of sensitive equipment should be traceable, from installation through end-of-life disposal. Such processes reduce the risk of data leakage from improperly discarded or undocumented devices. Consequences of improper behavior Staff should be trained to recognize social engineering attempts, unusual behaviors, and procedural deviations Operational security procedures also contribute significantly to interior protection. Background checks, ongoing employee vetting, and mandatory training ensure that individuals with access to sensitive areas understand their responsibilities and the consequences of improper behavior. Staff should be trained to recognize social engineering attempts, unusual behaviors, and procedural deviations. Maintaining a strict visitor escort policy prevents non-employees from wandering unobserved. All visitors should wear highly visible identification badges and be monitored continuously by authorized personnel. The building's interior should be treated as a controlled environment at all times, not merely a workspace. Continuous auditing and logging form Continuous auditing and logging form another pillar of interior security. Access logs from intelligent keys, biometrics, video, and environmental systems must be stored securely and evaluated regularly for anomalies. Automated systems can flag irregular patterns, such as repeated attempts to access unauthorized areas or entering rooms at odd hours. Manual audits validate that the access control list remains accurate, that no inactive or former employees retain credentials, and that documentation matches reality on the floor. These logs are indispensable during investigations, compliance assessments, and incident response efforts. Interior security controls Security networks should be isolated from the main IT networks to prevent a cyber incident Finally, redundancy and resiliency must be built into interior security controls. Electrical power for access control, intelligent keys, biometrics, and video systems should be backed by secondary sources, generators, or uninterruptible power supplies. Security networks should be isolated from the main IT networks to prevent a cyber incident from disabling physical protections. The goal is to ensure that interior security remains functional even during outages, disasters, or cyber disruptions. Multilayered approach Together, these additional interior measures create a layered defense that makes a secure building, data center, or infrastructure site extremely difficult to compromise. Rather than relying on a single barrier at the entrance, the environment becomes an ecosystem of mutually reinforcing controls — physical, operational, digital, and procedural. This multilayered approach allows structures to maintain high levels of protection even as threats evolve, ensuring that the systems inside remain secure, resilient, and trustworthy.
In today’s connected world, attacks are more likely to target digital than physical entry points. From ransomware and firmware tampering to remote hijacking, AI-driven phishing and automated vulnerability discovery, the nature of threats is evolving rapidly, and no industry can afford to neglect them. As our industry has moved from mainly mechanical to increasingly digital solutions, we have long recognized the importance of constantly monitoring and assessing the risks we face. This means not only meeting mandatory regulations but also voluntarily adopting international standards such as ISO 27001, which protects data and systems through a structured and independently audited framework. Today’s fast-changing risk environment is also why the EU introduced the Network and Information Security Directive 2 (NIS2) – to raise the bar for cybersecurity across Europe. But what do measures like NIS2 and the Cyber Resilience Act (CRA) mean in practice? How does the rise of AI fit in? And most importantly, what should our industry be doing to stay secure in such an unpredictable digital landscape? The new regulations Compliance is not just about meeting regulations, it is also a competitive advantage NIS2 is reshaping cybersecurity expectations by setting higher standards to reduce risk, improve transparency, and protect data and services. Alongside it, the CRA introduces mandatory requirements for products with digital components. This makes “secure by design,” regular updates, and compliance checks essential before products can enter the EU market. For companies in our industry, responsibilities now extend well beyond internal systems. Organizations must also ensure that suppliers and service providers comply, with regular risk assessments forming a central part of the process. The consequences of falling short are severe, ranging from significant fines and audits to the potential withdrawal of products from the market. For our customers, the message is clear: security must be built in from the start. Compliance is not just about meeting regulations, it is also a competitive advantage. At ASSA ABLOY Opening Solutions EMEIA, security is part of our DNA. We embed these standards into everything we do, giving customers solutions they can trust to be compliant and resilient. The rise of AI Artificial intelligence is transforming the digital security landscape and it cannot be separated from the regulatory framework shaping our industry. With AI advancing rapidly and new regulations coming into force, we have established a digital compliance framework to stay ahead of the curve and use AI as an enabler for improving security and achieving compliance. On one hand, AI brings powerful benefits, including more intelligent monitoring, faster anomaly detection, and smarter tools for operational efficiency. These capabilities directly support NIS2 and the CRA, particularly in the areas of proactive risk management and incident response. AI and building cybersecurity standards On the other hand, AI introduces new risks. The attack surface is expanding and threats such as deepfakes and smarter phishing create serious threats that regulators are determined to address. Both NIS2 and the CRA emphasize continuous monitoring, transparency and accountability, principles that must now also guide the responsible use of AI. At ASSA ABLOY Opening Solutions EMEIA, we see AI not just as a risk to mitigate, but as a capability to strengthen resilience and trust. That is why we are embedding strong governance practices around AI and building cybersecurity standards into every stage of product development. By doing so, we help our customers align with new regulations while ensuring AI serves as a tool for greater security and confidence. Trust and compliance Beyond our own operations, we are also committed to supporting customers on their compliance journey At ASSA ABLOY Opening Solutions EMEIA, we are taking NIS2, the CRA and the rise of cyber-threats seriously, ensuring compliance and enhancing trust with all our customers. We have reinforced supplier oversight, streamlined incident reporting, and embedded cybersecurity into every stage of product development and lifecycle management. Our teams also conduct ongoing risk assessments and post-incident reviews, ensuring that lessons are learned and improvements are made. By taking these steps, we not only meet regulatory requirements but strengthen the resilience of our supply chain and the trust customers place in us. Beyond our own operations, we are also committed to supporting customers on their compliance journey. Initiatives such as our recently released whitepaper “Enhancing Cyber–Physical Resilience with Digital Access Solutions” and a detailed NIS2 whitepaper developed in Germany last year provide clear, practical guidance. By showing what these regulations mean in practice and how intelligent access solutions can directly support compliance, we aim to make the path forward less complex and more achievable for our customers. Looking ahead The days when security threats to businesses and products were only physical are long passed. Today, we find ourselves in a world where the digital realm poses even more serious and constantly evolving challenges. It is therefore crucial that, as an industry, we take the necessary steps to meet the directives of NIS2 and the CRA and also constantly monitor the rise of AI. Only by doing so can we protect our customers, preserve our reputations, and build the trust that defines true leadership in security.