HackerOne - Experts & Thought Leaders


Latest HackerOne news & announcements
HackerOne, a global pioneer in Continuous Threat Exposure Management (CTEM), announces the upcoming integration of Anthropic’s Claude Mythos across select H1 Platform products: H1 Code Security Audit and H1 Code. The integration will make frontier cyber AI available in existing security workflows, connecting agentic vulnerability discovery with validation, prioritisation, and remediation. Enterprises are identifying possible exposures faster than ever, yet falling further behind on validating true exposure and making fixes. Frontier AI is widening that gap in both directions. According to H1 Platform data, critical vulnerability mean time to remediate (MTTR) improved by more than 50% over the past 12 months. Existing engineering workflows Over the same period, the unresolved critical backlog grew 29x. As frontier cyber AI increases the speed and depth of discovery, organizations need a scalable way to validate and prioritise what it finds. The H1 Platform harness will be available with Mythos through discovery of source code vulnerabilities with controls designed to improve coverage, validate model outputs, and bring validated exposures into existing engineering workflows. "Frontier cyber AI models can do one of two things to a security team," said Nidhi Aggarwal, Chief Product Officer at HackerOne. "It can hand them a longer list, or it can hand them a list they can act on. Which one depends entirely on what sits between the model and the security team. A harness helps turn model output into a validated exposure a security team can act on. We ran and validated the H1 Platform harness for ourselves before any customer saw it." Surface complex vulnerabilities On the discovery side, H1 Code Security Audit scans full repositories to surface complex vulnerabilities, including compositional vulnerabilities that can span years of commits and multiple authors, and H1 Code reviews pull requests. “Attackers are already using frontier AI to find and exploit vulnerabilities faster than humans alone can respond,” said Kara Sprague, Chief Executive Officer at HackerOne. “Defenders need access to advanced cyber-capable models, with people accountable for the decisions those models inform and the actions those models take. Finding vulnerabilities faster matters only if organizations can validate, prioritise, and act on them.” Complementary layers of continuous security Frontier cyber AI is one layer of coverage. An elite community of security researchers provides another, bringing creativity, contextual understanding, and real-world adversarial expertise to complex attack chains, business logic flaws, and novel exploitation paths. Together, frontier cyber AI and human expertise provide complementary layers of continuous security. HackerOne does not use or permit use of confidential researcher submissions or customer vulnerability data to train, fine-tune, or otherwise improve generative AI models. The select H1 Platform offerings will soon be available with Mythos. Users can also read more about what HackerOne found running Mythos on its systems as part of Project Glasswing and learn more about the H1 Platform.
HackerOne, a global pioneer in Continuous Threat Exposure Management (CTEM), announces a partnership with OpenAI to make frontier GPT cyber models available in select H1 Platform products, H1 Code Security Audit, H1 Code, and H1 Remediation, to help teams find and fix vulnerabilities faster. GPT cyber models use is optional and enabled by the customer. The partnership addresses a growing challenge facing security leaders applying increasingly capable AI across the exposure management lifecycle to find vulnerabilities and exposures, validate which ones pose real risk, and help teams prioritise and remediate them. As frontier AI increases the speed and depth of discovery, the H1 Platform helps organizations turn that capability into measurable risk reduction. Exposure management lifecycle “AI is making complex attack paths increasingly discoverable, changing the risk calculation for every security leader,” said Kara Sprague, Chief Executive Officer at HackerOne. “Defenders have to assume that if an exposure exists, it will be found, and act before attackers do. That means building security programmes that continuously discover, validate, and eliminate risk, so organizations can move from reacting to threats to staying ahead of them.” Addressing that new risk requires connecting expanded discovery capabilities to the rest of the security lifecycle. “Frontier AI can significantly expand what defenders can discover, but findings must still be validated, prioritised, and translated into action,” said Nidhi Aggarwal, Chief Product Officer at HackerOne. “The H1 Platform can put frontier AI to work across the security lifecycle, finding and validating the exposures that pose real risk, tracing them to root cause, and giving teams a clear path to remediation.” Multi-model harness The H1 Platform multi-model harness can use OpenAI’s frontier cyber models through the Daybreak Defense Network to broaden coverage, validate outputs, and trace findings to root cause. Security teams receive each finding with a developer-ready fix plan designed to cut overall time to remediate. Frontier cyber AI is one layer of coverage. An elite community of security researchers provides another, bringing creativity, contextual understanding, and real-world adversarial expertise to complex attack chains, business logic flaws, and novel exploitation paths. Together, frontier cyber AI and human expertise provide complementary layers of continuous security. Improving generative AI models HackerOne does not use or permit use of confidential researcher submissions or customer vulnerability data to train, fine-tune, or otherwise improve generative AI models. The partnership builds on HackerOne and OpenAI’s work to strengthen cyber defense. HackerOne recently signed OpenAI’s “A call for collective action on cyber defense,” an open letter from organizations around the world calling for collective action to expand access to advanced defensive capabilities, share practical security expertise, and accelerate verified fixes. HackerOne is also a launch partner in Patch the Planet, an OpenAI initiative focused on using AI-assisted security research and human expertise to identify and remediate vulnerabilities in critical open-source software. To learn how frontier cyber AI is transforming Continuous Threat Exposure Management, register for their upcoming webinar, Outpacing the Attacker, on Friday, September 11, 2026, at 18:30 BST.
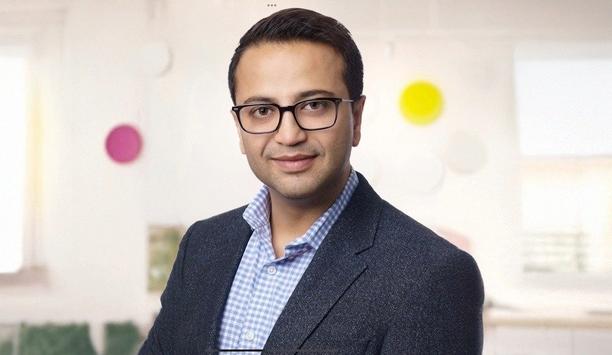
HackerOne, a pioneer in Continuous Threat Exposure Management (CTEM), announces the appointment of Naveen Bhateja as Chief People Officer. Bhateja joins the executive leadership team to lead the company's people strategy, leadership development and culture. Bhateja brings more than 25 years of experience building leadership and talent in global technology companies through periods of fast growth and change. At HackerOne, he will focus on developing the company's leaders, deepening its bench and helping employees grow as the business scales, strengthening the foundation beneath everything HackerOne builds for its customers and the researcher community. Strengthened executive capabilities "The pace of change in security has never been higher, and the organizations pulling ahead are the ones that invest as much in their people as they do in their technology," said Kara Sprague, CEO of HackerOne. "Naveen has spent his career guiding high-performing teams through exactly this kind of change. We're building an AI-native company where exceptional people grow together and shape the future of security." Bhateja has held senior people leadership roles at companies including Medidata, Juniper Networks, Amazon and JPMorgan Chase, where he shaped enterprise-wide talent and leadership strategies, organizational effectiveness, and strengthened executive capabilities during periods of significant business growth and change. “I have always believed talent is one of the greatest differentiators between good and great organizations because it unlocks everything else,” said Bhateja. “What drew me to HackerOne is that the company has built something genuinely difficult: a model where AI and human expertise make each other stronger. My role is to help build an AI-native organization that equips our people to move faster, innovate and deliver greater customer impact.”